
Enabling Okta SSO connections with your OVHcloud account
Learn how to associate your OVHcloud account with an external Okta service.
You can use Single Sign-On (SSO) to connect to your OVHcloud account. To enable these connections, your account and your Okta accounts have to be configured using SAML (Security Assertion Markup Language) authentications.
Requirements
- Being an administrator of an Okta service
- An OVHcloud account
- Access to the OVHcloud Control Panel
Instructions
For a service provider (i.e. your OVHcloud account) to establish an SSO connection with an identity provider (i.e. your Okta service), the key is to establish a mutual trust relationship by registering the SSO connection in both services.
Registering OVHcloud into Okta
Your Okta service acts as an identity provider. Requests to authenticate your OVHcloud account will only be accepted if you have first declared it as a trusted third party.
This means that it must be added to Applications.
Log in to the Okta administration interface with your administrator account.
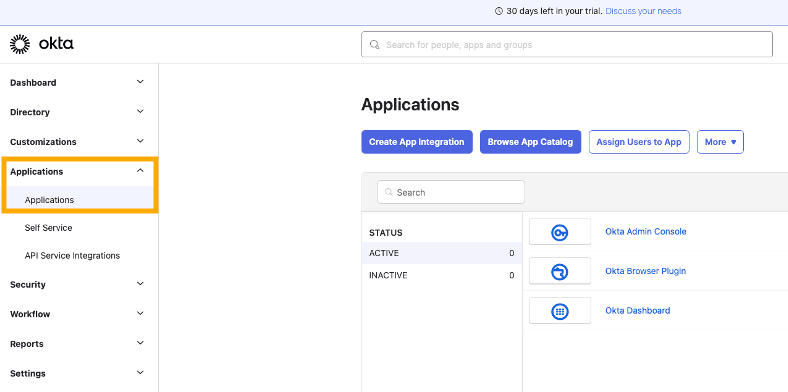
Go to Applications then again Applications.
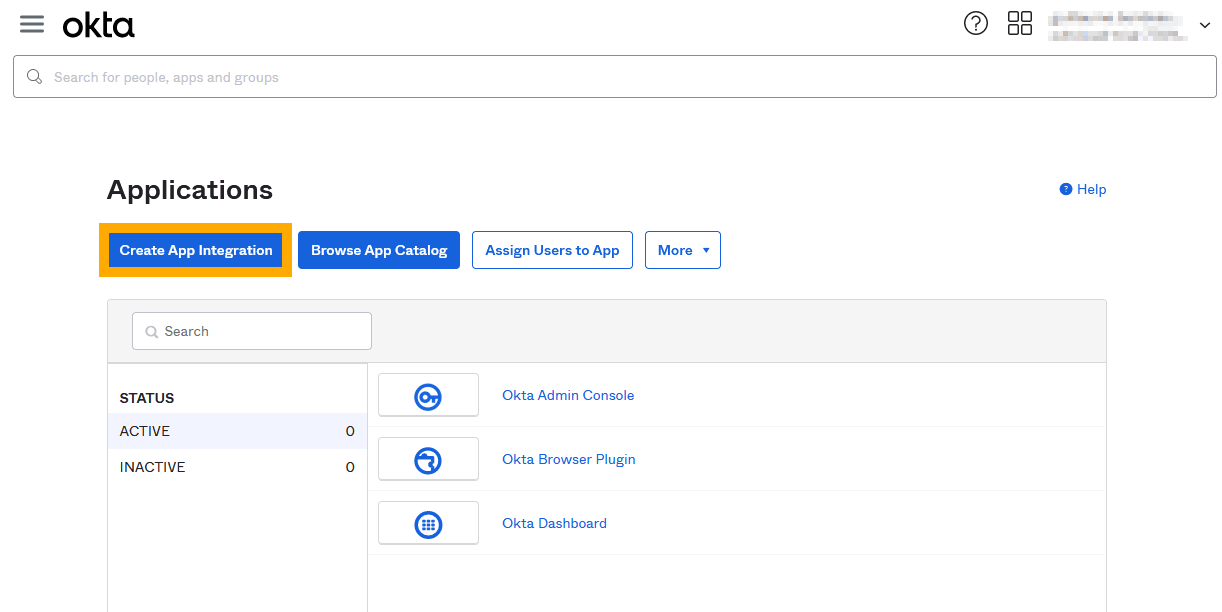
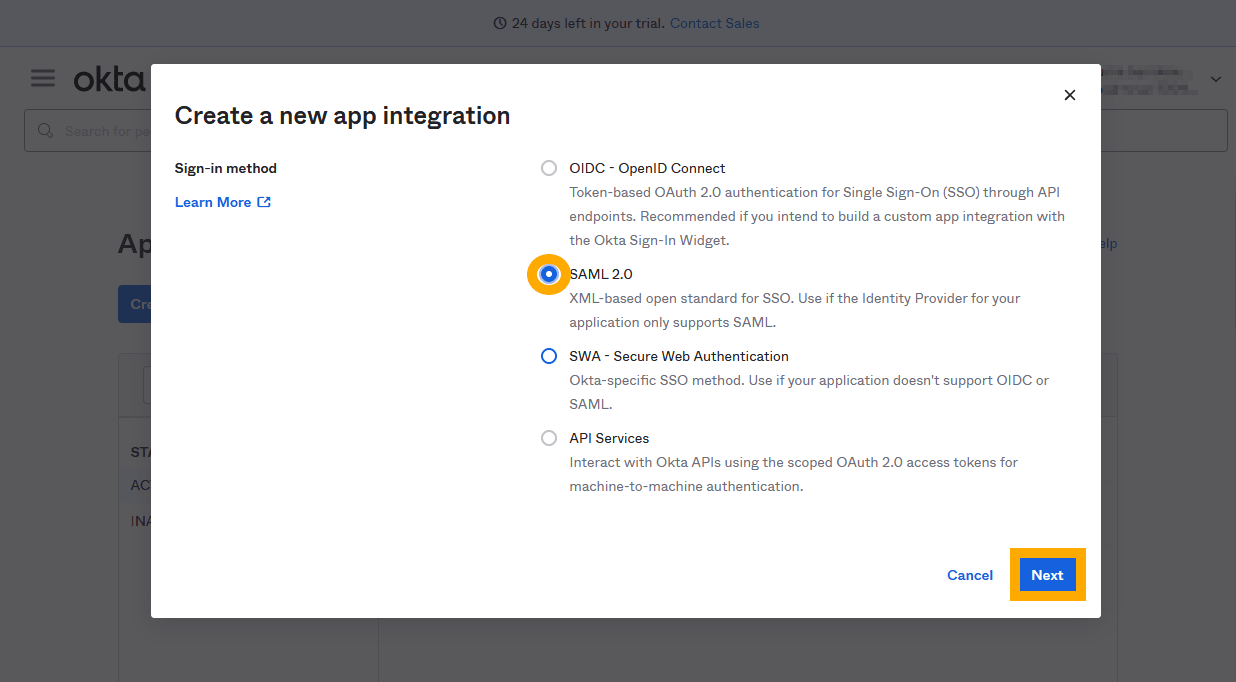
Click Create App Integration, select SAML 2.0, then select Next.
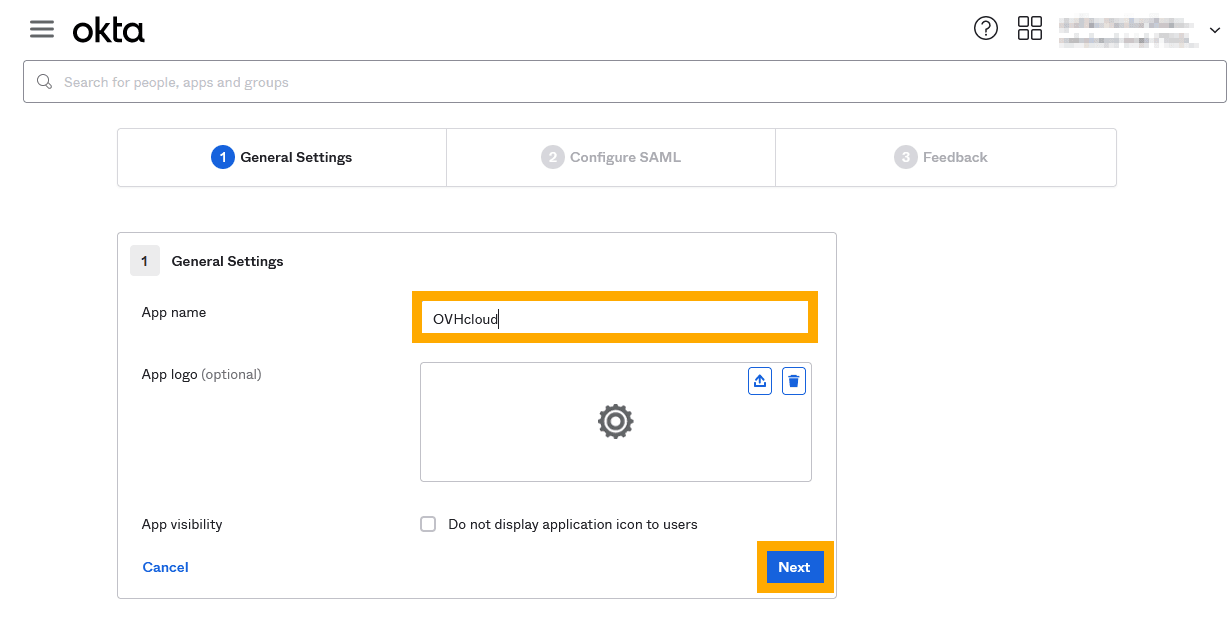
In the General Settings step, add a name for this application, such as "OVHcloud," and click Next.
In the SAML Settings step, complete the Single sign-on URL and Audience URI fields with the information below:
- Single sign-on URL:
https://us.ovhcloud.com/auth/and - Audience URI:
https://us.ovhcloud.com/auth/
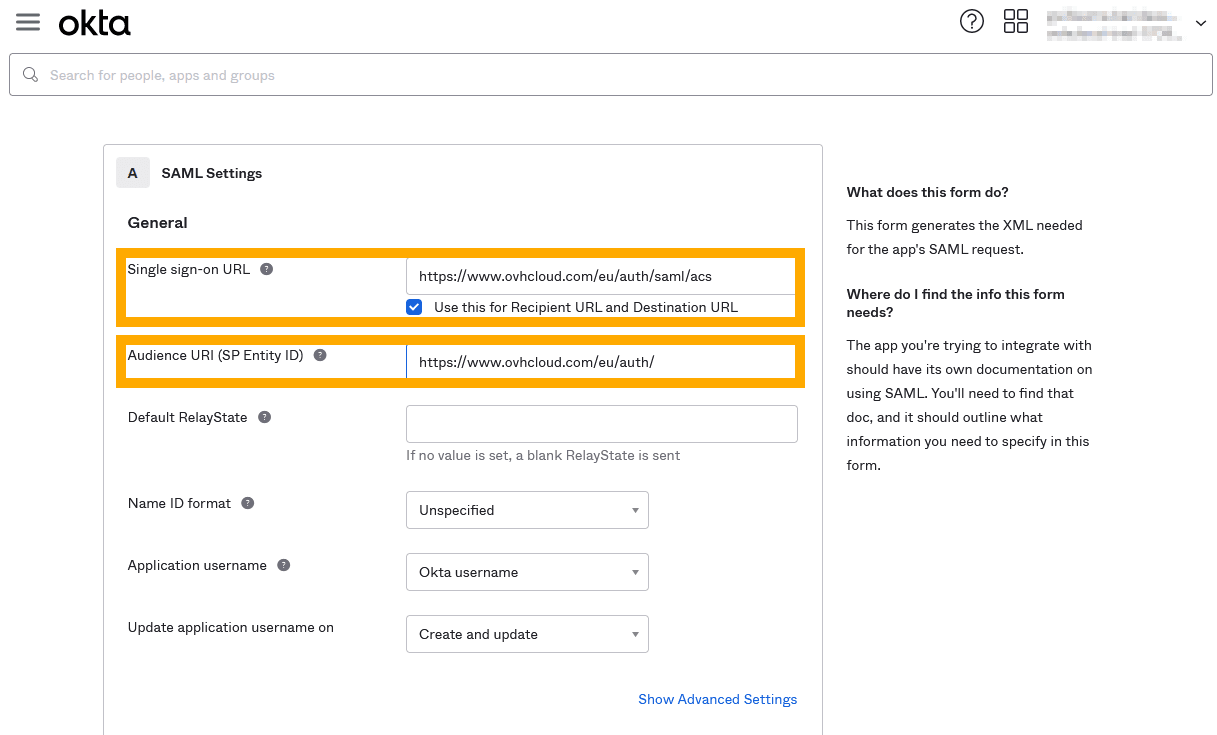
Then set the following Attribute Statements:
- Name:
http://schemas.xmlsoap.org/ws/2005/05/identity/claims/upnand Value:user.login - Name:
http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddressand Value:user.email - Name:
http://schemas.xmlsoap.org/ws/2005/05/identity/claims/nameand Value:user.displayName
Set these Group Attribute Statements:
- Name:
groupsand Filter:Matches regex:.*(Adapt the filter if you want to be more specific)
Click Next.
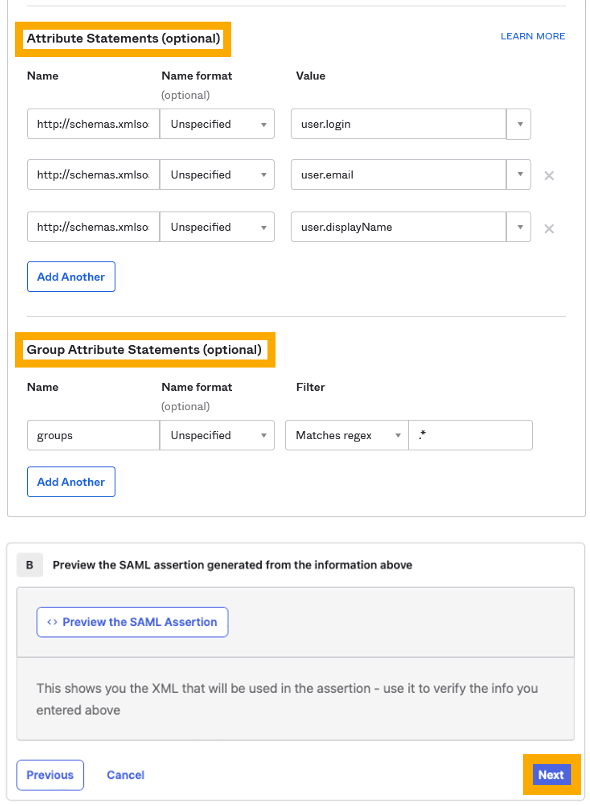
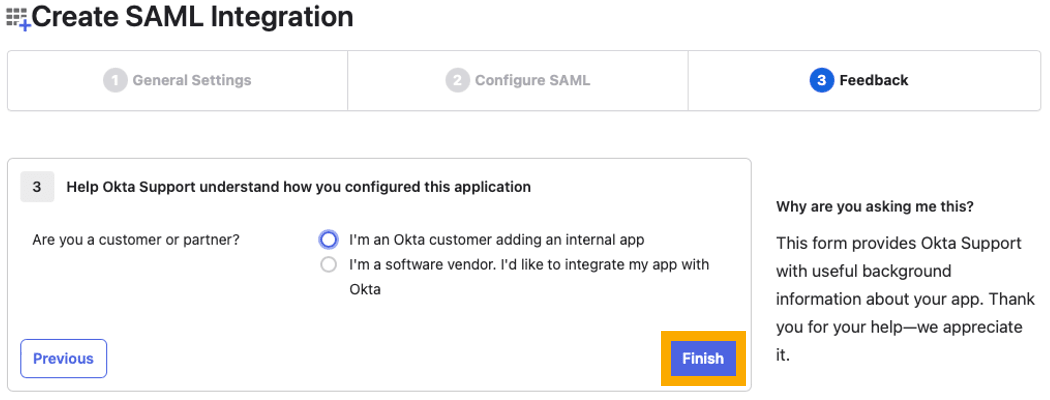
In the Feedback step, select the appropriate option and click Finish.
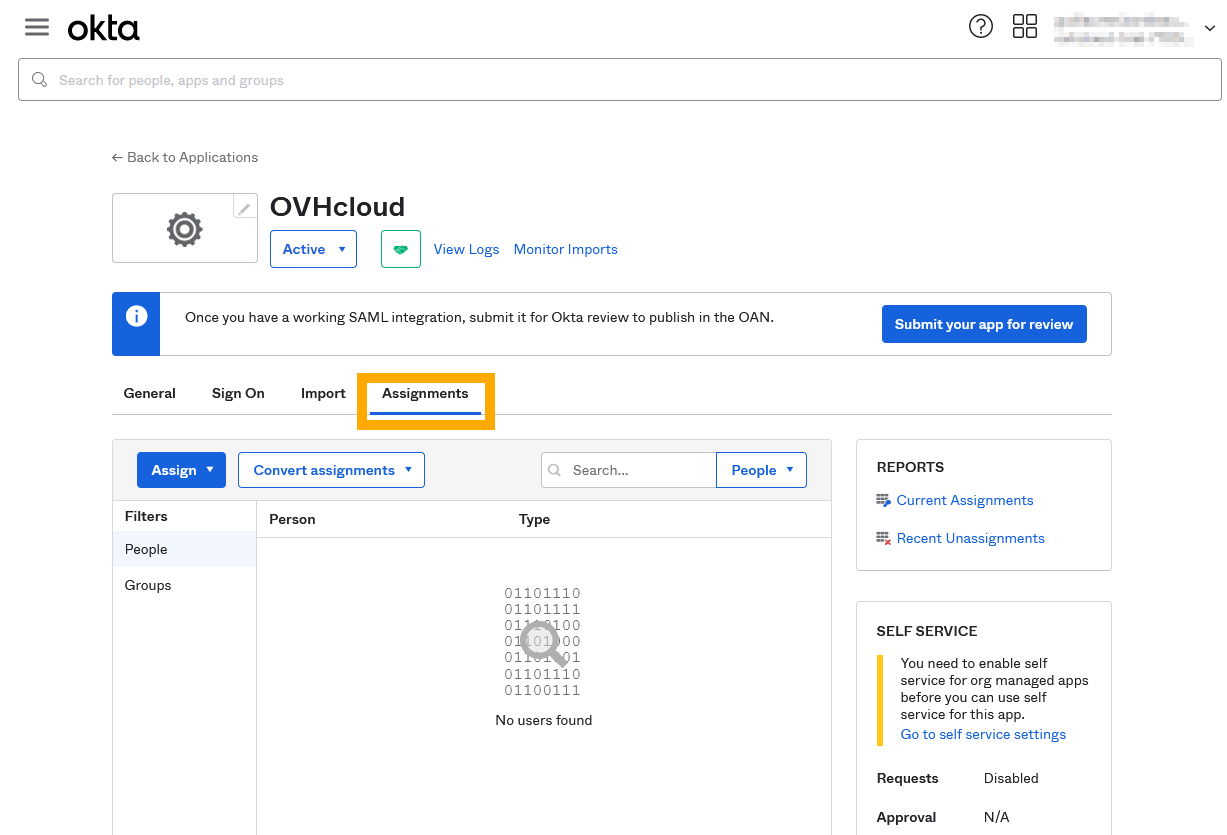
Then open the application, go to the Assignments tab, and assign users or groups to the application.
Before going to the next section, go to the Sign On tab, access the Metadata URL, and save the provided XML file.
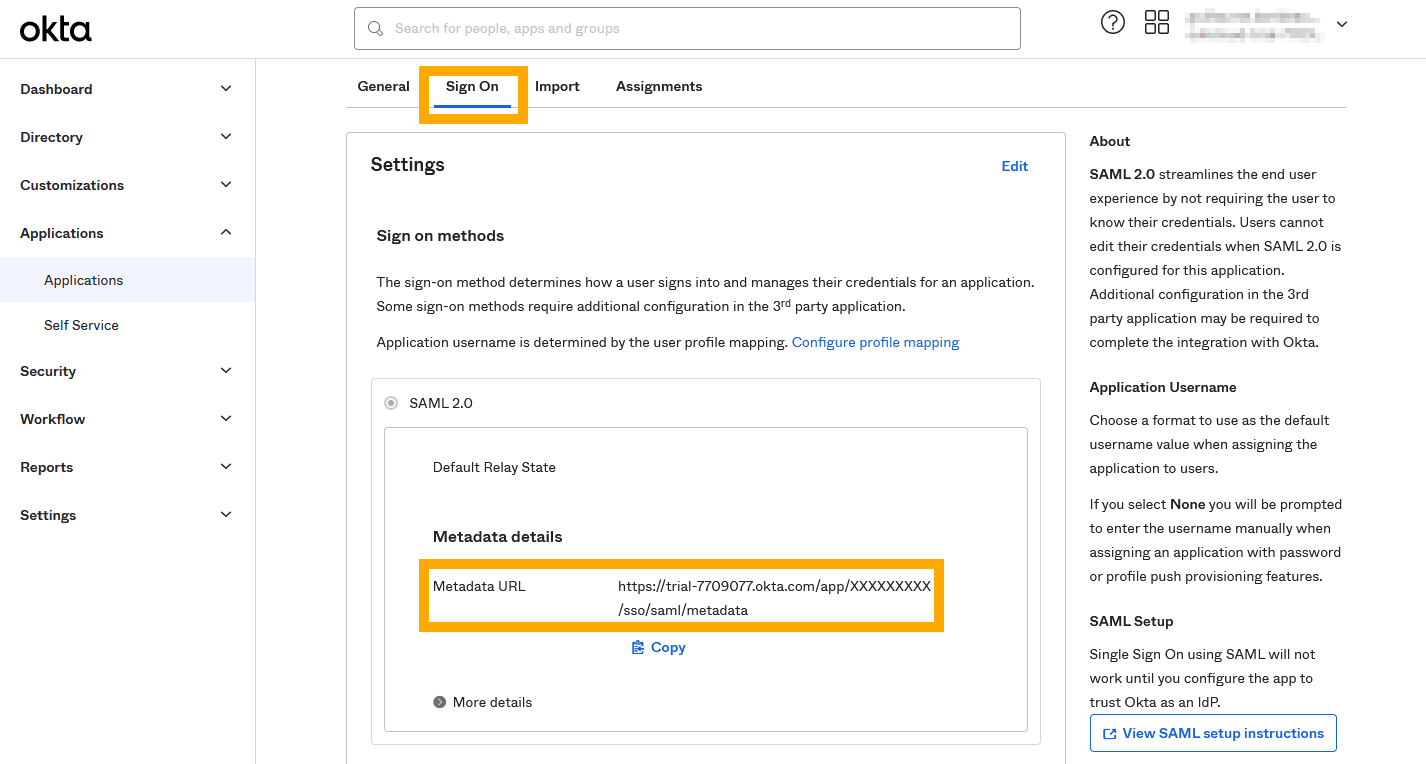
Your Okta service now trusts OVHcloud as a service provider. The next step is to ensure that the OVHcloud account trusts your Okta as an identity provider.
Registering Okta into the OVHcloud account and configuring the connection
To add Okta as a trusted identity provider, you must provide the identity provider metadata in the OVHcloud Control Panel.
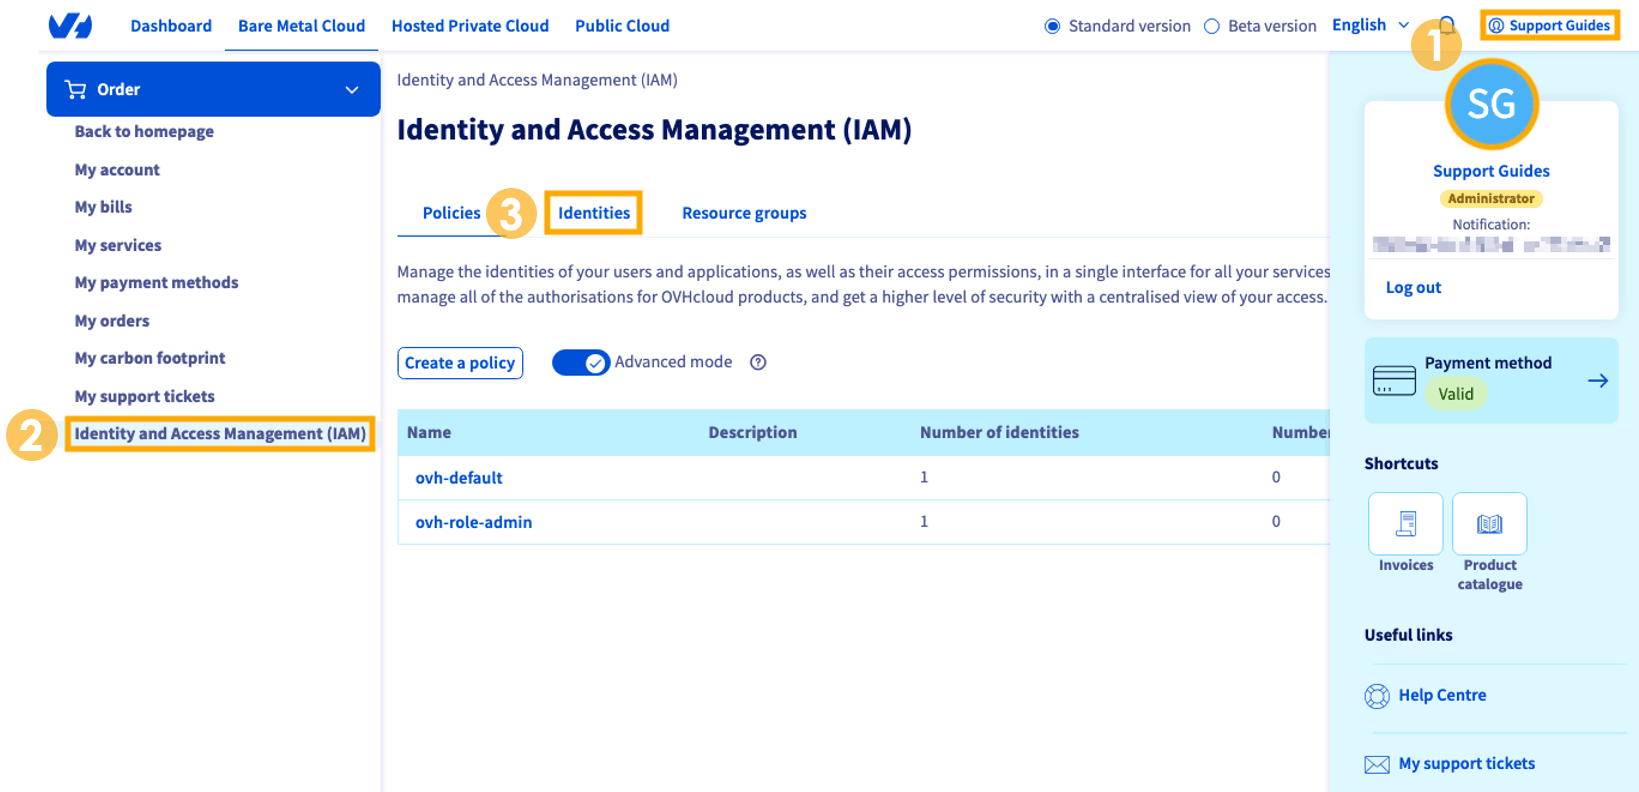
- Click your
nameand then yourinitials. - Select
Identity and Access Management (IAM)from the left-hand menu. - Click the
Identitiestab to access local users management.
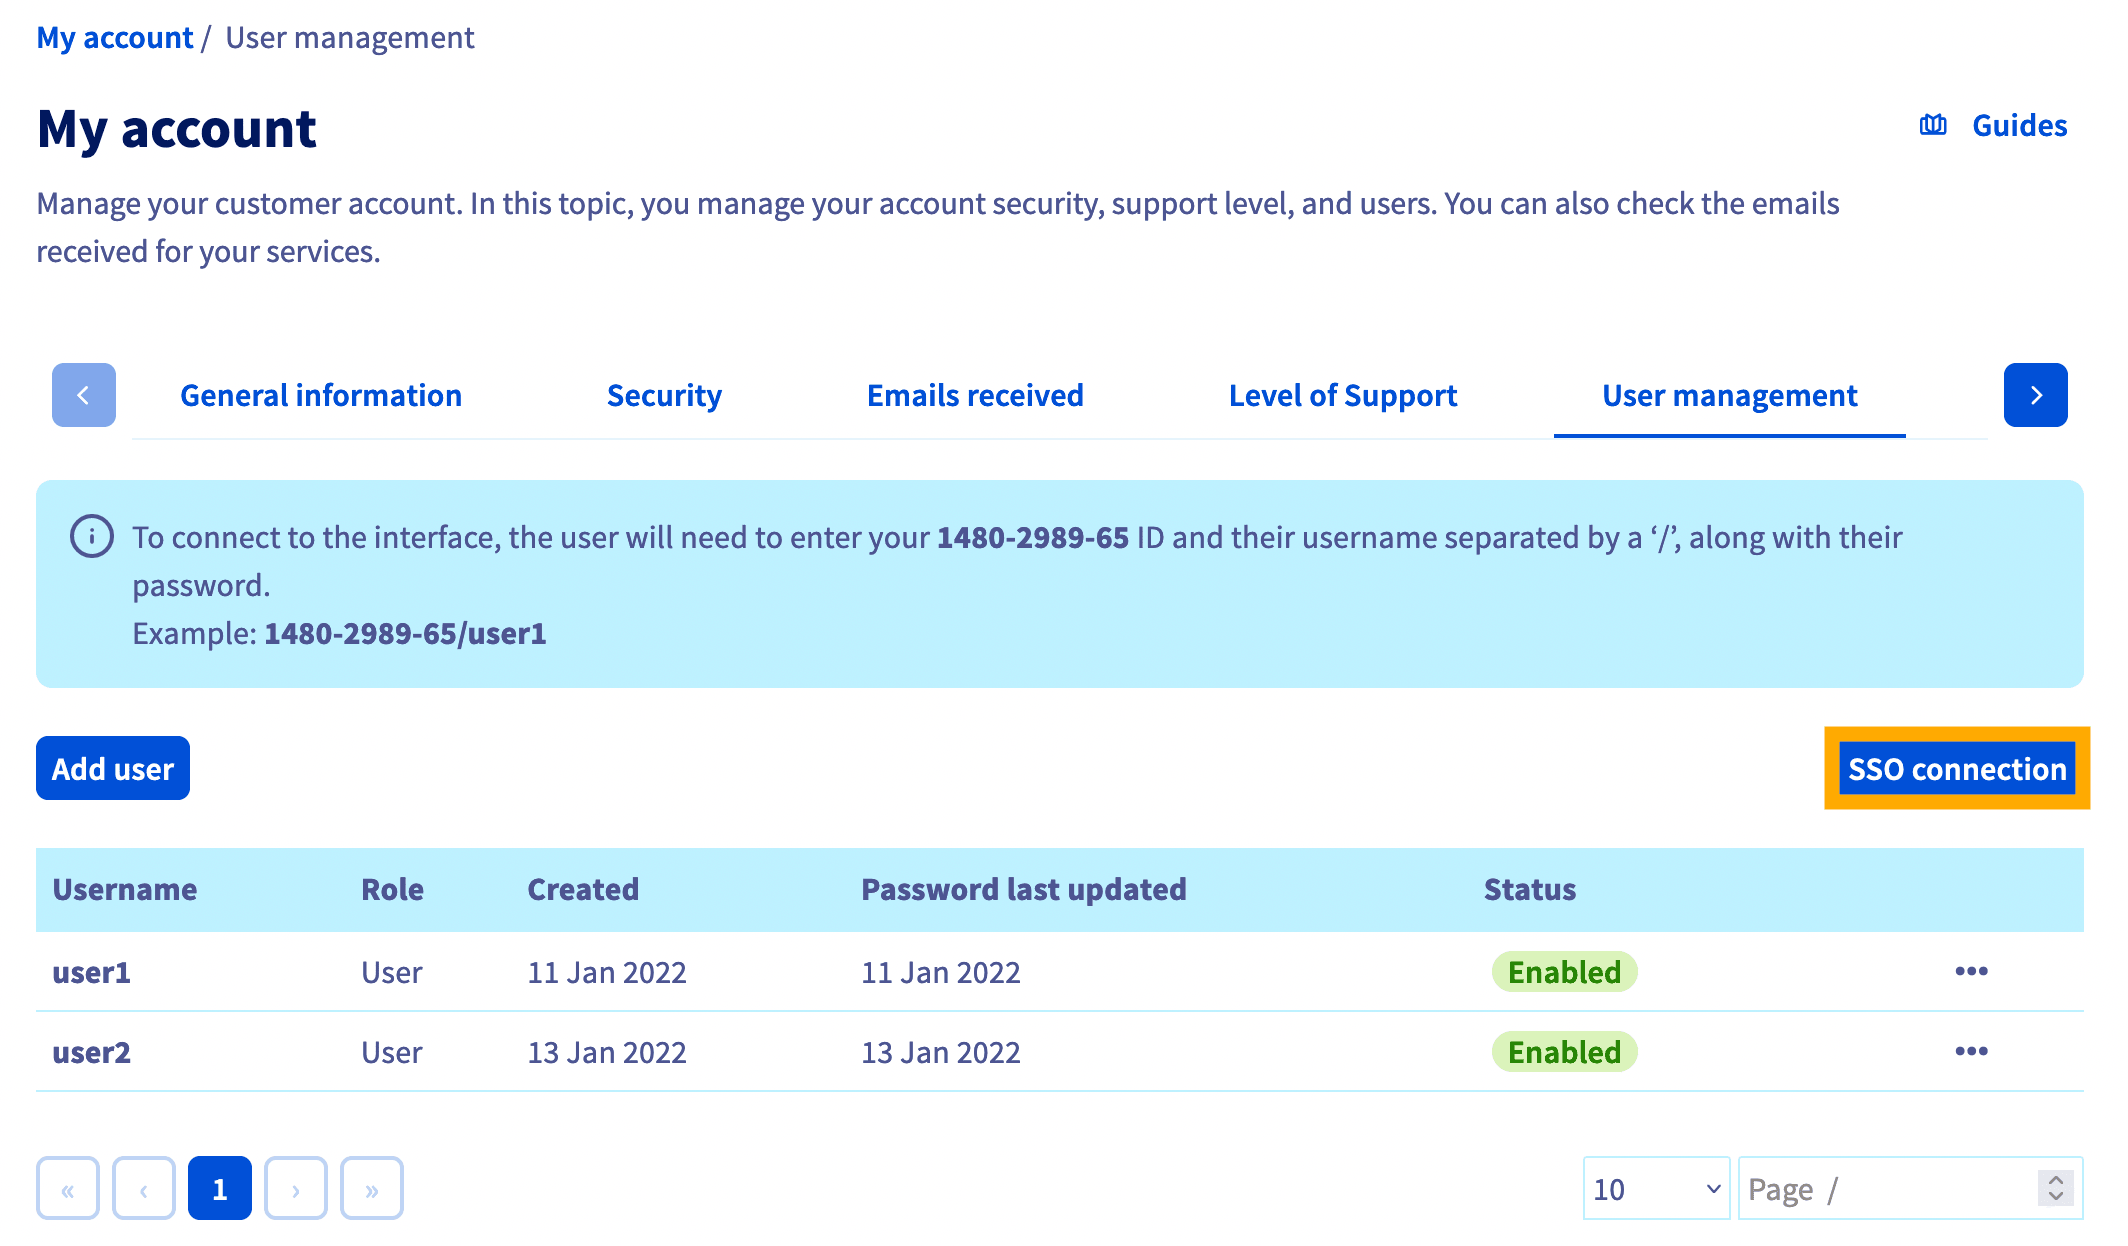
Click the SSO connection button.
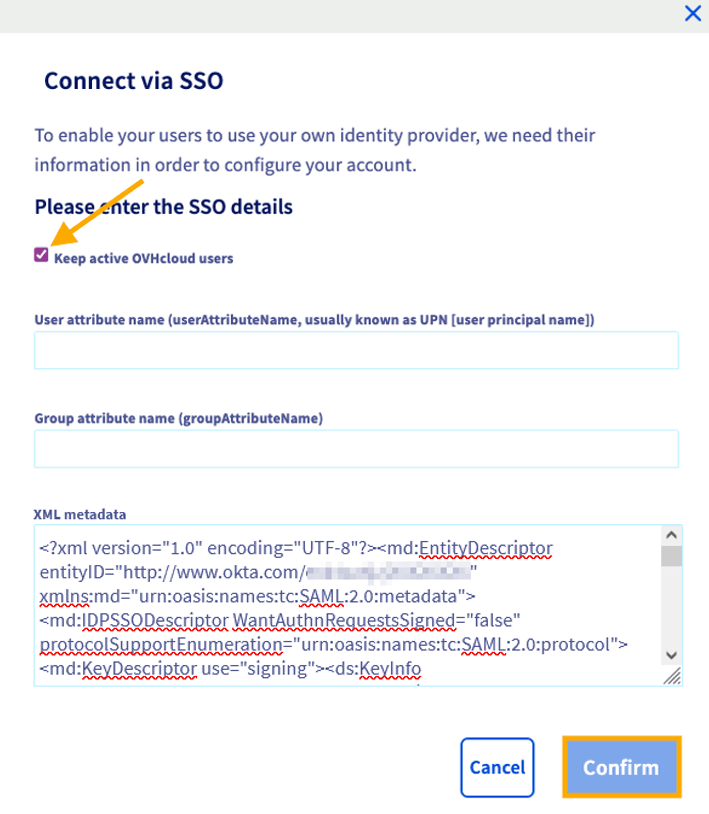
Fill in the XML metadata of your Okta service. Enter groups as the Group Attribute Name. Click on Confirm.
You can keep local users by ticking the Keep active OVHcloud users box.
Now you need to retrieve your Okta as the identity provider, as well as default groups.
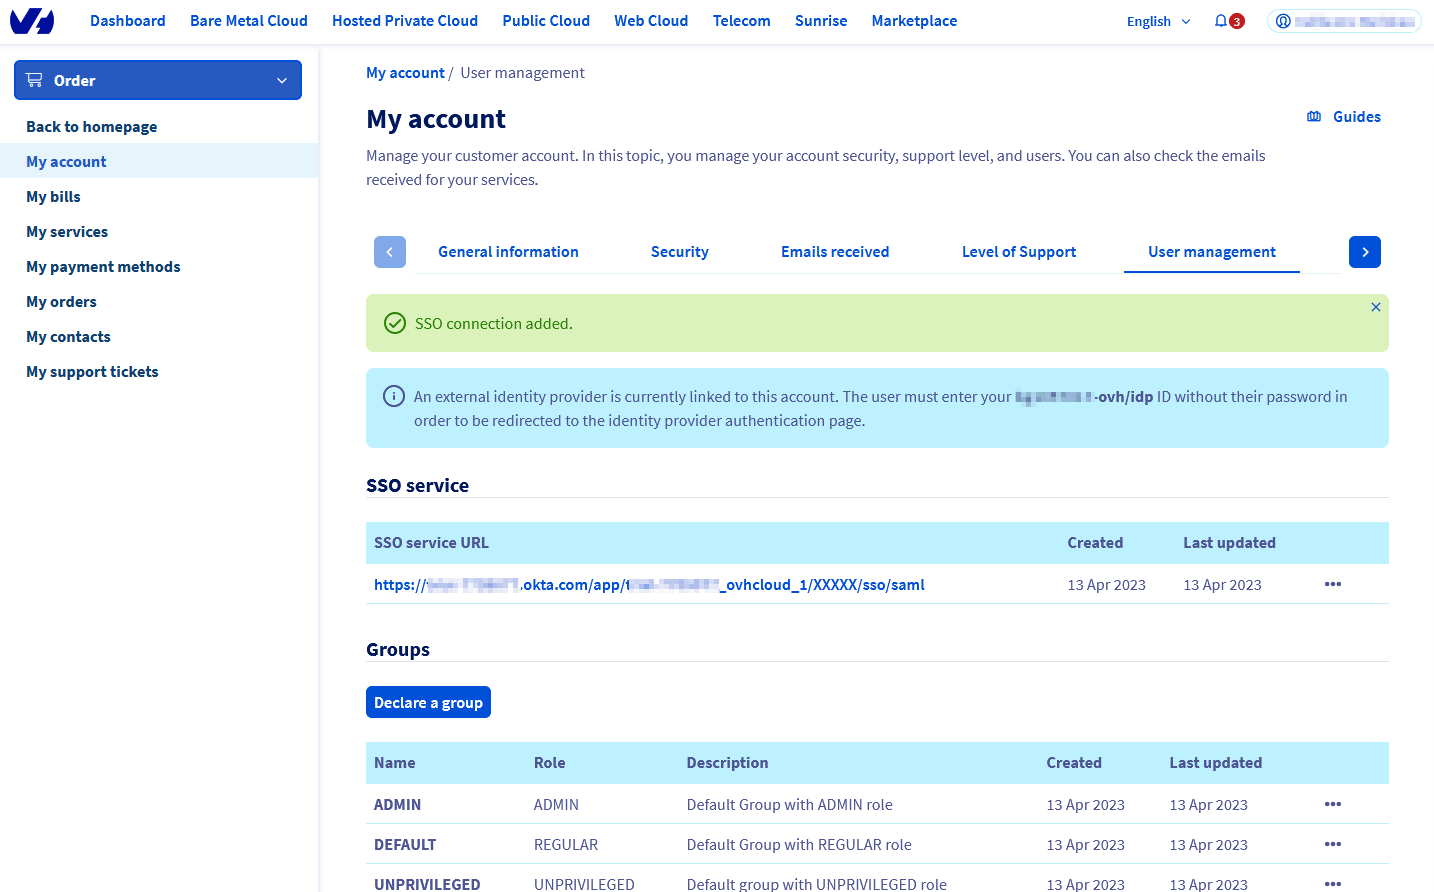
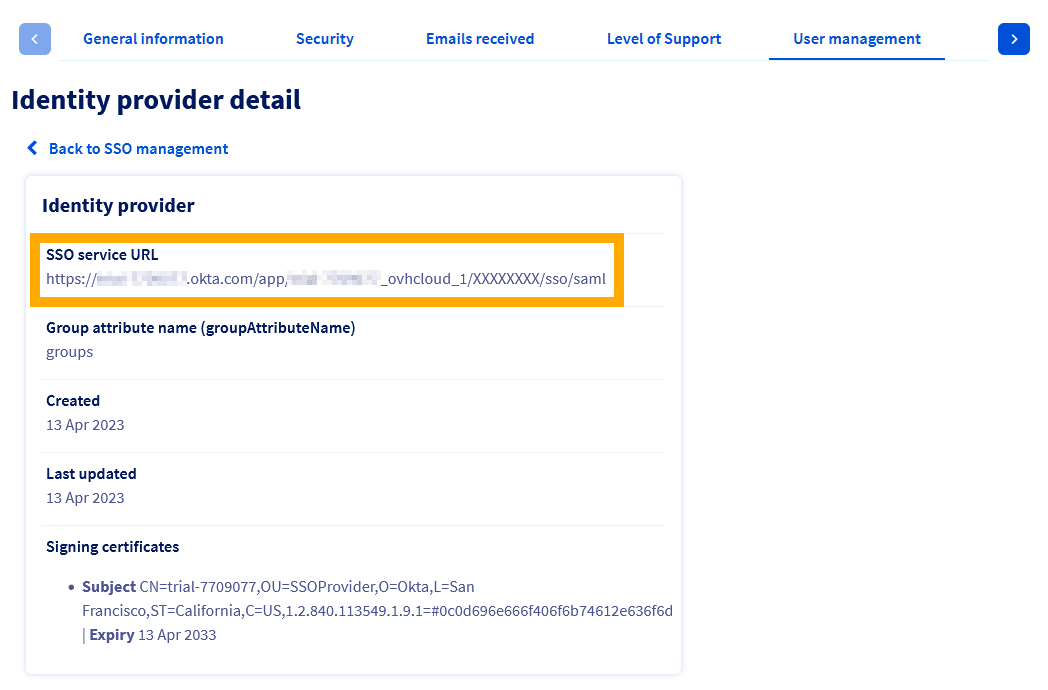
For more information, click on the link under SSO service URL.
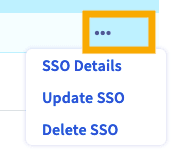
The more options ... button allows you to update or delete the SSO, and view its details.
Your Okta service is now considered a trusted identity provider. However, you still need to add groups to your OVHcloud account.
NOTE: If you try to connect via SSO at this point, you will probably receive a Not in valid groups error message.
That is because your OVHcloud account checks whether the authenticating user belongs to an existing group on the account.
You must then assign roles to Okta user groups at OVHcloud. Otherwise, your OVHcloud account does not know what the user is allowed to do and, by default, no rights are assigned.
From the OVHcloud Control Panel, add a group by clicking the Declare a group button and filling in the fields:
- Group name: Group name within Okta
- Role: Level of rights granted to this group
When finished, click Confirm.
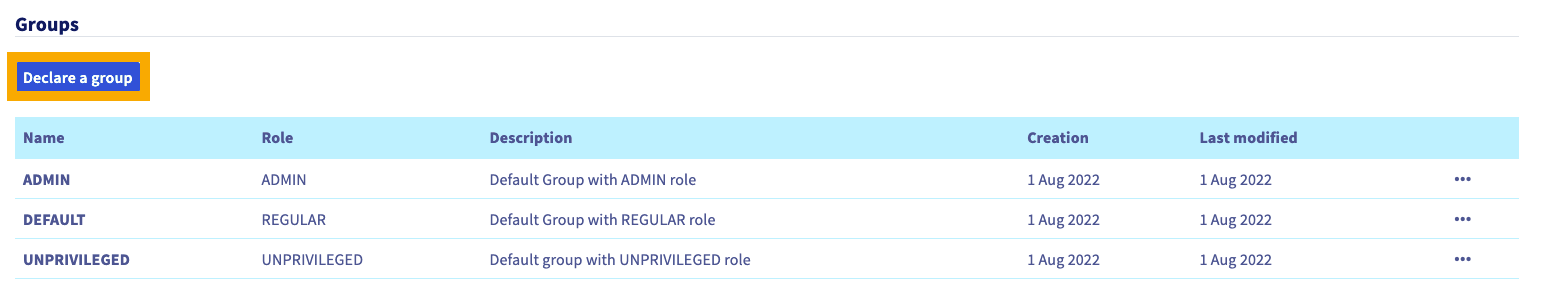
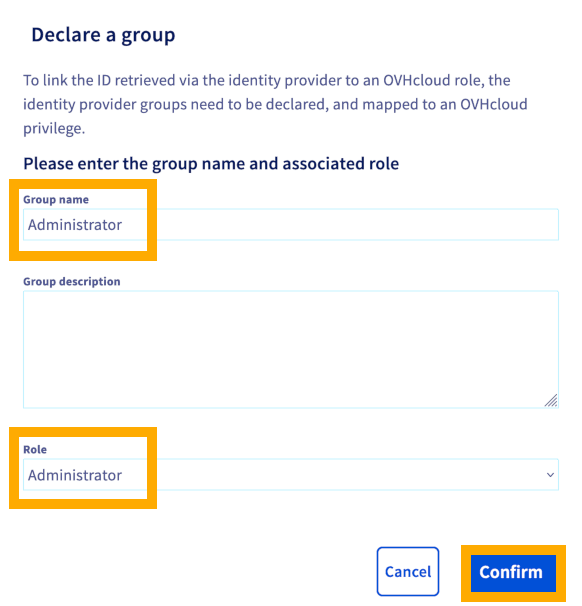
You can then verify that the group is added to your OVHcloud account in the "Groups" section:
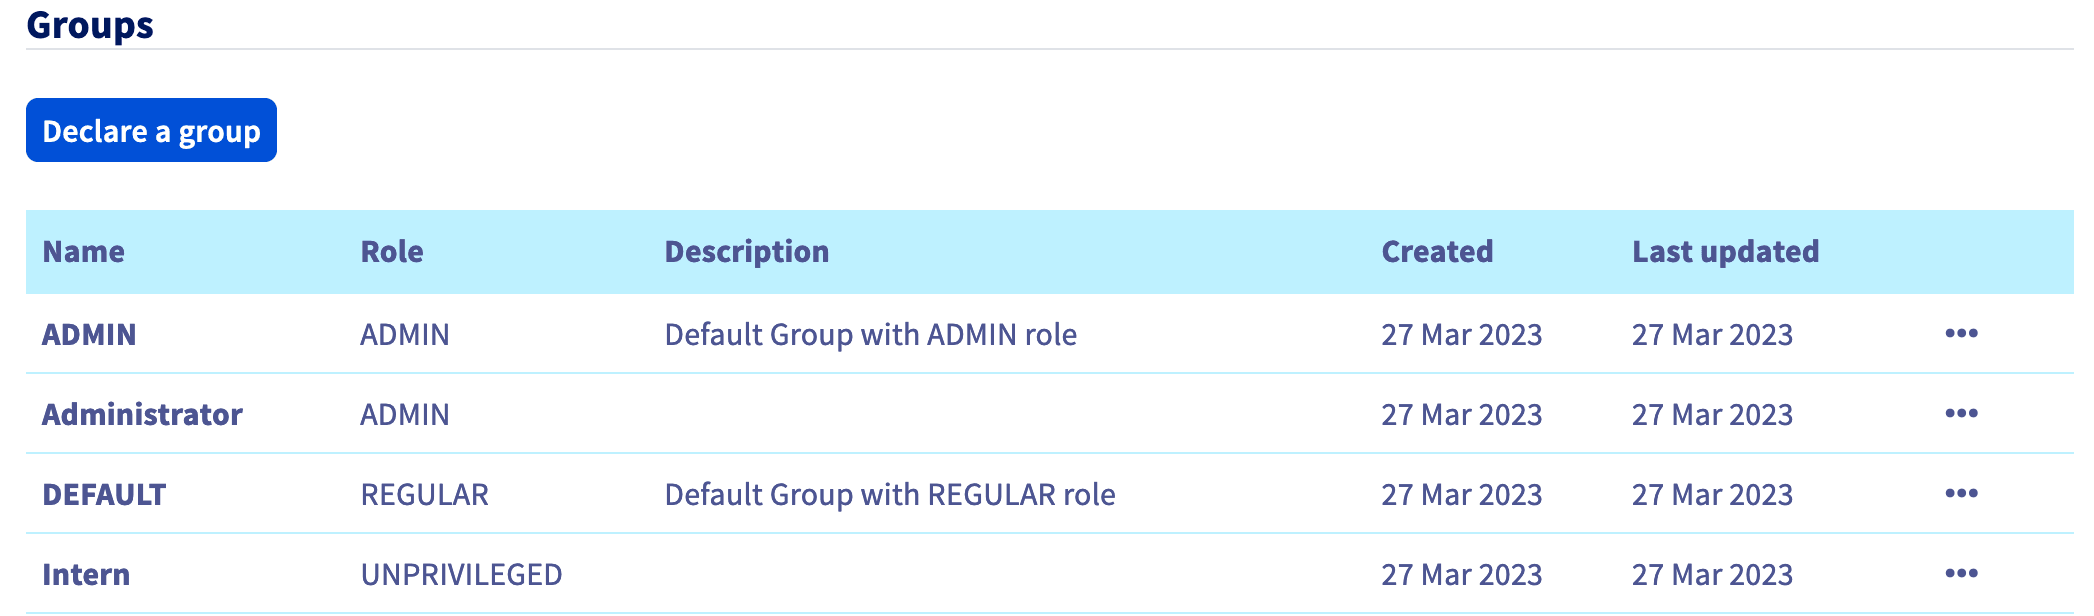
When you later log in with a user from the Intern group, your OVHcloud account will recognize that the user has the role "UNPRIVILEGED" specified by his group.
NOTE: If you set the privileges to NONE, you will need to assign permissions to this group via the IAM policies.
You will then be able to log out of your account and log back in with your Okta as an identity provider.
Connecting via SSO
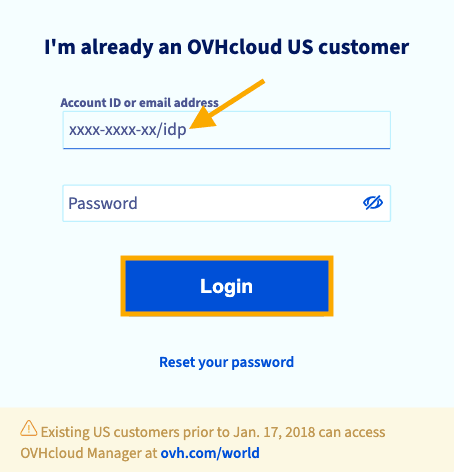
On the OVHcloud login page, enter your customer code followed by /idp without entering a password, and click the Login button.
You are then redirected to your Okta login page. Enter the login and password for a user of your Okta, then click the Sign in button.
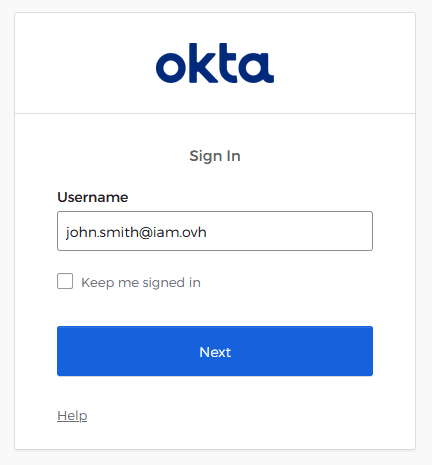
You are now logged in with the same customer code but through your Okta user.
Go further
Browse all the Account information guides.
Browse the rest of the OVHcloud US documentation for guides on our other products and services.