
Configuring the network on Proxmox VE on the High Grade, Scale, and Advance ranges
Learn two ways to configure an Additional IP on Proxmox VE: via the public interfaces and via the private interfaces (vRack).
The sections related to Advance range servers only apply to third-generation Advance servers powered by EPYC 4004 Series processors.
Older Advance generation servers do not rely on the same network infrastructure.
This article is about Additional IPv4 configuration on a public interface. You can also configure IPv6 addresses on your virtual machines using this guide.
Please note that Additional IP addresses can also be configured in a vRack (private network), which allows interconnection over a wide range of OVHcloud services, offering more flexibility.
Learn how to configure Additional IP addresses in a vRack without guides for IPv4 and IPv6.
NOTE: As of May 2025, virtual MACs can be used on High Grade & Scale ranges.
If you want to use virtual MACs to configure the network on Proxmox VE on High Grade and Scale servers, you can refer to Configuring Additional IPs in bridge mode on your virtual machines.
Instructions
Choose your method
Click one of the methods below to jump to instructions for carrying it out.
Additional IP in routed mode on public network interfaces: With this configuration, Additional IP addresses must be attached to a dedicated server. Suppose you have multiple Proxmox virtualization servers and you want to migrate a VM from one server to another. In that case, you must also migrate the Additional IP address to the destination server via the OVHcloud Control Panel or the OVHcloud API. You can automate this step by writing a script that uses the OVHcloud APIs.
Additional IP via the vRack: This configuration is more flexible as you do not need to associate an Additional IP with a server but with a vRack. This means that if you have multiple Proxmox virtualization servers, and you want to migrate a VM from one server to another, you do not need to perform any action on OVHcloud APIs. The only requirement is for all servers to be connected to the same vRack.
Collect environment data
How to find MAC addresses
From the OVHcloud Control Panel:
- Select
Bare Metal Cloudfrom the top navigation bar. - On the left-hand menu, select
Dedicated serversand choose your server. - Click the
Network interfacestab. - Locate the Private interface and take note of the MAC address.
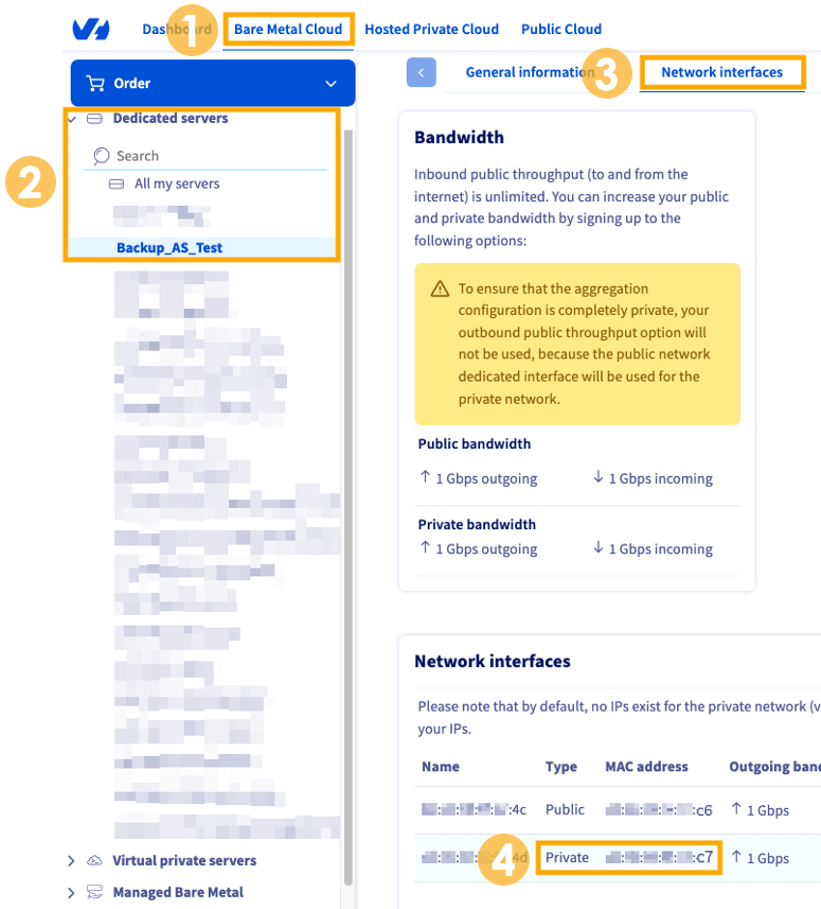
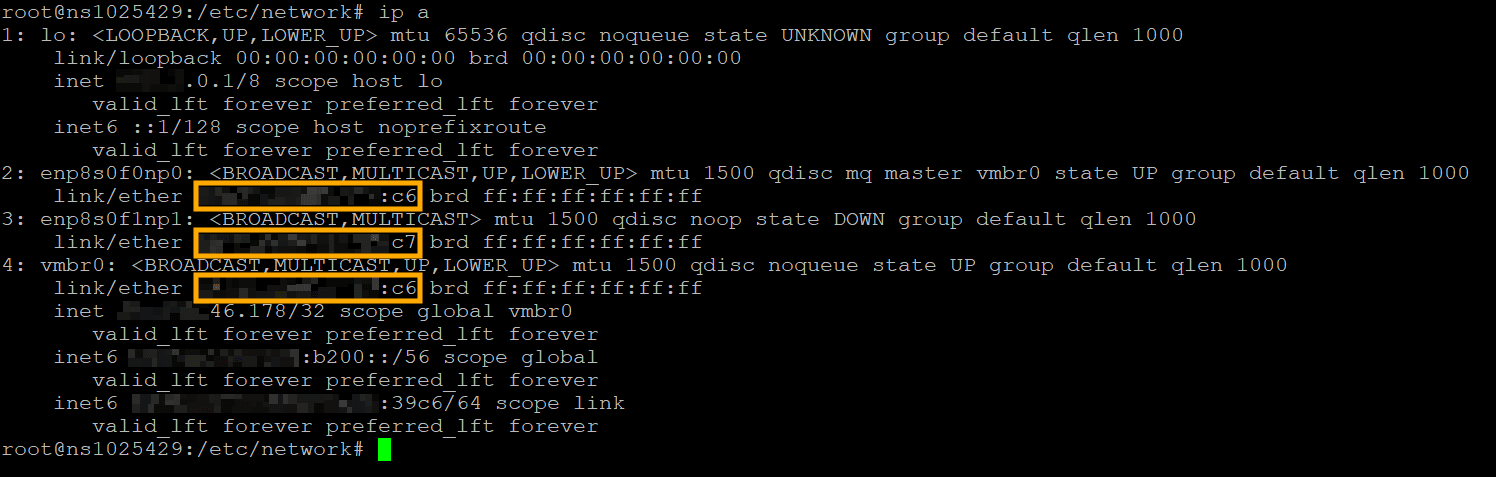
SSH into your dedicated server and run the following command to list all interfaces:
Example result:
Take note of the MAC addresses linked to each of the interfaces. These will help you identify your variables as well as the table below.
Determine assignable IP addresses
In IP blocks purchased from OVHcloud, the first, penultimate, and last addresses of a given IP block are always reserved for the network address, network gateway, and network broadcast, respectively. This means that the first assignable address is the second address in the block, as shown in the example below for the 46.105.135.96/28 block:
The subnet mask used in this example is appropriate for our block of Additional IPs. Your subnet mask may differ depending on the size of your block. When you purchase your IP block, you will receive an email with the subnet mask to use.
Attach an Additional IP block
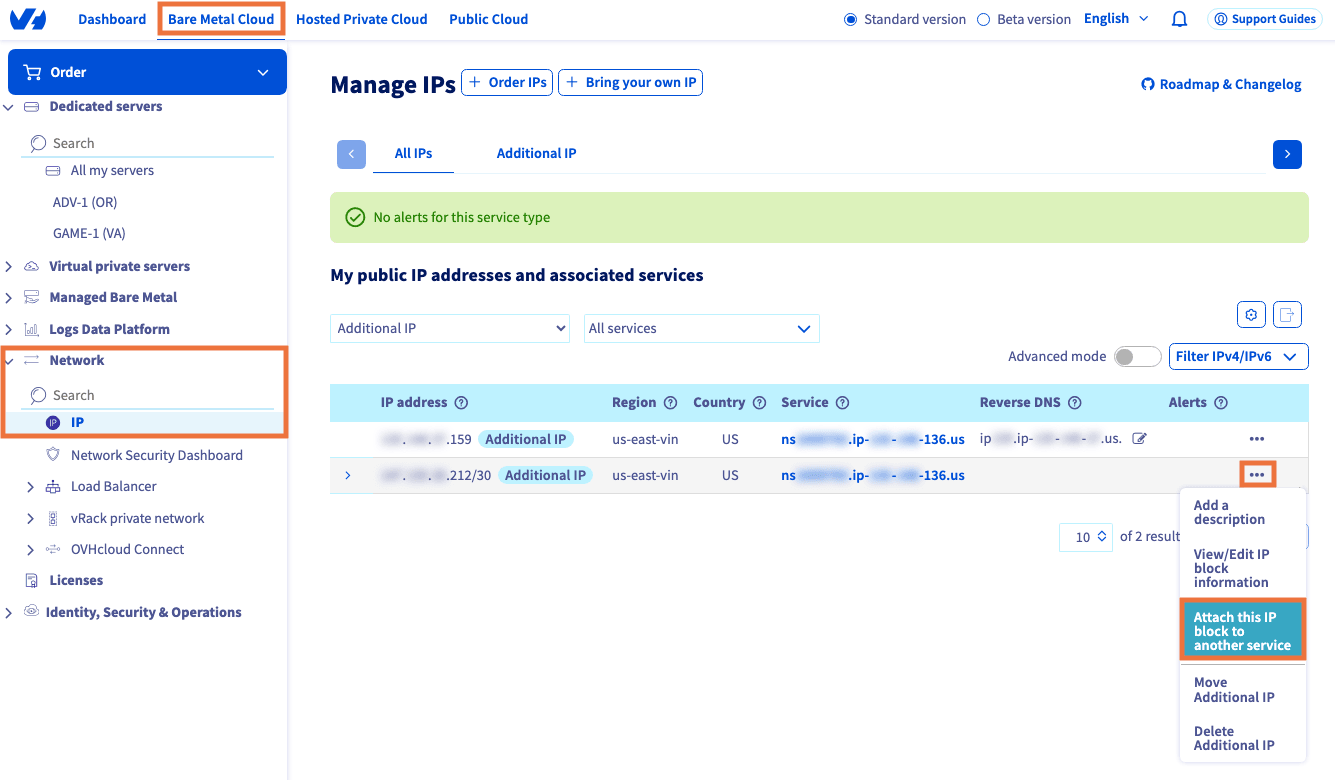
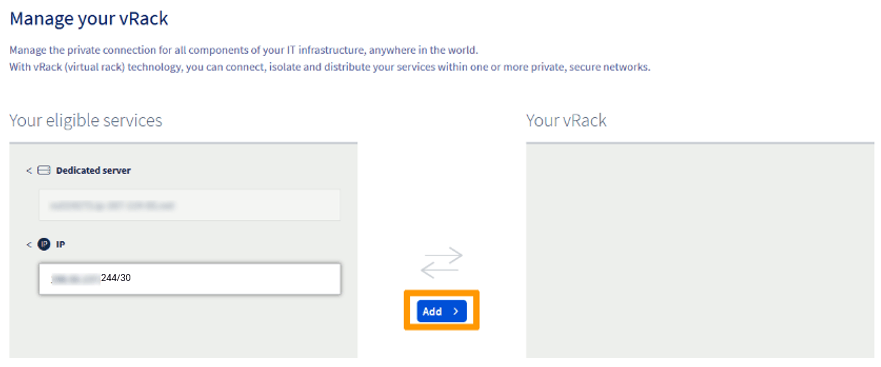
In your OVHcloud Control Panel, go to the Bare Metal Cloud section and click on Network. Next, open the IP menu.
Select the more options ... button to the right of your IP block, then click Attach this IP block to another service.
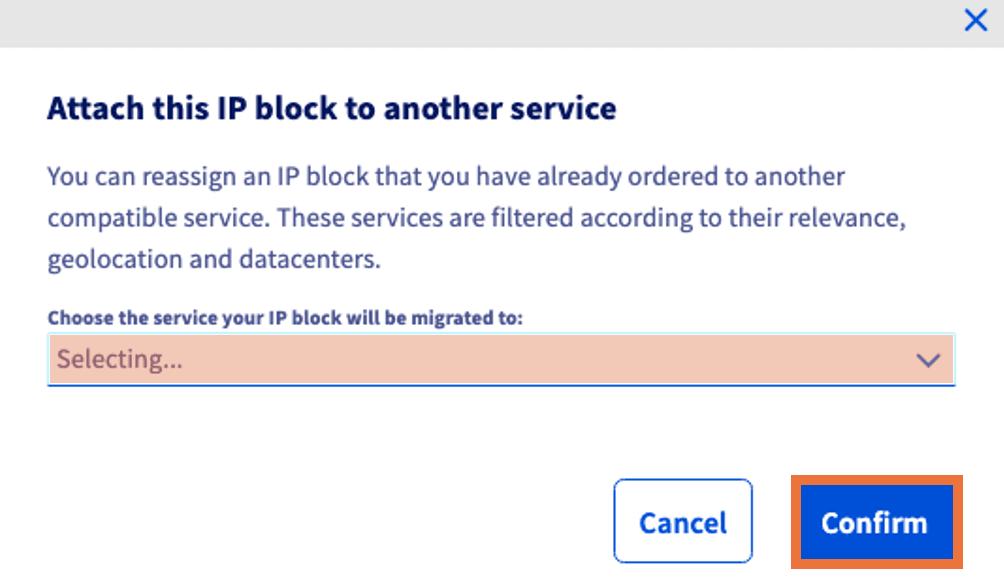
On the next screen, select a different service and click Confirm.
Method 1: Additional IP in routed mode on public network interfaces
With this configuration, Additional IP addresses must be attached to a dedicated server. If you have multiple Proxmox virtualization servers and you want to migrate a VM from one server to another, you will also need to migrate the Additional IP address to the destination server, via the OVHcloud Control Panel or the OVHcloud API. You can automate this step by writing a script that uses the OVHcloud APIs.
Requirements:
- An OVHcloud dedicated server
- One or more Additional IP addresses
- Access to the OVHcloud Control Panel
NOTE: No virtual MAC address must be applied to Additional IPs in the OVHcloud Control Panel.
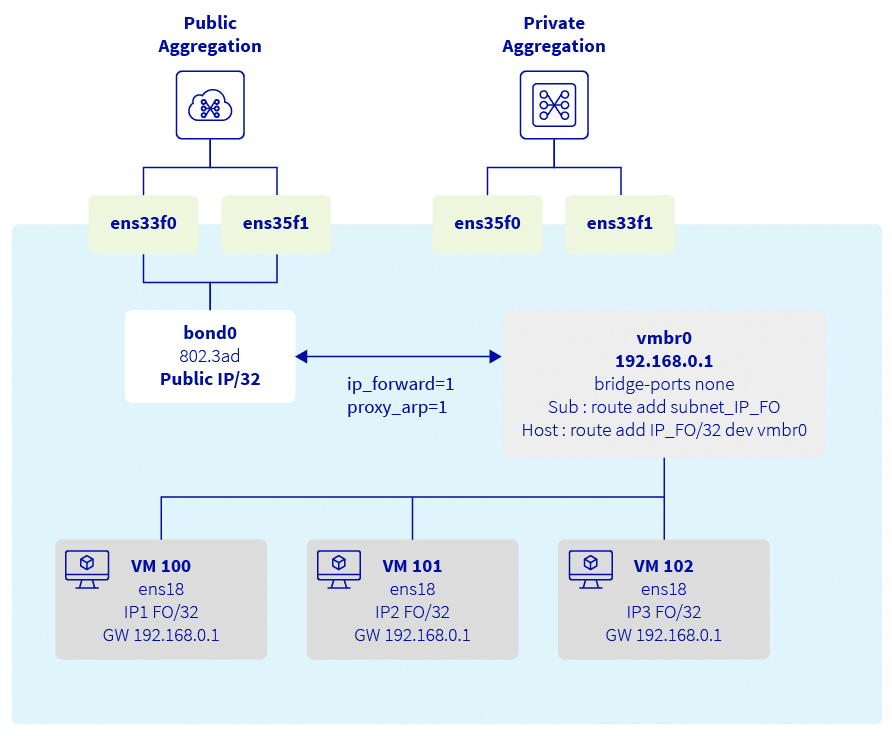
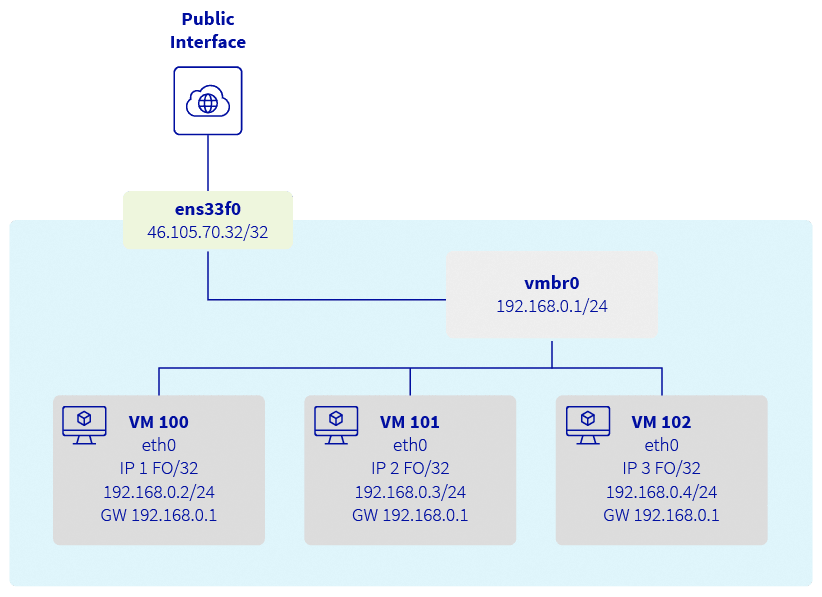
Target configuration schema
Click the tab for the type of server you are using.
Explanations
Proxmox is a Debian-based distribution that relies on ifupdown2 for network configuration. In this guide, the network configuration will be modified via SSH and not via the web interface.
We will:
- connect via SSH on Proxmox
- create a bond interface (only for the High Grade & Scale ranges)
- create a bridge interface connected to the bond
- allow packet forwarding between interfaces
- add routes to the additional IPs
Click each step to expand the full instructions.
Step 1: Log in to the Proxmox server via SSH
Log in to the Proxmox server via SSH:
Step 2: Allow packet forwarding
Enable the ip_forward sysctl parameter. To do this, we recommend modifying the sysctl.conf configuration file.
Add the following line to /etc/sysctl.conf:
Next, reload the sysctl configuration:
Step 3: Configure the network interfaces
At this point, restart the network services:
When the networking service is restarted, VMs are not added back to the bridge. This is because Proxmox disconnects each VM from the bridges and does not reconnect them. To force the VMs to reconnect to the bridges, you can restart the VMs.
Client VM configuration example
The VM must be attached to the vmbr0 bridge.
Contents of the /etc/network/interfaces file:
Step 4: Testing and validation
From now on, your virtual machines should be able to access the Internet from the additional IPs. They should also be reachable directly from the Internet using their additional IPs. The available bandwidth corresponds to the bandwidth available on your server's public interfaces and will not affect the private interfaces used for the vRack. This public bandwidth is shared with other virtual machines on the same host, as well as the Proxmox host itself.
To check your public IP, from the VM:
You need to restart the VM's network services for the configuration to take effect.
Method 2: Additional IP via the vRack
This configuration is more flexible as you do not need to associate an Additional IP with a server, but with a vRack. This means that if you have multiple Proxmox virtualization servers and you want to migrate a VM from one server to another, you do not need to perform any action on OVHcloud APIs. The only requirement is for all servers to be connected to the same vRack.
NOTE: This configuration only works with a block of additional IPs. It is not possible to use a single Additional IP (/32) directly in the vRack. To use an Additional IP, it must be configured on a public interface and cannot be directly integrated into the vRack.
Requirements
- A server compatible with vRack
- A vRack service
- A block of Additional IPs
- Access to the OVHcloud Control Panel
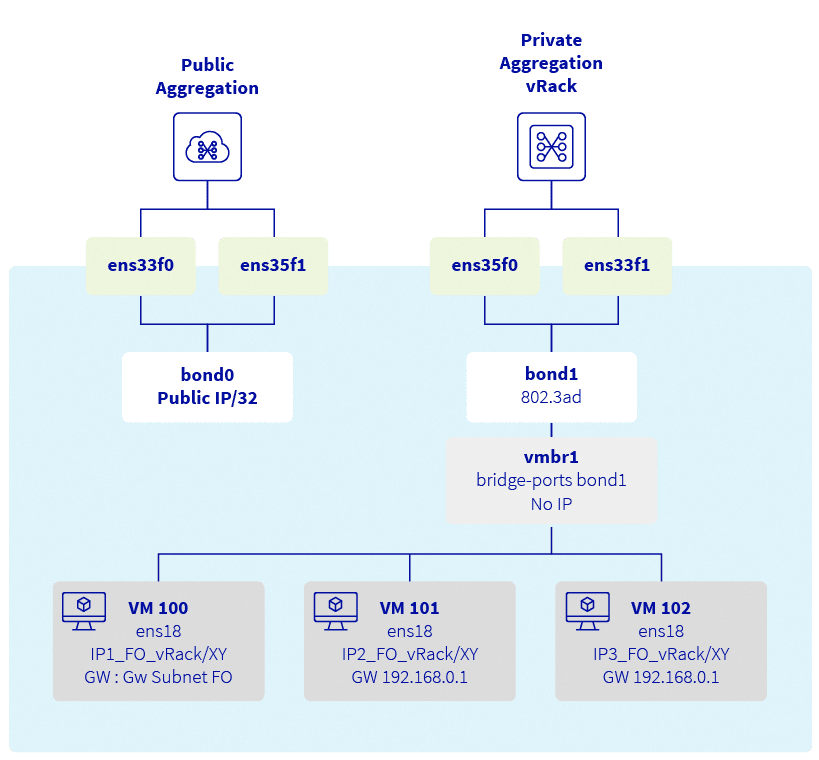
Target configuration schema
Explanations
Proxmox is a Debian-based distribution that relies on ifupdown2 for network configuration. In this guide, the network configuration will be modified via SSH and not via the Web interface.
We will:
- create a bond interface (only for the High Grade & Scale ranges)
- create a bridge interface connected to the bond
Click each step to expand the full instructions.
Step 1: Log in to the Proxmox server via SSH
Step 2 - Option A: Configure the network interfaces (command line)
At this point, restart the network services:
When the networking service is restarted, VMs are not added back to the bridge. This is because Proxmox disconnects each VM from the bridges and does not reconnect them. To force the VMs to reconnect to the bridges, you can restart the VMs.
Client VM configuration example
The VM must be attached to the vmbr1 bridge.
Contents of the /etc/network/interfaces file:
Step 2 - Option B: Configure the network interfaces (Proxmox interface)
You can also complete the configuration shown in Step 2 - Option A from the Proxmox web interface.
First, you need to create a Linux Bond (bond0 or bond1).
- Click
Datacenter,<Your Node>,System, and thenNetwork.
-
Choose
Createand selectLinux Bond.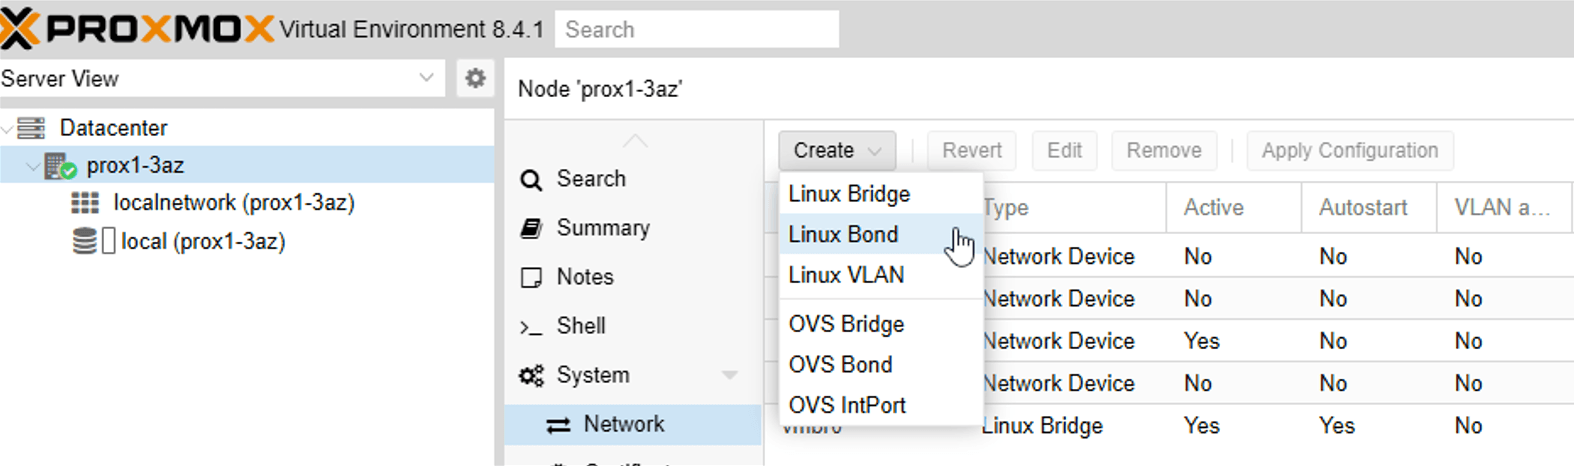
- Select the slave interfaces (e.g.,
ens3f1np1).
- Choose the bonding mode (e.g.,
802.3ad).
- Choose the hash policy (e.g.,
layer3+4).
-
Enter the Name
bond0(orbond1if you are creating multiple bonds).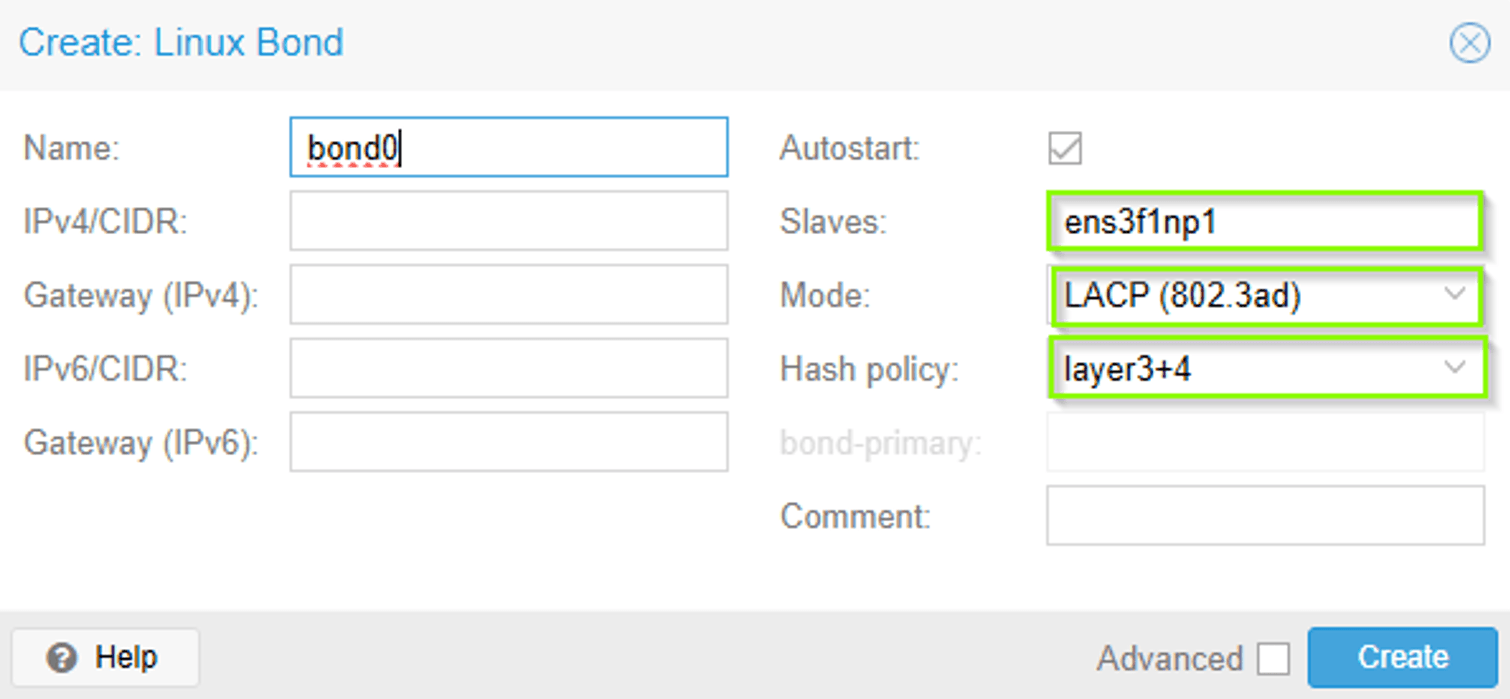
Next, you need to create a Bridge (vmbr0) to link to the bond.
-
Click
Createand selectLinux Bridge. -
Set the Bridge Port to the bond you created (e.g.,
bond0). -
Set the IP address, gateway, and netmask according to your configuration.
-
Enter the Name for the bridge (e.g.,
vmbr0).WarningNOTE: While creating the bridge, make sure
VLAN awareis marked.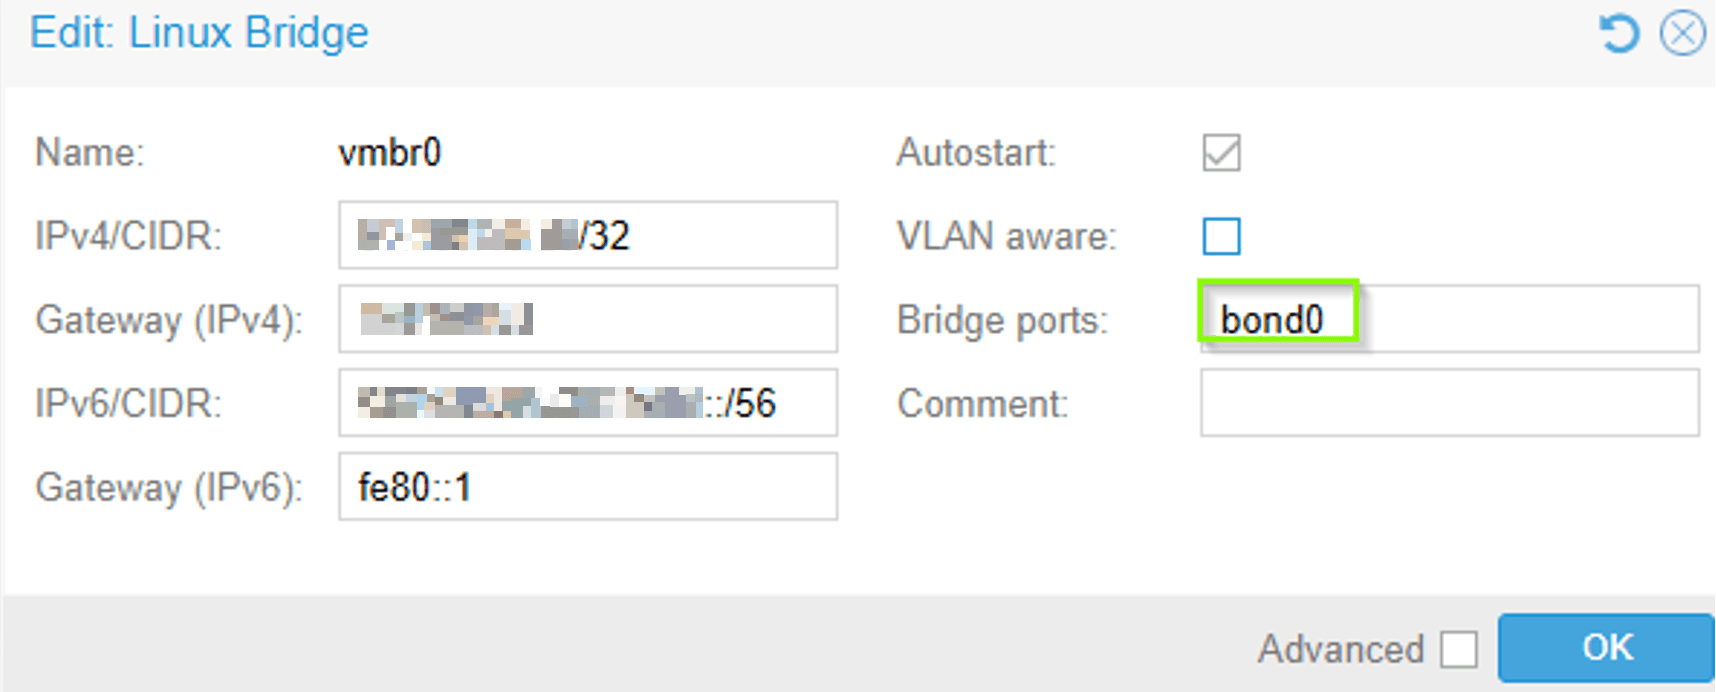
Then, edit the Linux Bond to add the external interfaces.
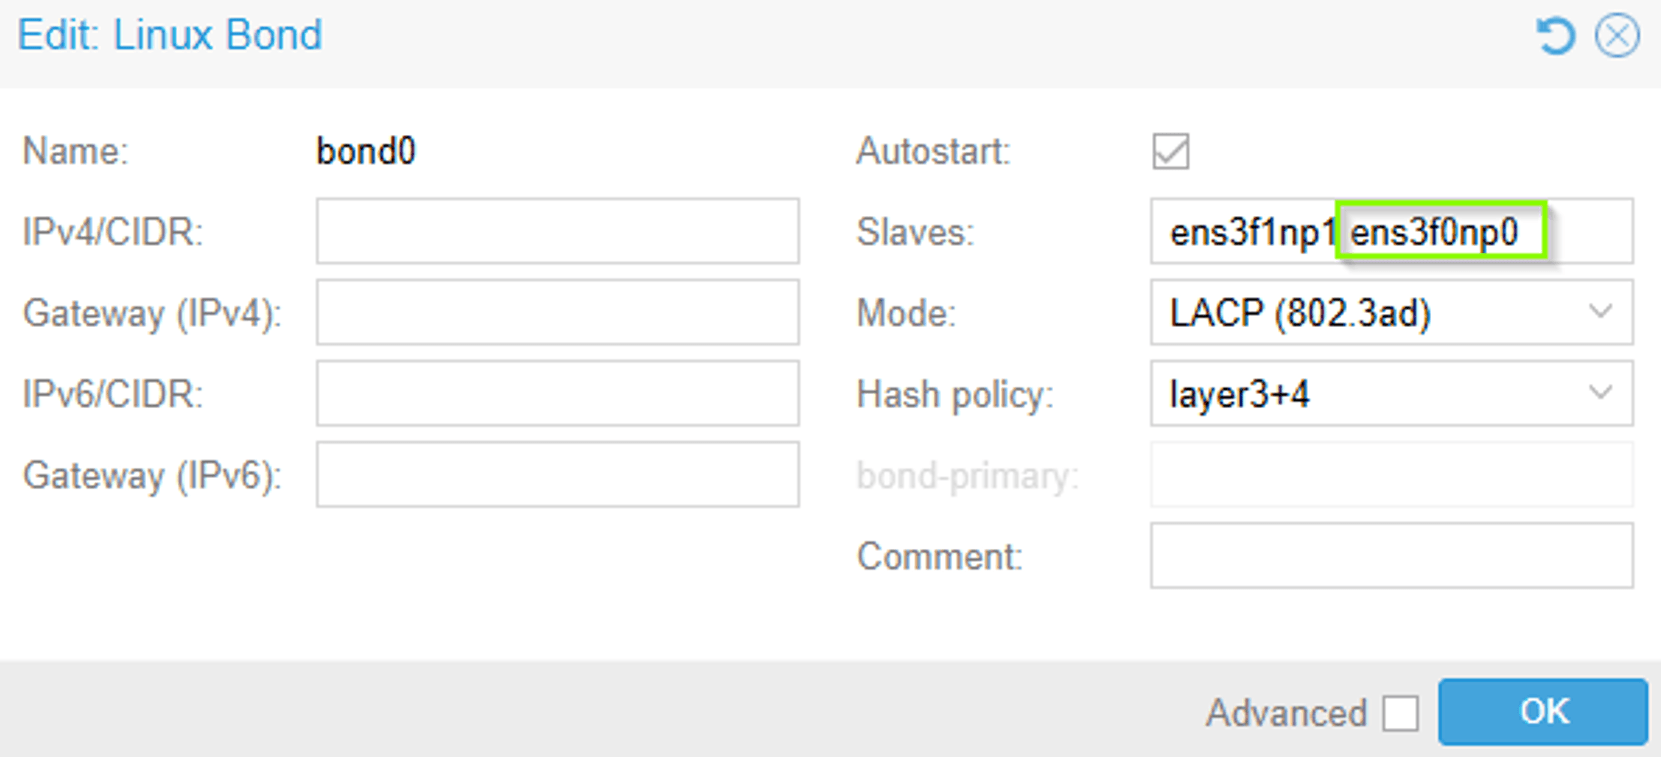
The same steps are used to associate a bond with internal interfaces.
Finally, apply this new configuration.
- Once the bond(s) and bridge(s) are created, click
Apply Configurationin the top right corner. This saves the changes and mimics the effect of restarting the network with thesystemctl restart networkingcommand on the OS side. - Proxmox may prompt you to reboot or confirm the changes; follow the prompt carefully to avoid disconnecting.
Step 3: Testing and validation
From now on, your virtual machines should be able to access the Internet from the additional IPs. They should also be reachable directly from the Internet using their additional IPs.
To check your public IP, from the VM:
You need to restart the VM's network services for the configuration to take effect.
Go further
Browse all the Dedicated Servers guides.
Browse the rest of the OVHcloud US documentation for guides on our other products and services.
Learn more about Dedicated Servers on the OVHcloud US website.