
Getting started with OVHcloud Key Management Service (KMS)
Learn the steps you need to take to set up your first Key Management Service (KMS) and to create a key and access certificate.
Requirements
Instructions
Ordering your KMS
Each KMS is associated with a region, so the keys stored there are guaranteed to stay there. You can order multiple Key Management Services in different regions or the same region.
Since the billing for a KMS is based on the number of keys stored on it, ordering a KMS does not generate billing until keys are created.
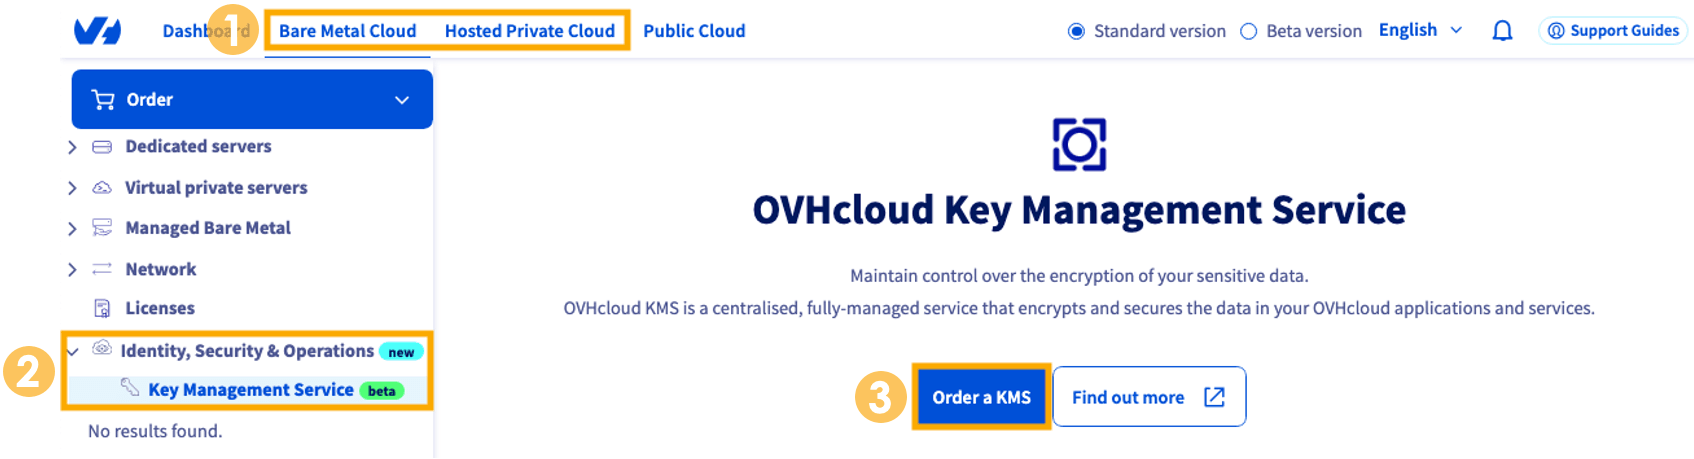
You can order a KMS from the OVHcloud Control Panel by going to one of the following menus:
- In the top navigation bar, choose either
Bare Metal CloudorHosted Private Cloud. - In the left-hand menu, select
Identity, Security & Operations, and thenKey Management Service. - Click
Order.
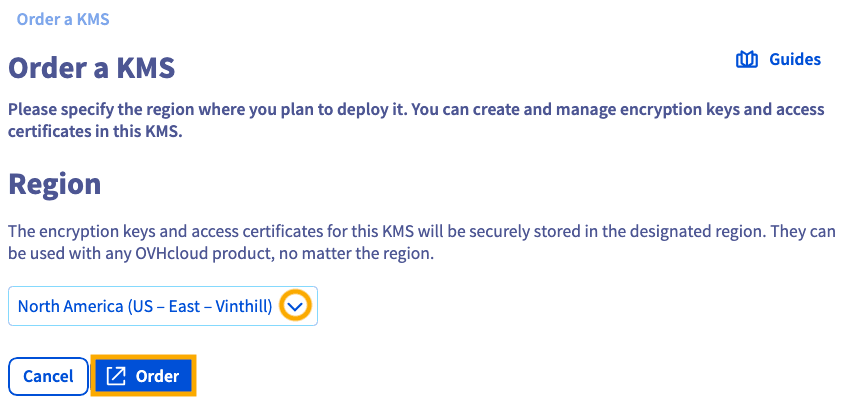
Choose a region for your KMS.
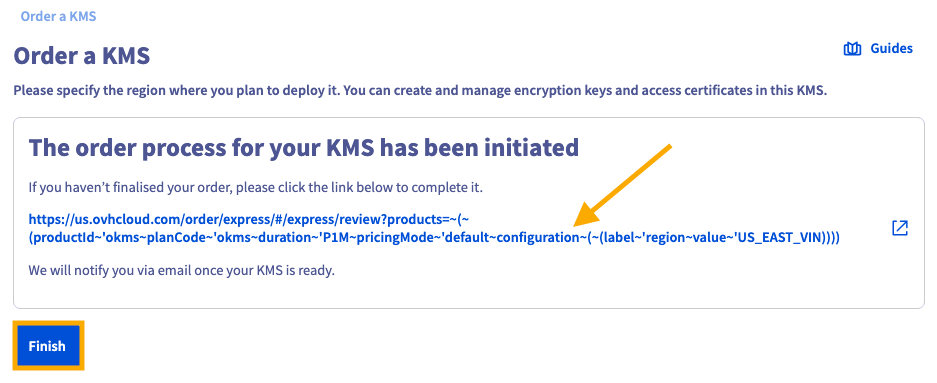
You can then finalize the order in another tab. If it has not opened automatically, the URL is displayed:
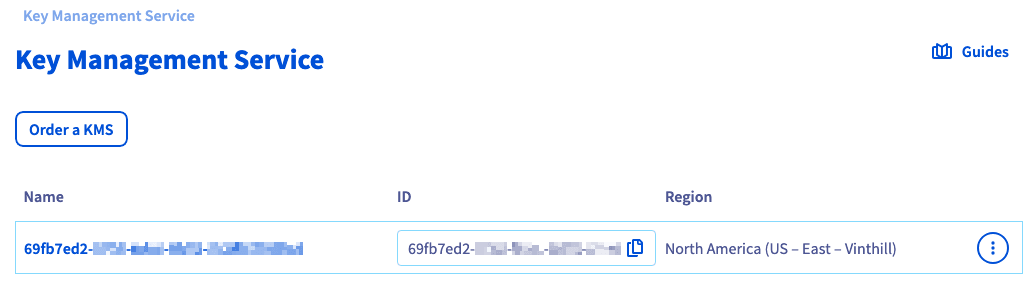
After a few seconds, the KMS will be available in your OVHcloud Control Panel.
NOTE: The more options ... button to the right of your service is where you can cancel that service.
Creating an encryption key
Click each tab across the top to view all content.
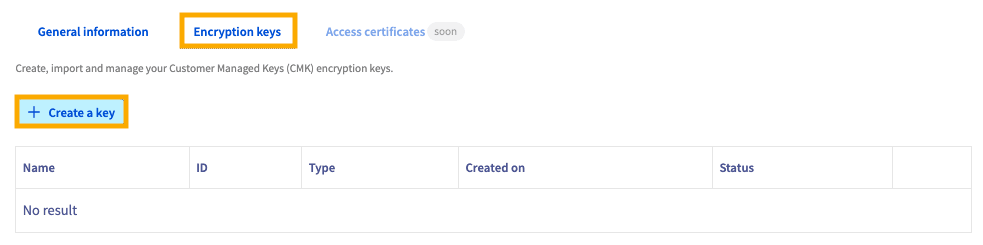
You can create an encryption key from the OVHcloud Control Panel by selecting the KMS service you just created, choosing the Encryption keys tab, and clicking the + Create a key button.
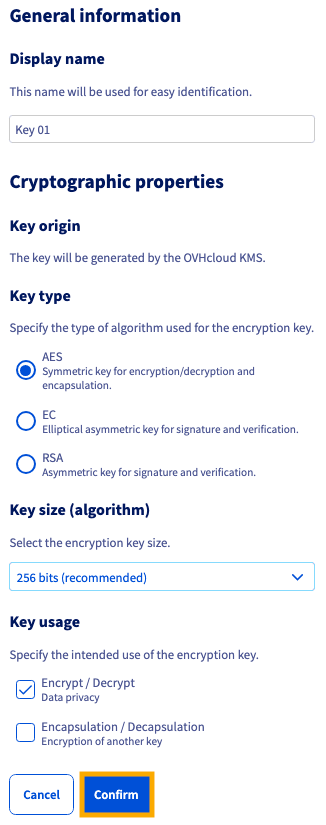
A form allows you to configure the key and select its type, size, and usage. Click Confirm when you have made your selections.
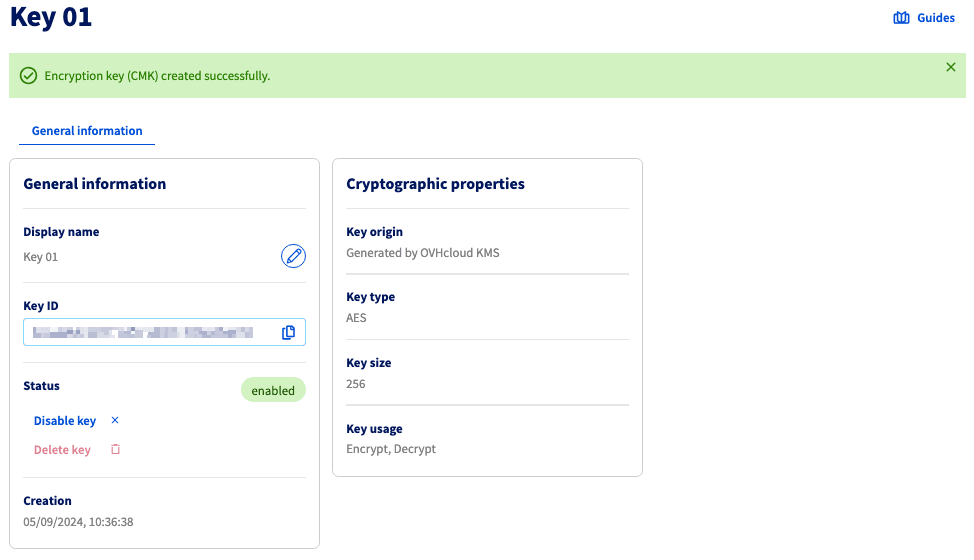
Once the key is created, click on it to access its details. The dashboard displays the cryptographic properties of the key and the actions for renaming, disabling, or deleting it.
To reduce the risk of unwanted deletion, it is required to disable the key before deleting it.
NOTE: A deleted key is not recoverable and results in the loss of any data encrypted with it. Deletions should be performed with great caution.
Creating an access certificate
To communicate with your KMS, you will need to create an access certificate. This will be used for any interaction with the KMS, either to create encryption keys or to carry out operations with them.
The necessary steps to create an access certificate are available in our Manage your OKMS access certificate guide.
Use the OVHcloud KMS
Once your OVHcloud KMS is set up, there are two different ways to use it:
- Using the Rest API, if you want to manually use the API to encrypt or sign your data.
- Using the KMIP protocol, if you want to connect any KMIP compatible product with your OVHcloud KMS.
Go further
Browse all the Key Management Service (KMS) guides.
Browse the rest of the OVHcloud US documentation for guides on our other products and services.
Learn more about Key Management Service on the OVHcloud US website.