
Data - Compliance between AI Tools and S3™ * compatible Object Storage
Learn how to use S3™*-compatible buckets with OVHcloud AI Solutions via the OVHcloud Control Panel and ovhai CLI.
This will help you to manage your data when working with AI Notebooks, AI Training, and AI Deploy.
Topics
- Create an S3™ compatible Object Storage bucket
- Edit your S3™ compatible user roles
- Retrieve user credentials
- Set up proper access permissions
- Add a datastore via the
ovhaiCLI - Create new buckets linked to this datastore using CLI (Optional)
- Upload files to your bucket
- Use S3™ compatible buckets with AI Solutions
Requirements
- Access to the OVHcloud Control Panel
- A Public Cloud project
- A user account created in your Public Cloud project, with the AI and Object Storage roles assigned (for more information about users and roles, see this guide)
- The
ovhaiCLI installed (see our how to install ovhai CLI guide)
Instructions
Create an S3™-compatible bucket
You can create your first S3™-compatible Object Storage bucket in the OVHcloud Control Panel by navigating to the Object Storage section via the Public Cloud menu.
On the next screen, you can see all the buckets you have already created on your Public Cloud project. You can create a new bucket by clicking the + Create an object container button, just above the bucket list.
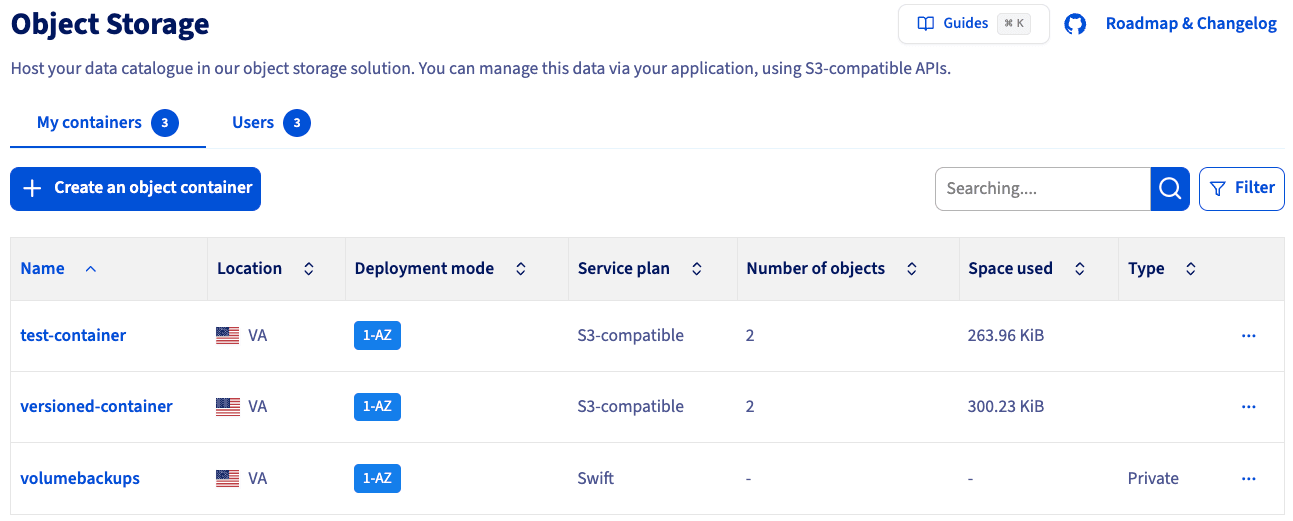
If you haven't created a bucket yet, the interface will be slightly different, prompting you to + Create an object container.
Once you have clicked this button, you will be asked to specify the type of bucket you want to create. In this guide, we will choose the S3™-compatible API:
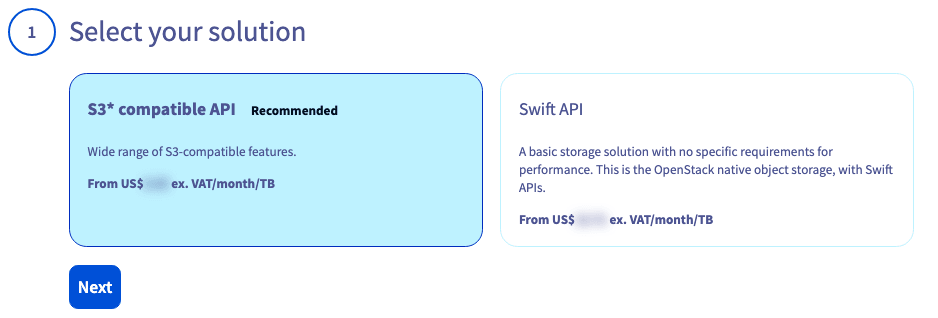
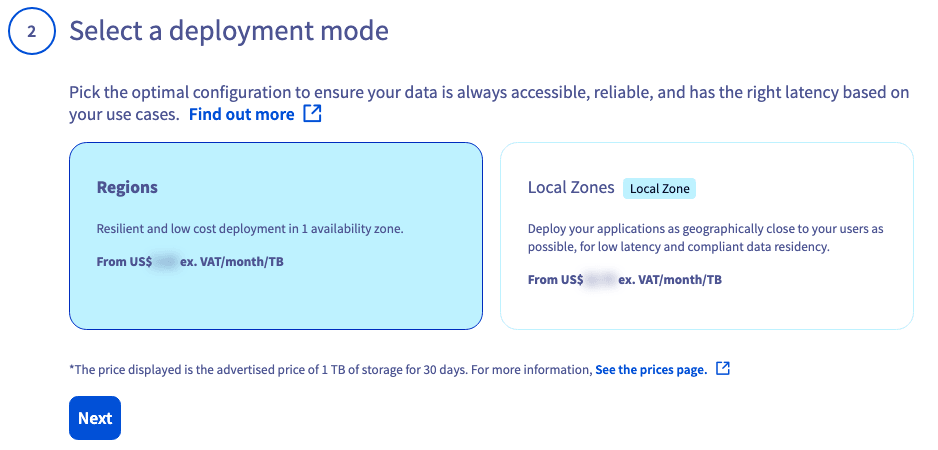
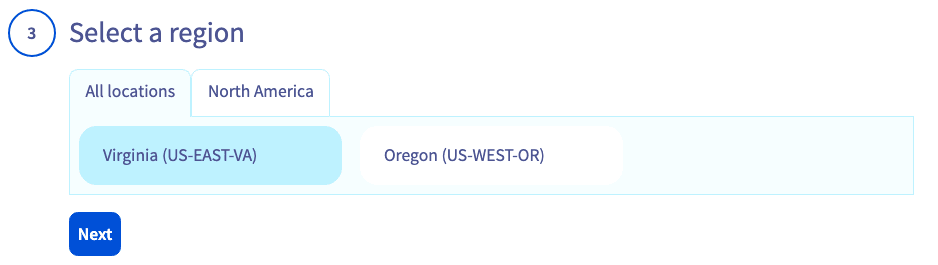
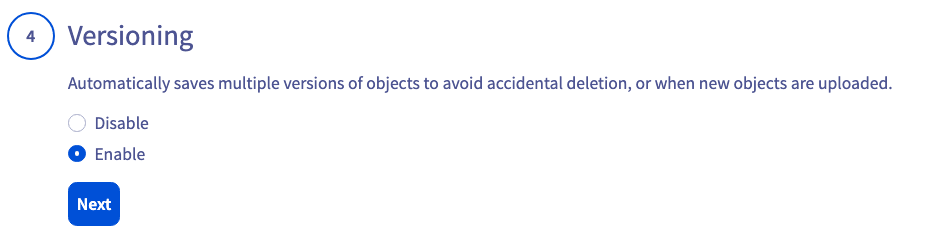
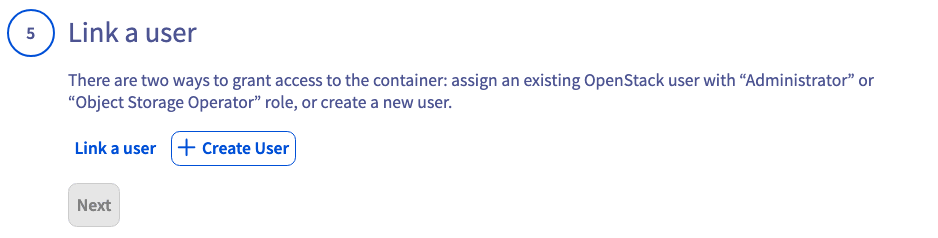
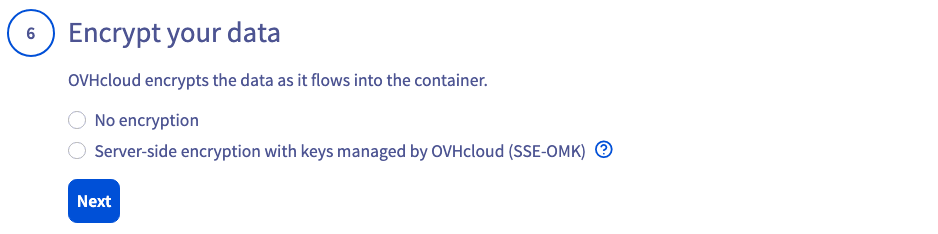
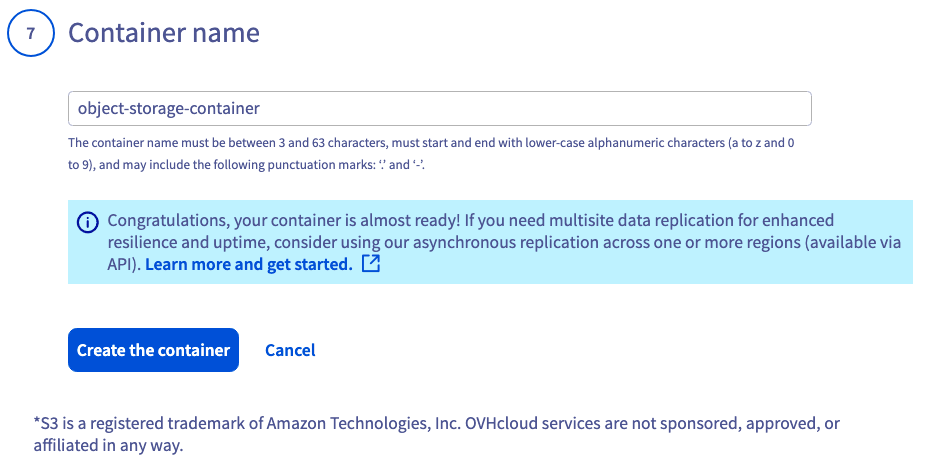
You should then find it in the list of your existing Object Storage buckets.
By clicking on its name and then the Create tab, you can see the objects it contains (empty for now), as well as information such as its endpoint and location (region), which we will use later:
Edit your S3™-compatible user roles
Once your S3™-compatible bucket has been created, you need to check that the associated user has the necessary rights to interact with your data and the OVHcloud AI Solutions (AI Notebooks, Training, and Deploy).
For Local Zone deployment, you did not need to associate a user with your bucket. However, it is important to check that you also have at least one user with the necessary rights.
To do that, navigate to the Users & Roles area in the Project Management section of the OVHcloud Control Panel.
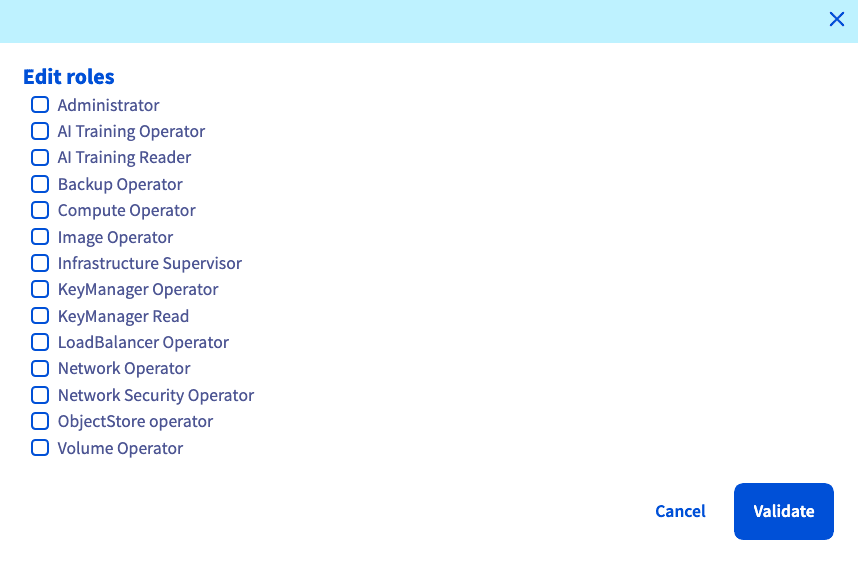
Whether you have created a new user or use an existing one, check that this user has at least the following rights: AI Training Operator and ObjectStore Operator, as shown below:
For more information about editing user rights, you can check the dedicated documentation.
Retrieve user credentials
Before continuing, you need to ensure that you have the following information so that you can authenticate via the CLI and use your bucket:
- Username
- Password
- S3™-compatible access key
- S3™-compatible secret key
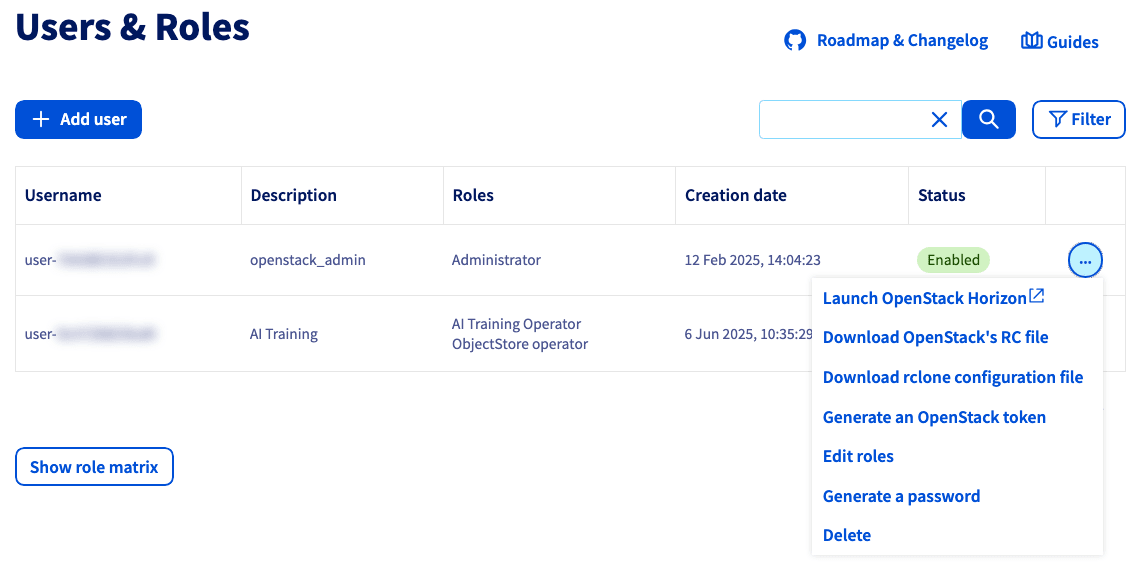
As we saw in the previous step, all your Public Cloud project users are displayed in the Users & Roles menu in the Project Management section. You will find there your existing usernames. The username we are interested in is the one to which you gave permissions in the previous step.
If you have lost the password associated with this username, you can regenerate it by clicking the more options ... button, and then on Generate a password, which will revoke the old one.
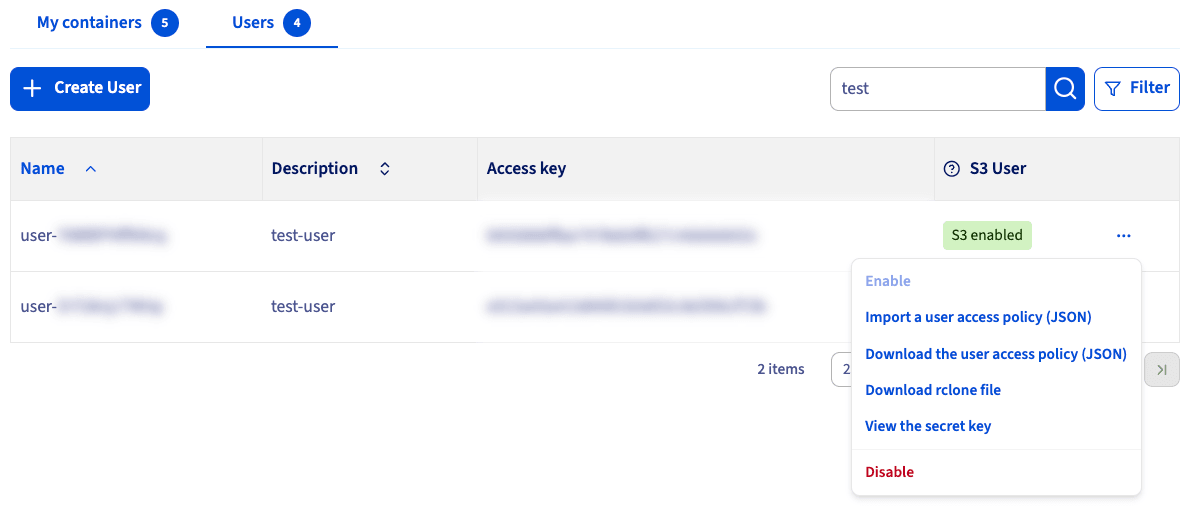
Then, you need to retrieve the access key and secret key associated to this user. To do that, return to the Object Storage section. Click on the Object Storage Users tab. Here you will find the Access key for each of your existing users. You can also view the secret key by clicking the more options ... button, then on View the secret key.
Set up proper access permissions
It is also important to ensure that this user has the appropriate permissions to access all the files in the bucket. Otherwise, you may encounter permission issues during the AI Solution deployment process.
To grant access to your bucket for your user, click the more options ... button located next to your bucket name. Then, click the Add a user to a container option and select the same user you used during bucket creation.
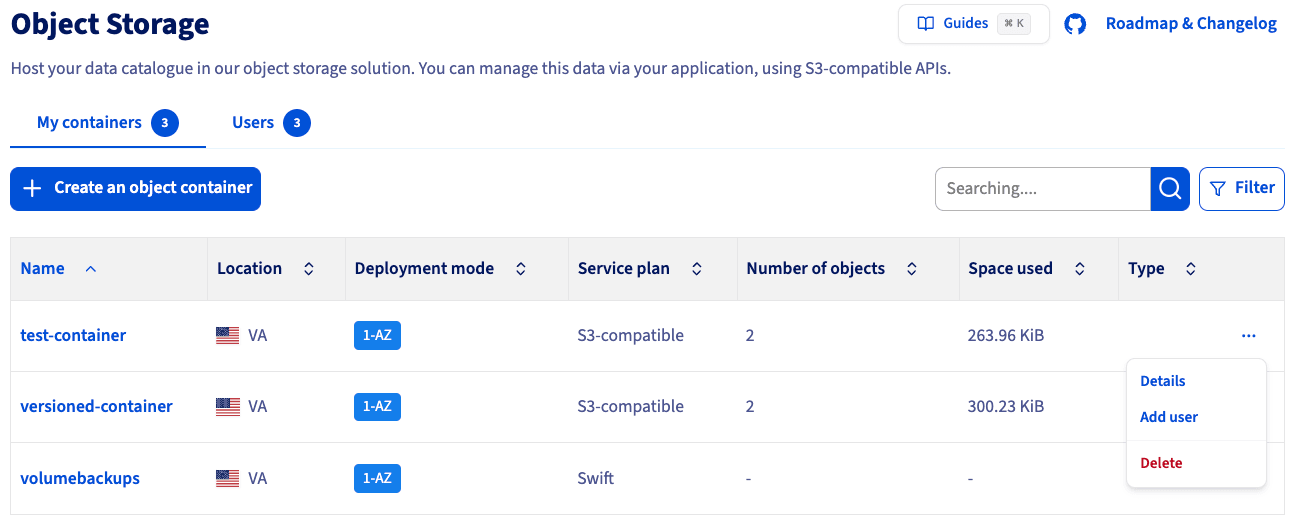
By following these steps, you can grant the necessary permissions to your user, ensuring a smooth deployment process for your notebook, job, or app.
Add a datastore via the ovhai CLI
Now that your bucket has been created, and the associated user has the necessary permissions, you can move on to the ovhai CLI. If you have not installed it yet, please refer to the ovhai CLI installation guide.
The first step is to authenticate with the user that you have granted access to your bucket. To do this, use the following command:
We recommend that you choose the Terminal authentication mode, and enter your username and associated password to log in.
If you encounter an authentication error, please recheck this step and make sure you have the AI right.
Once authenticated, you can list your existing datastores with the following command:
You should obtain the following result:
Here you can see that there are no S3™-compatible data stores in the list yet. That is why you will add your own, to then access the buckets of a given region, and for a specific access key and secret key combination!
To add this datastore, you will use the ovhai datastore add s3 command pattern. You can use the --help flag to know more about adding S3™-compatible datastores:
This will give us the different arguments to fill in:
Here is the command pattern to add an OVHcloud S3™-compatible datastore:
You will need to replace: - <alias> by the name you want to give for your datastore - <endpoint_url> by the Endpoint value you have retrieved at the end of bucket creation step. This endpoint should start with: https://s3.... - <region> by the region where you have created your bucket. This region is indicated as the Location of your bucket, on the last screenshot of the bucket creation step. Make sure you use lowercase letters. - <my-access-key> by the access key of the associated user - my-secret-key by the secret key of the associated user
This endpoint also allows you to choose between Standard and High Performance storage classes. The storage class you select will determine the storage class used during file upload to the bucket when using the ovhai CLI. If you plan to upload files using the Control Panel (UI), you will have the option to choose between Standard and High Performance storage. However, when using the CLI, the default endpoint will use Standard storage. If you require High Performance storage, please ensure that the endpoint ends with .perf.cloud.ovh.us.
For more information on storage classes, please consult this documentation.
Here is an example to add a datastore named ai-training that will handle Region buckets created in Vint Hill (us-east-va) region (since they share the same endpoint_url):
You can now check the datastore list:
You should see your new datastore in the list:
Now that you have a datastore dedicated to the specified region, you can list the buckets associated to this region and access and secret keys combination by running the following command (replace by your datastore name, s3-ai-training in previous example):
You can see that the bucket s3-ai-training you created using the Control Panel (UI) has been retrieved.
Create new buckets linked to this datastore using CLI (Optional)
This step is optional and for information only.
Now that your datastore is configured, you can simply create new buckets for the region and user associated with your datastore using the following command, rather than using the OVHcloud Control Panel (UI):
Keep in mind that the bucket name must be between 3 and 63 characters, can consist only of lowercase letters, numbers, dots (.), and hyphens (-), and must start and end with lowercase alphanumeric characters (a to z and 0 to 9).
Then you can check that your S3™-compatible bucket has been created correctly, and linked to your datastore (replace by your datastore name, 1azgra in previous example):
You should see your bucket in the list:
Upload files to your bucket
Before connecting your bucket to the AI solutions, you are going to upload a few objects to it (images, codes, models, etc.) so that you can then retrieve these files from the AI Solutions. You can do this using the Control Panel (UI) or the ovhai CLI:
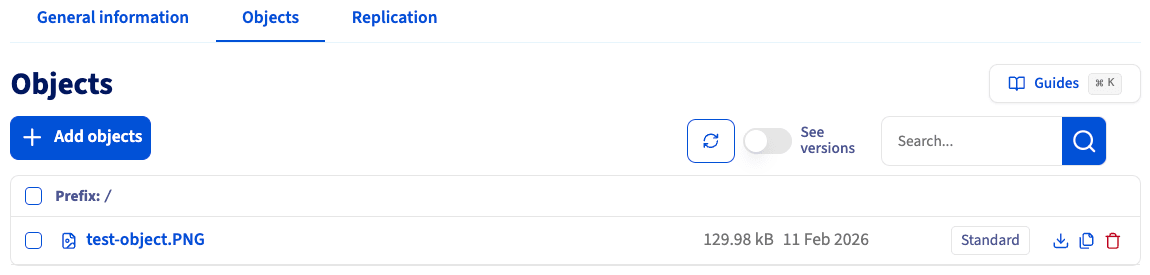
Go to the Object Storage section (in the Storage category) and click on your bucket name. Then, click the My Items tab and the + Add objects button:
Select the files you want to upload to your bucket. If needed, you can prefix their names. Then, choose between Standard or High performance storage (find more information about storage classes here). Once you have made your selection, confirm by clicking on Import.
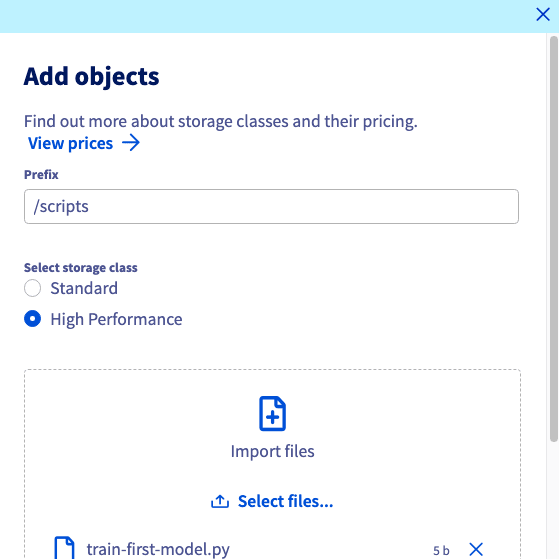
In this example, the python file train-first-model.py is added and prefixed by /scripts, resulting in the file path /scripts/train-first-model.py.
Once the upload is completed, you should see uploaded files in the object list.
Using S3™-compatible buckets with AI Tools
Now that your S3™-compatible bucket has been created and populated with some objects, you can mount it on any OVHcloud AI Solution to access your data.
Please note that for the moment this S3™-compatible feature can be used through ovhai CLI only. It will soon be available from the OVHcloud Control Panel.
To launch an AI notebook with an S3™-compatible bucket mounted as remote data, you can use the following command pattern:
Just make sure to replace the framework and editor by those of your choice. Also, specify the right <bucket-name> and <datastore-alias, and designate the destination where you want the bucket data to be stored (<mount_path>) and its access permission (rw for read & write, or ro for read only).
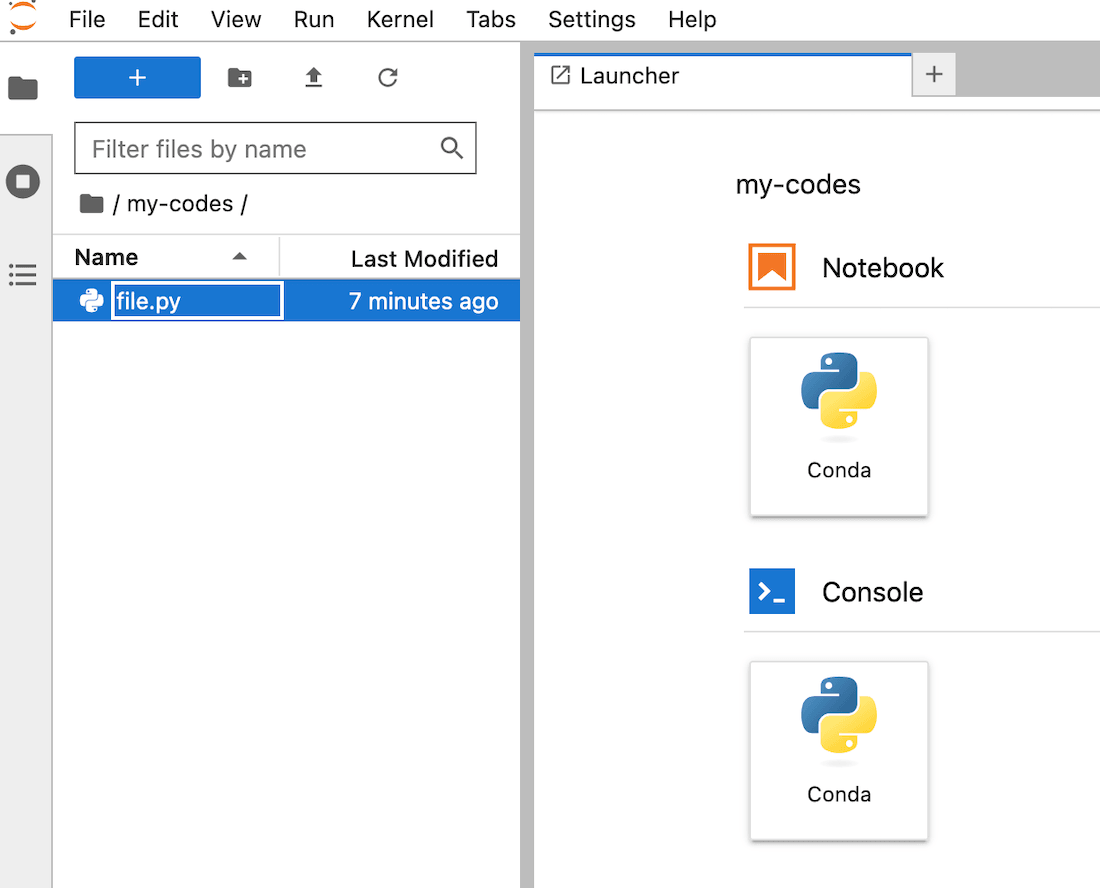
For example, to launch a basic Jupyter notebook on 2 CPUs, with a Conda pre-packaged environment, and the bucket ai-training-container from the s3-ai-training datastore mounted as remote data on /workspace/my-codes with read and write (RW) permissions, use the following command:
This command will create an AI notebook with the specified framework and editor, and will mount the specified bucket at the specified destination with the specified permissions. After logging in to your notebook interface (using the same credentials you have used to ovhai login), you should see the uploaded file in your notebook's workspace:
For more information on the capabilities of the ovhai notebook run command, you can run the following command:
You can also consult the dedicated CLI - Launch an AI notebook documentation to know more about the possible options, frameworks, and editors available.
Go further
Browse all the AI & Machine Learning guides.
Browse the rest of the OVHcloud US documentation for guides on our other products and services.
Learn more about AI & Machine Learning on the OVHcloud US website.
If you need training or technical assistance to implement our solutions, contact your sales representative or click on this link to get a quote and ask our Professional Services experts for a custom analysis of your project.
*S3 is a trademark filed by Amazon Technologies, Inc. OVHcloud's service is not sponsored by, endorsed by, or otherwise affiliated with Amazon Technologies, Inc.