
How to activate and use rescue mode
Learn how to reboot and use a server in rescue mode.
Rescue mode is a tool provided by OVHcloud that allows you to boot into a temporary operating system to diagnose and resolve issues on your server.
Usual tasks the rescue mode is appropriate for include:
- Resetting your user password
- Diagnosing network problems
- Repairing a broken operating system
- Fixing a software firewall misconfiguration
- Testing disk performance
- Testing CPU and RAM
Requirements
- A dedicated server in your OVHcloud account
- Access to the OVHcloud Control Panel
Topics
- Activating rescue mode
- Accessing your server in rescue mode via SSH
- Mounting partitions to access your files
- Link Aggregation configuration in rescue mode
- Exiting rescue mode
- How to add a default authentication key for rescue mode
- Legacy Windows rescue system (WinPE rescue mode)
- How to test Additional IP and vRack functionality in rescue mode
Instructions
To use rescue mode, you must edit the server's Netboot setting. Then the server has to be restarted.
Activating rescue mode
Log in to your OVHcloud Control Panel, open the Bare Metal Cloud section, then Dedicated servers, and select your server from the list.
In the General information box, click the more options ... button next Boot and select Edit.
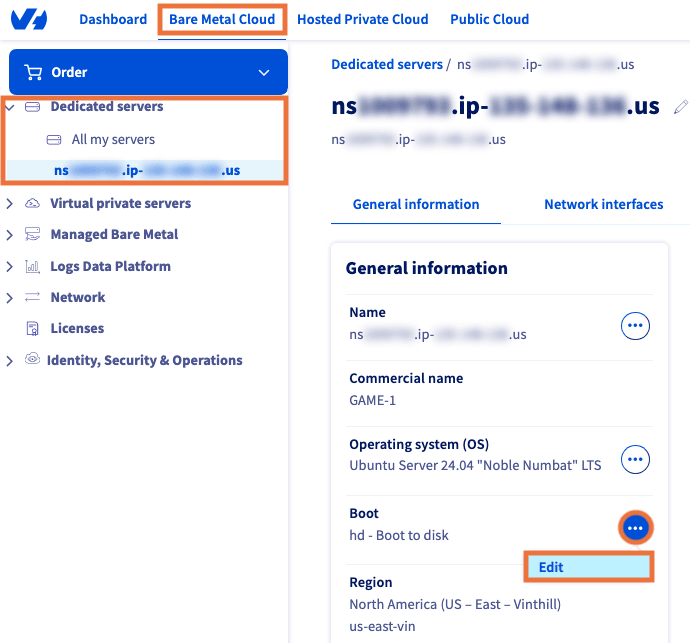
1: Rescue mode options
On the page Change the netboot, select Boot in rescue mode.
The available options for rescue mode depend on the server type and the operating system installed.
- Customer rescue system (always available)
- Rescue system for Windows (available for Windows servers)
- iPXE / ipxe-shell (external open-source tool, always available)
- Legacy Windows rescue system (deprecated WinPE system, only relevant if your server does not meet the requirements for the current rescue system for Windows)
The instructions below will only cover the customer rescue system, the most commonly used option.
Please refer to our dedicated guide for a detailed explanation on using the rescue system for Windows.
Select Customer rescue system in the drop-down menu.
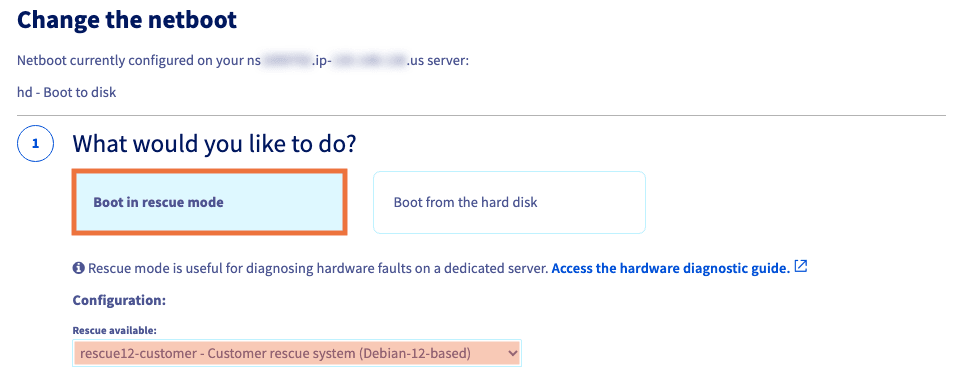
2: Authentication options
The next choice determines the method of authentication for the SSH connection to the rescue mode system. This is mainly a matter of convenience since each rescue mode session is meant to be transitory and will be discarded once you reboot the server from its disk.
- Password authentication: You will be sent login credentials via email.
- Key authentication: You can use a public authentication key of your choice (compatible formats:
RSA,ECDSA,ED25519).
Click on the relevant tab for your connection method:
Click Password authentication.
The rescue mode notification email including its login details will be sent to the contact email address of your OVHcloud account. To use a different email address, enter it in the field Send new login details to the following email address.
Click Next.
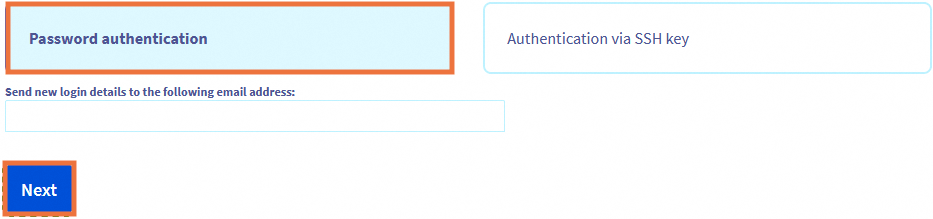
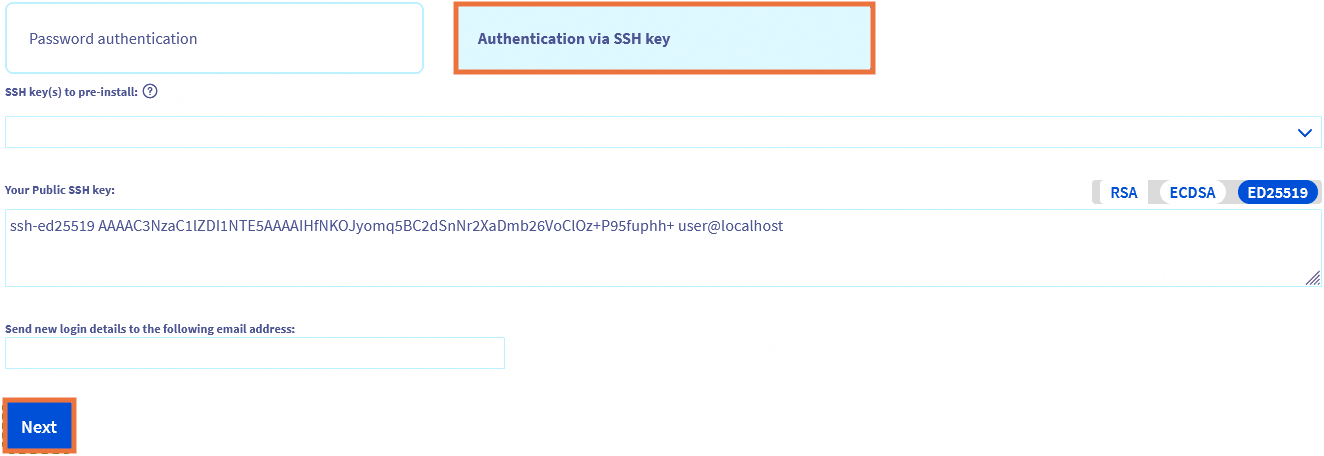
3: Final steps to activate rescue mode
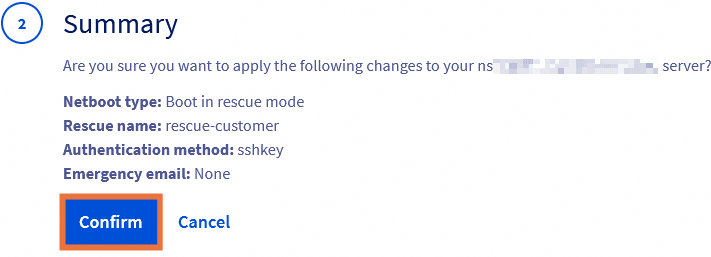
In the Summary step, click Confirm.
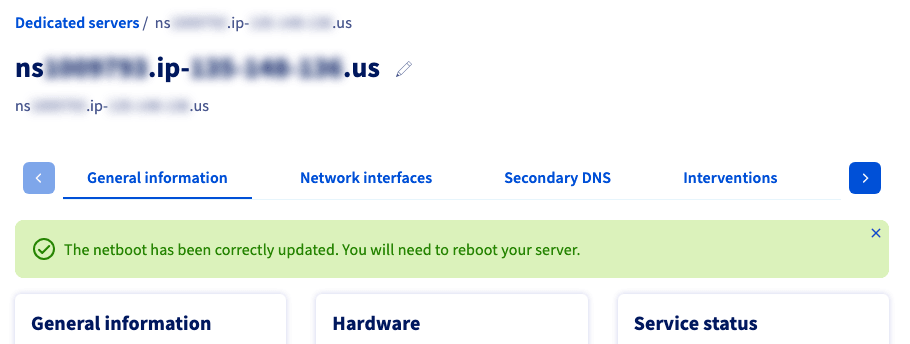
You should now have a notification regarding the Netboot setting in the General information tab.
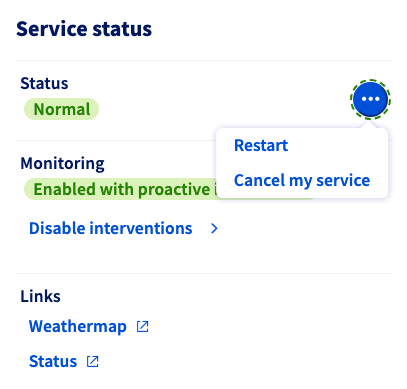
The final step is to restart the server. Click the more options ... button next to "Status" in the Service status box, then select Restart. Click Confirm in the pop-up window.
This "hard reboot" will take a few minutes to complete. You can check the current status in the tab named Tasks.
After you have finished your actions in rescue mode, remember to change the Netboot setting back to Boot from the hard disk before restarting the server.
Accessing your server in rescue mode via SSH
Once you have received the email informing you that rescue mode is enabled, you can log on to the rescue mode system and access your server.
Your SSH client will normally block the connection at first due to a mismatch of the ECDSA fingerprint. This is normal because the rescue mode uses its own temporary SSH server. To resolve this, you need to edit the file known_hosts of your local .ssh folder.
You have two options:
- Delete the fingerprint from the file. Your SSH client will then add a new fingerprint entry for the server when you are no longer using rescue mode. For a detailed explanation, refer to our SSH introduction guide.
- Temporarily disable the fingerprint. Open the file
known_hostswith a text editor and identify the fingerprint string of your server by its IP address. Add the character#at the start of the line. As a result, this line is now a "comment" and will be ignored by applications reading the file. Remember to revert this change before switching theNetbootback to the "normal" mode.
Click on the relevant tab for your selected connection method:
Open the command line application on your local device and enter the following command:
Example:
Enter the temporary rescue mode password when prompted.
Find more information about SSH connections in our SSH introduction guide.
Mounting partitions to access your files
Unless you intend to configure the server's disks in a way that requires them to be detached (unmounted), you need to first mount the system partition in order to access your data from rescue mode.
Firstly, list all partitions to retrieve the name of the partition you need to mount:
Output examples:
Then mount the pertinent partition accordingly:
The partition to mount should be easily identifiable by the SIZE indicated in the table (sda2 in the first example, nvme1n1p3 in the second). Using the folder name mnt as mount point, for the first example the mount command would therefore be as follows:
Command to enter for the second example:
NOTE: The examples above illustrate the necessary steps based on a typical server configuration. The information in the output table depends on your server's hardware and its partition scheme. When in doubt, consult the documentation of your operating system.
If you require professional assistance with server administration, consider the details in the Go further section of this guide.
To see more technical information about the server's disks and partitions, enter:
Some tasks may require that disks or partitions be detached. To do this, use the unmount command:
NOTE: For password reset instructions, see the guides below:
VMware - Mounting a datastore
You can mount a VMware datastore in a similar way as described in the previous segment.
Click here for the full instructions.
List your partitions in order to retrieve the name of the datastore partition:
Mount the partition with the following command, replacing sdbX with the value identified in the previous step:
If you have VMFS 6 datastores, access the sbin folder and create the mount folder:
List your partitions to retrieve the name of the datastore partition:
Mount the partition with the following command, replacing sdbX with the value identified in the previous step:
Once the mounting operation is done, you can access your files and carry out troubleshooting tasks inside the folder you have defined as mount point. Example:
Certain operations on the file system (such as configuring user accounts) will require an additional step. Create a temporary chroot environment at the mount point with this command:
You should now be able now apply all necessary changes to your system.
Link Aggregation configuration in rescue mode
Link Aggregation (LACP) is highly beneficial, as it increases your server's total bandwidth while providing network redundancy in case a network interface fails.
Although rescue mode is based on the Debian 12 operating system, its network configuration relies on the ifupdown utility, instead of Netplan.
If you have a server that supports link aggregation and you wish to configure it in rescue mode, please refer to this guide.
Exiting rescue mode
If relevant, return to the rescue mode login shell by entering:
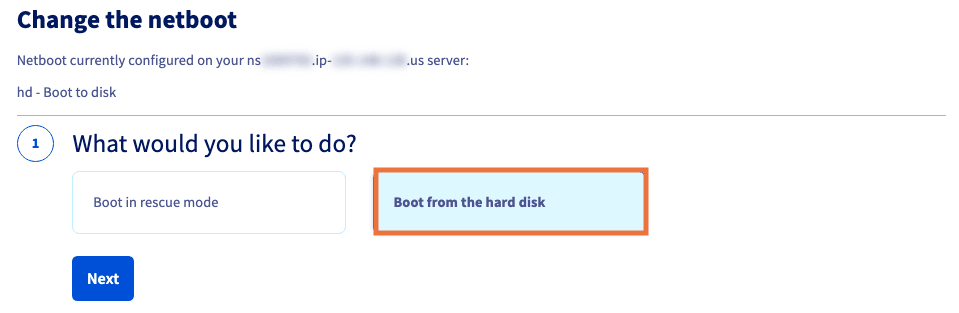
In your OVHcloud Control Panel, change the boot mode back to Boot from the hard disk and confirm.
You can now restart the server from the rescue mode shell:
Alternatively, use the Restart function in the OVHcloud Control Panel.
How to add a default authentication key for rescue mode
To speed up the process, you can add a public key as default for rescue mode SSH access to your server. This is only possible via the OVHcloud API.
Click here for the full instructions.
To do this in the API web console, open the following API endpoint:
Enter the internal name of your server (ns1111111.ip-203-0-113.us) in the appropriate field.
Then edit the text field below as follows:
Replace string with your full public key string.
The result should look as shown in the following example:
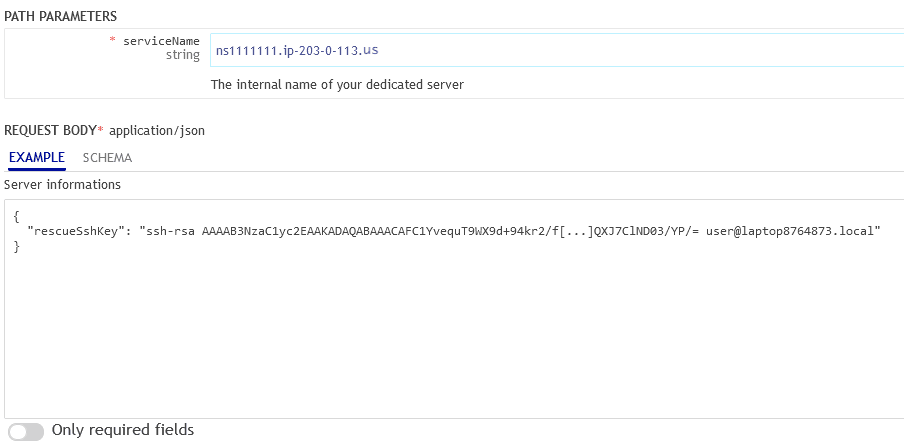
When you have entered your values correctly, click the button EXECUTE.
The field Your Public SSH key: will now be filled automatically with this key string when changing the Netboot mode.
Legacy Windows rescue system (WinPE rescue mode)
Once you have received the email informing you that rescue mode is enabled, you can log on to the rescue mode system and access your server.
Click here for the full instructions.
To use the Windows PE rescue mode GUI, you will need to download and install a VNC console or use the IPMI module (not available on all server models).
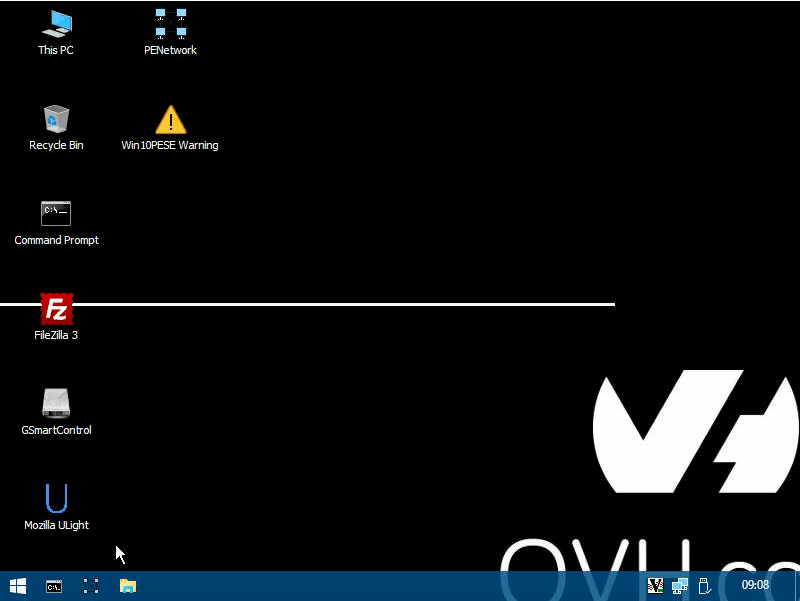
The following tools are already installed in this mode:
How to test Additional IP and vRack functionality in rescue mode
Testing Additional IPs
Configured as an alias (without vMAC)
To begin, put your server into rescue mode as described above. Once you are in rescue mode, use the following command to identify your NIC.
To find the correct NIC in your output, find the NIC that has your server's public IP address attached. In this article, we use the example interface eth0. We will add our additional IP to the interface using the following command. Be sure to replace our example values with yours.
To test that your additional IP is functioning properly, ping it from a separate machine. If you are concerned that you are having routing issues, you can perform an mtr (My traceroute) test. In our example, we use an OpenDNS server. Be sure to replace our example values with yours.
If you determine that you have routing issues, send the outputs of the following tests to OVHcloud US Support.
Bridge configuration (with vMAC)
For a bridge configuration, the above steps will work with one modification. To add our additional IP to the interface, we will use the following four commands instead of the ip addr add command used above.
In our example, we name our test link "testrescue." Be sure to replace our example values with yours. If you need help finding your Virtual MAC, check out the following article: How to Assign a Virtual MAC to an Additional IP
Testing vRack
NOTE: Before testing your vRack connection, make sure both of the servers you use are on the same vRack.
To begin testing that your vRack connection works, put two servers into rescue mode.
Once you have gained access to rescue mode, we will configure both servers. We will use the same configuration on both servers, but with different private IP addresses. First, find your private interface using the following command:
Next, we will set our network configuration. To do so, open the interface file using the following command.
Below is a sample configuration for this file. Make sure the private IPs you use on both servers are on the same subnet.
Once you have configured both servers, ping one server from the other. If it works, you know you have a working vRack. If it does not, contact OVHcloud US support and send them the configuration files and results of your failed ping test.
Go further
How to activate and use Windows rescue mode
How to recover server access if your user password is lost
How to replace your authentication keys for SSH access if a key is lost
How to diagnose server hardware issues
How to use the IPMI console with a dedicated server
Browse all the Dedicated Servers guides.
Browse the rest of the OVHcloud US documentation for guides on our other products and services.
Learn more about Dedicated Servers on the OVHcloud US website.