
Object Storage - Identity and access management
Requirements
- A Public Cloud project in your OVHcloud account
OVHcloud Control Panel Access
- Direct link: Public Cloud Projects
- Navigation path:
Public Cloud> Select your project
Instructions
Creating a user
Click on Object Storage in the left-hand menu.
Choose the Users tab and click + Create User.
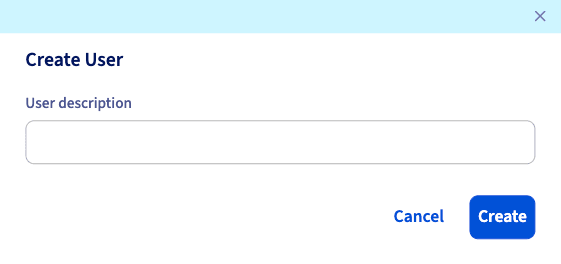
In the pop-up window, enter a description for your user and click Create.
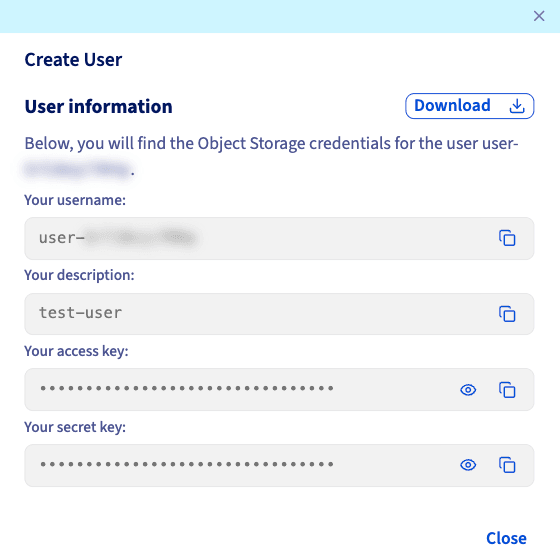
Once your user has been created, you will see the credentials:
By clicking on the more options ... button at the end of a user’s line, you can, among other things, download the Rclone configuration file, see the user’s secret key, and delete the user.
Manage access to a container via a profile
You can define access to your containers via pre-defined profiles.
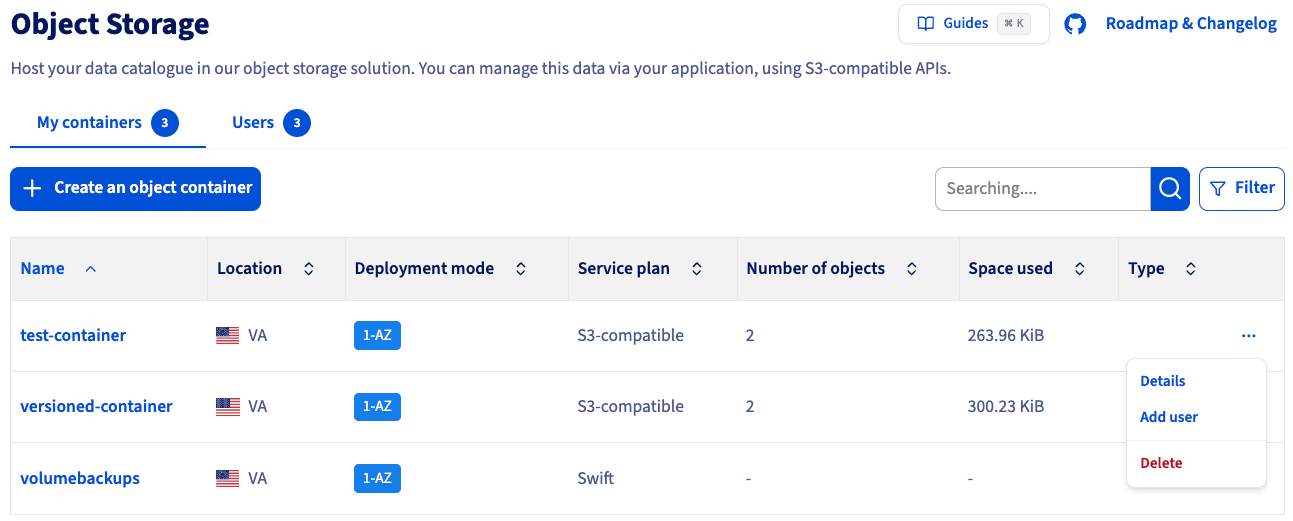
From the My containers tab, click on the more options ... button at the end of your container line, and then select Add user from the drop-down menu.
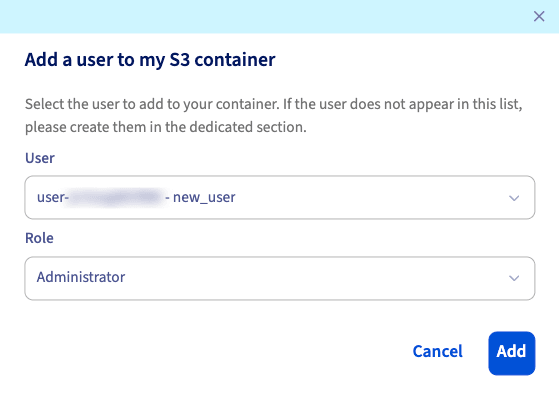
Select the user, choose a role, and click Add.
Advanced resource access management
Overview
By default, all resources (buckets, objects) and sub-resources (lifecycle configuration, website configuration, etc.) are private in Object Storage. Only the resource owner, i.e., the user account that creates it, has full control.
Access to private resources can be granted via access policies. Access policies can be categorized broadly into two types:
- user-based: access policies attached to a specific user are called user policies. A user policy is evaluated using Object Storage IAM permissions and applies only to the specific user it is attached to.
- resource-based: bucket policies and ACLs are policies that are attached directly to specific resources
Bucket policies are a feature that is not yet available for Object Storage. This article is about user policies.
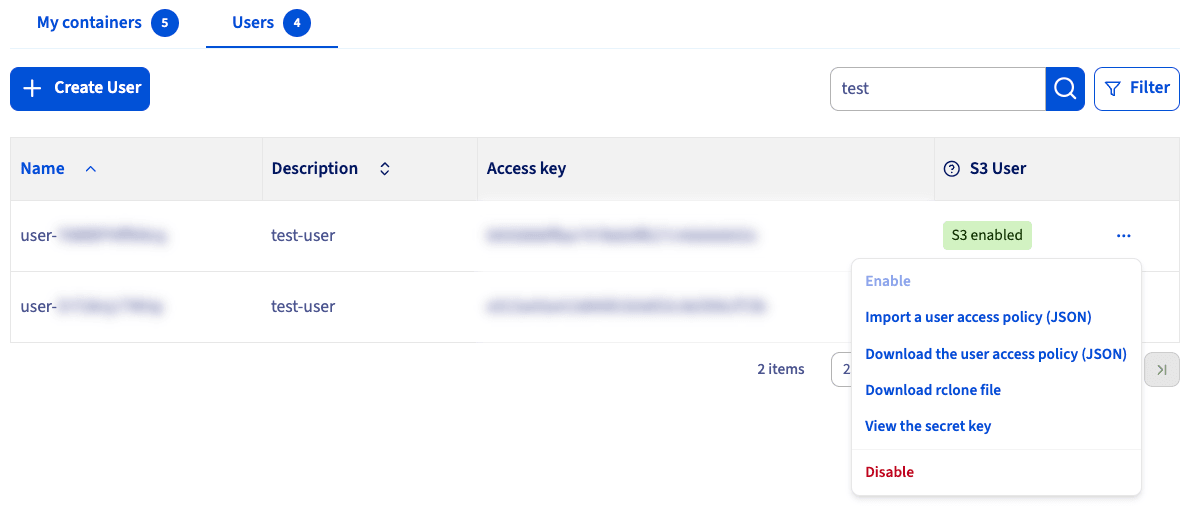
You can refine your permissions by importing a JSON configuration file. To do this, go to the Users tab.
Click on the more options ... at the end of your user’s line, then Import a user access policy (JSON).
If you want to change a user’s rights, you may need to download the JSON configuration file in advance by selecting Download the user access policy (JSON).
Understanding the user policy evaluation process
At the moment, user permissions are evaluated as follows:
-
if exists, evaluate user policy else fallback to ACLs
- check for an explicit deny: if there is an explicit deny, then deny permission, else, check for an explicit allow
- check for an explicit allow: if there is an explicit allow, then allow permission
- if there is no explicit deny nor explicit allow, then fallback to ACLs
-
fallback to ACLs
This evaluation process will be subject to change with the upcoming implementation of bucket policies.
Some examples of JSON configuration files:
Read/write access to a bucket and its objects
Read-only access to a bucket and its objects
Deny listing of all buckets owned by the parent account
The (s3:ListAllMyBuckets) action is allowed by default for a given user. Add the Deny effect if you want to explicitly refuse the use of the ListBuckets API operation.
Allow all operations on all project resources
Read/write access to all objects in a specific folder (/home/user2) in a specific bucket (<bucket_name>)
Allow all operations to specific IPs by whitelisting authorized IPs
As a consequence of the current authorization process, implicit deny is not supported by OVHcloud Object Storage if the user is the bucket owner i.e., since ACLs are evaluated by default and since the bucket owner has FULL_CONTROL ACL, if the user is the bucket owner and even if there is no explicit allow in the policy file, the user will be authorized.
The following policy to attempt to allow read access to objects only to specific IPs will not work under current conditions if attached to the bucket owner i.e., even if the bucket owner makes his requests from IPs that are not in the specified range, the bucket owner will be authorized.
The following policy to attempt to deny read access to objects to specific IPs by blacklisting unauthorized IPs will not work under current conditions if attached to the bucket owner because there is no explicit deny and requests from the specified IPs will not match the allow, therefore, we fall back to the ACLs.
List of supported actions
Go further
Browse all the Object Storage (S3™-compatible) guides.
Browse the rest of the OVHcloud US documentation for guides on our other products and services.
Learn more about Object Storage on the OVHcloud US website.
If you need training or technical assistance to implement our solutions, contact your sales representative or click on this link to get a quote and ask our Professional Services experts for a custom analysis of your project.
*S3 is a trademark filed by Amazon Technologies, Inc. OVHcloud's service is not sponsored by, endorsed by, or otherwise affiliated with Amazon Technologies, Inc.