
Scanning Docker Images for Vulnerabilities with OVHcloud Managed Private Registry (Harbor)
Learn how to activate the vulnerabilities scanner and manually scan an image in an OVHcloud Managed Private Registry service.
OVHcloud Managed Private Registry service is a composite cloud-native registry that supports both container image management and Helm chart management.
Before you begin
This tutorial assumes that you already have a working OVHcloud Managed Private Registry and you have followed the guides on creating a private registry, connecting to the UI, managing users and projects and creating and using private images.
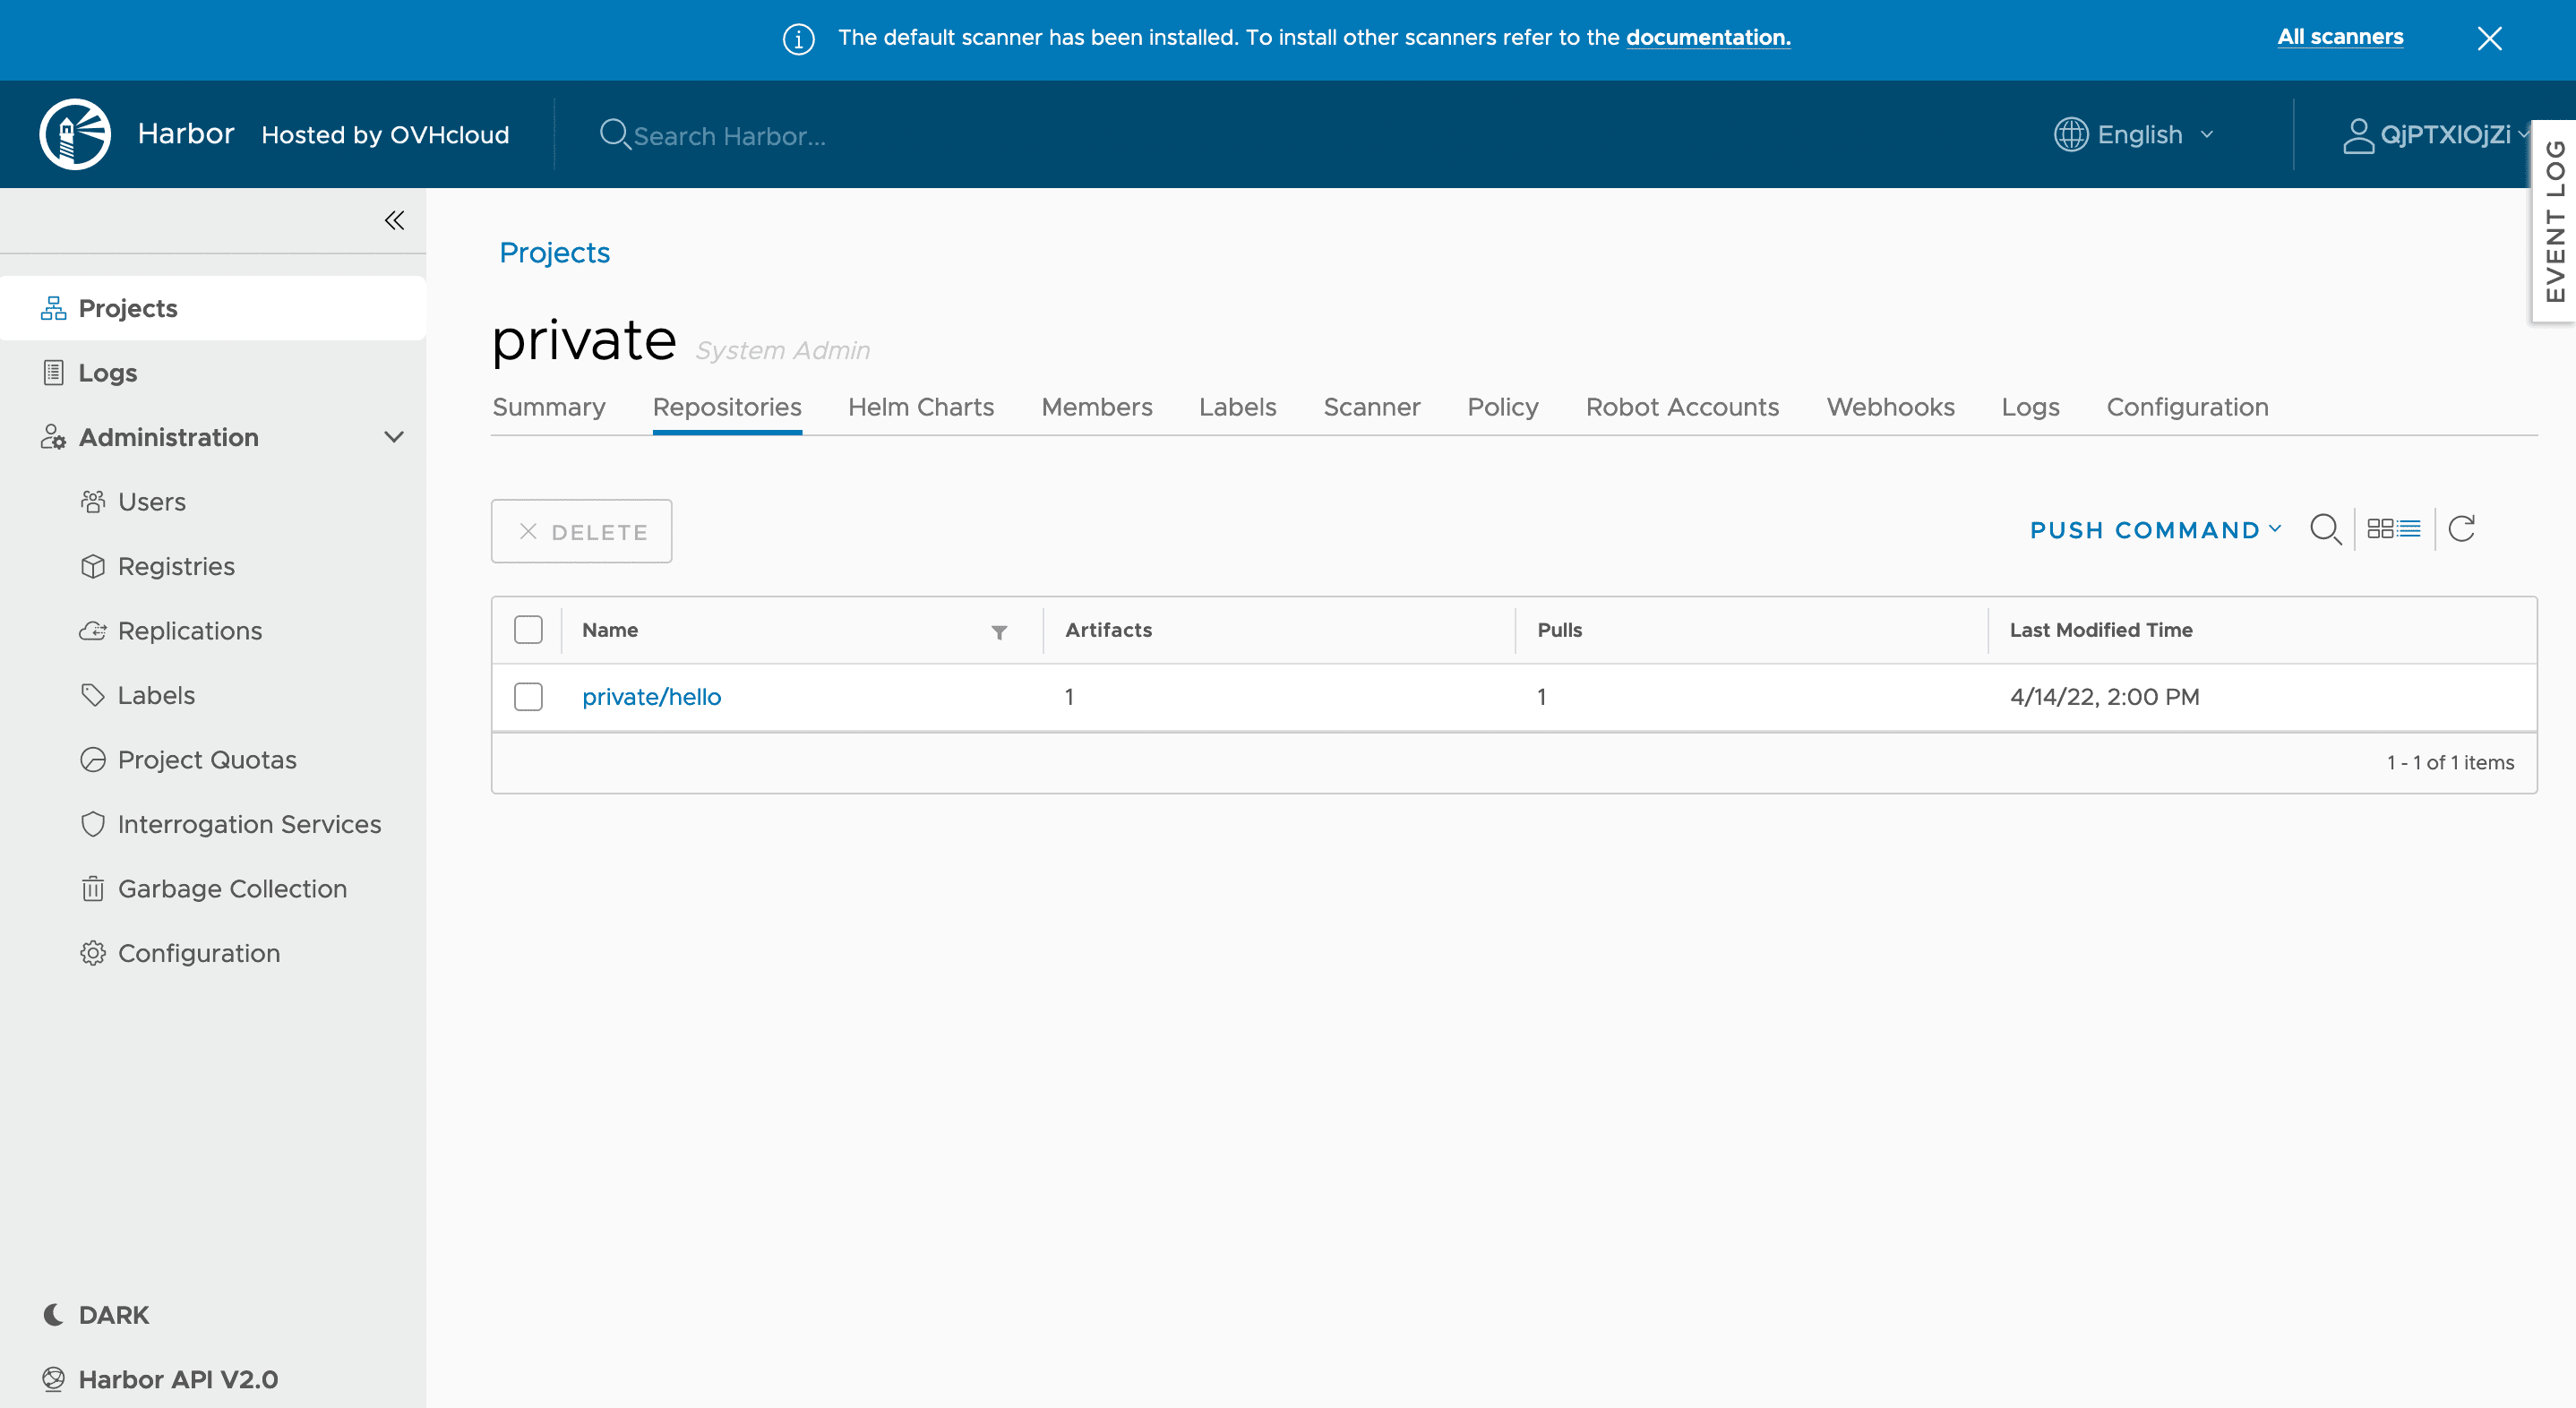
You should have at least one image in your Private Registry:
Instructions
Using the Harbor UI, you can scan your images on your private registry.
Check that you have enabled a vulnerability scanner
By default, when you create a Private Registry in order to enable a vulnerabilities scanner you need to choose a M or L plan.
With the M and L plans, OVHcloud installs and maintains a vulnerability scanner for you: Trivy.
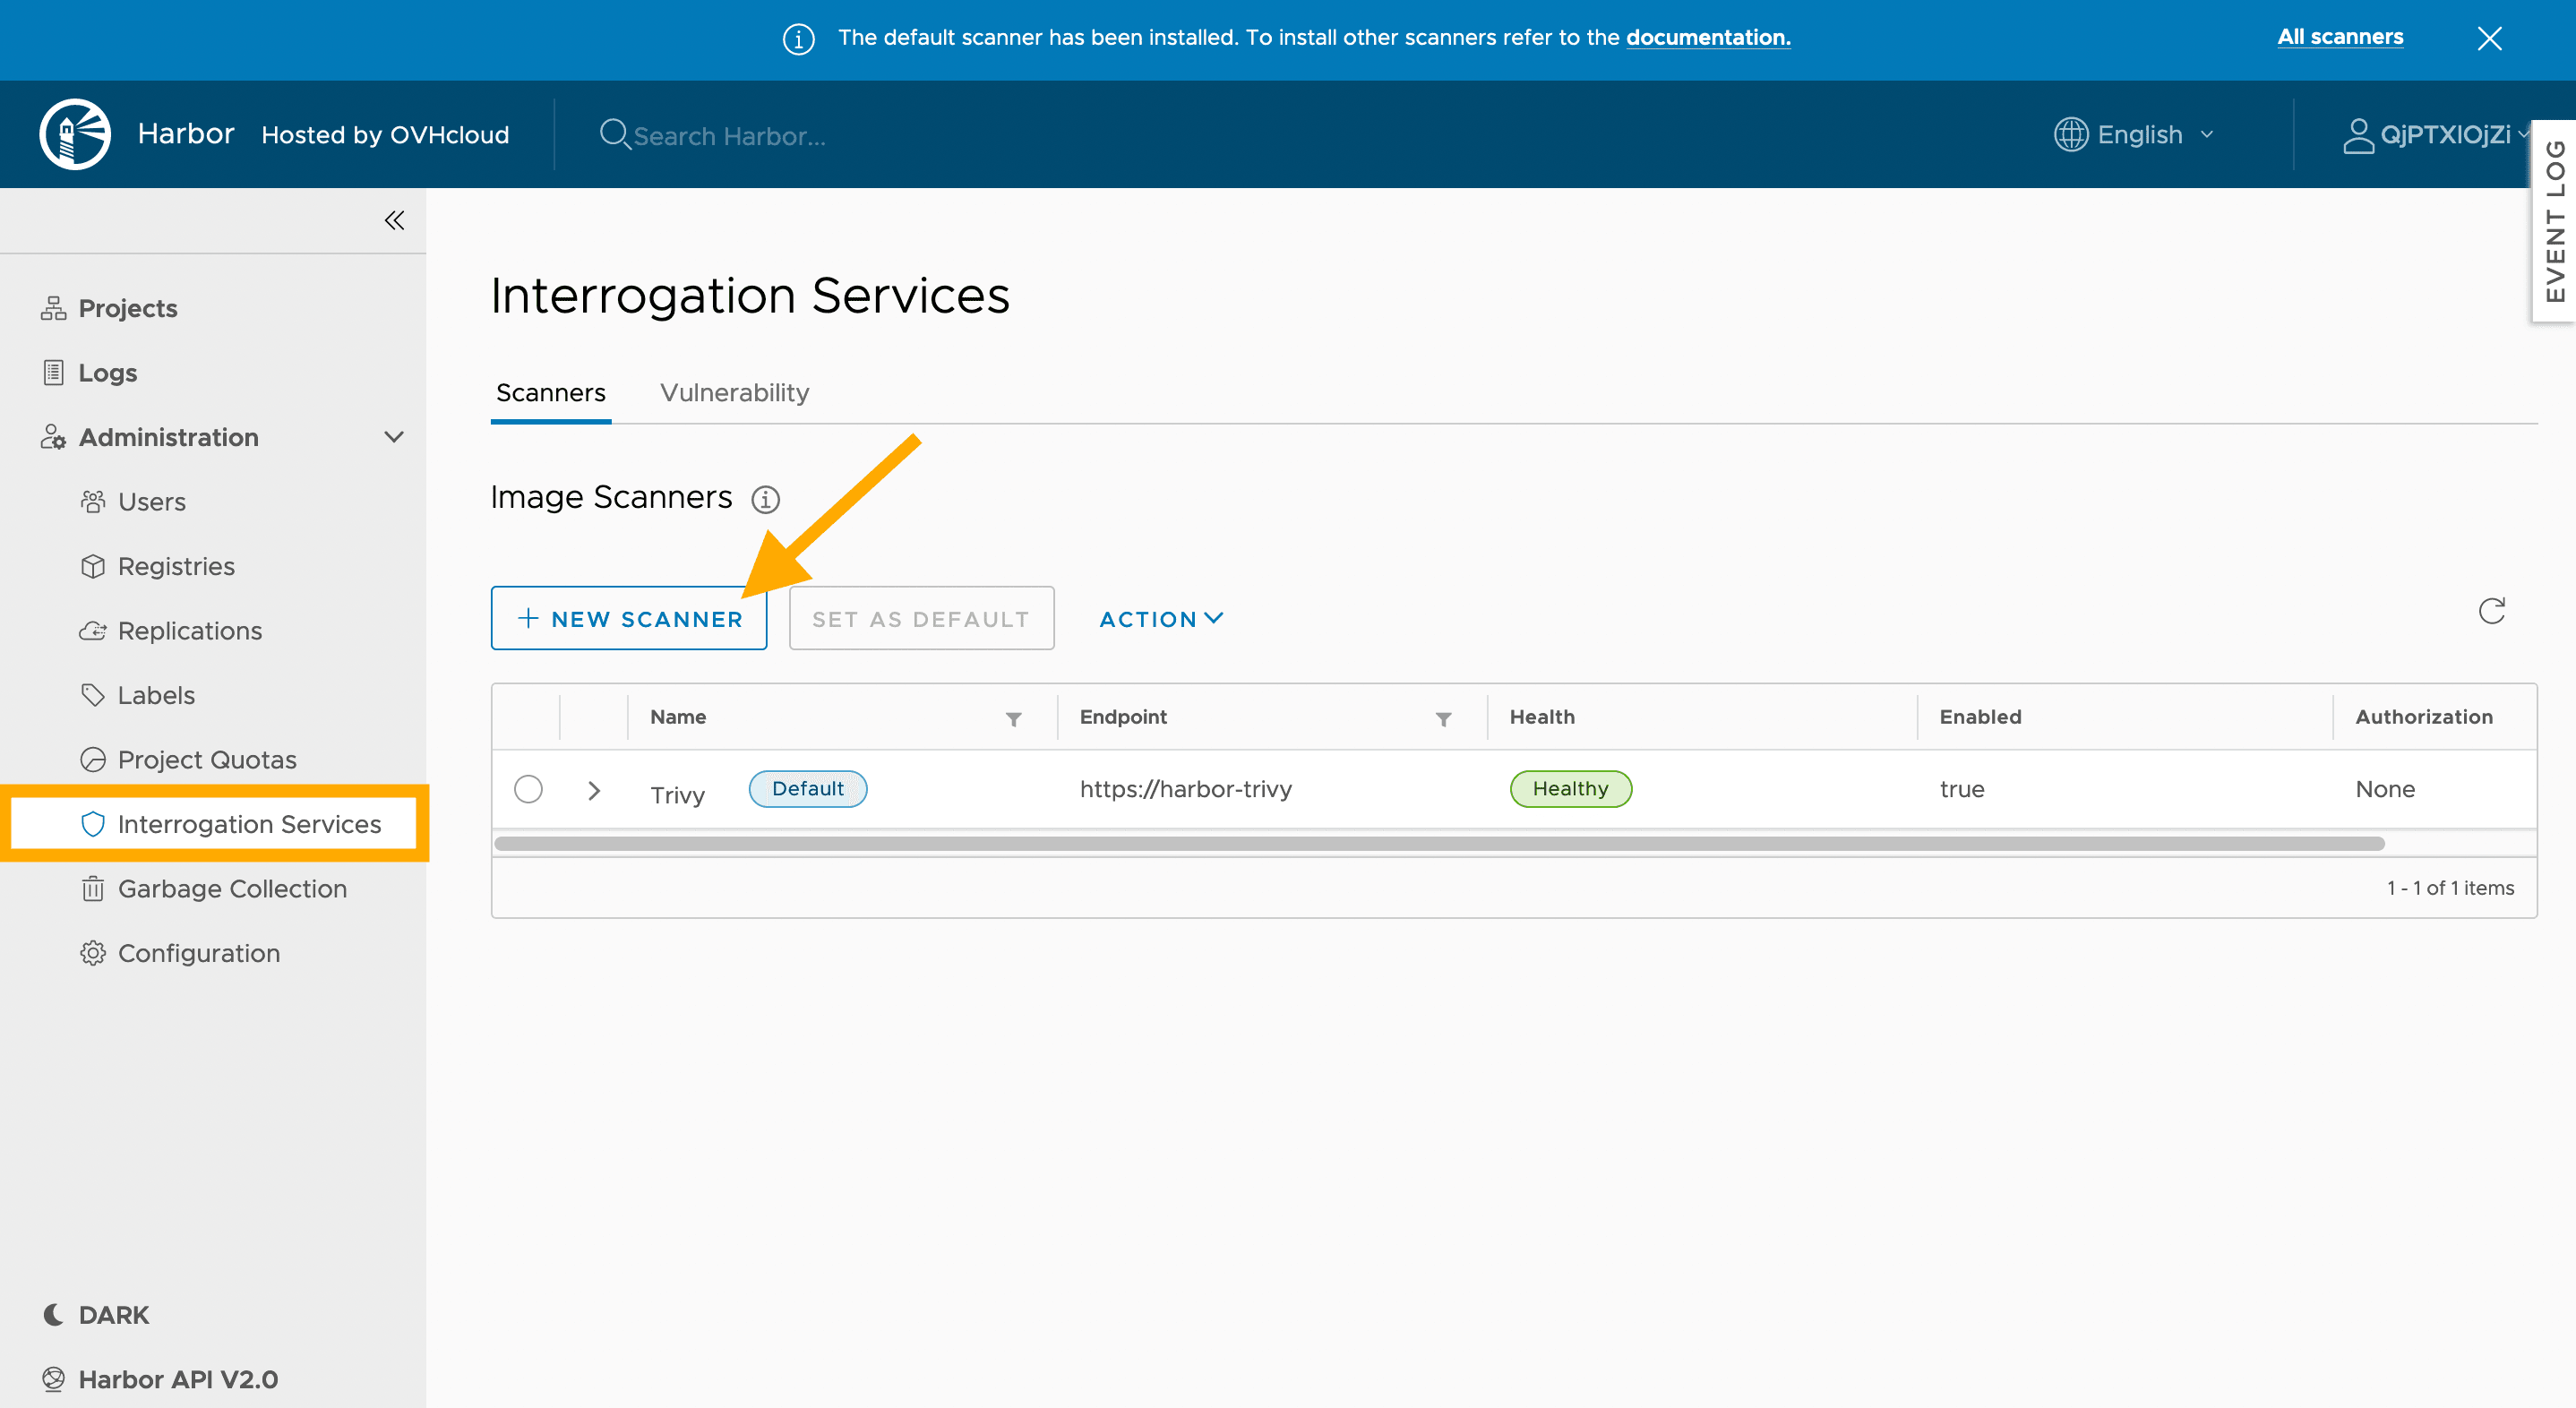
To verify if you have a vulnerability scanner in your private registry, go to Interrogation Services in the side navigation bar.
As you can see, Trivy is installed and ready to use.
If you want to manually add a vulnerability scanner, you can also do it with the New Scanner button. However, it will not be updated and maintained by OVHcloud.
Scan a Docker image manually
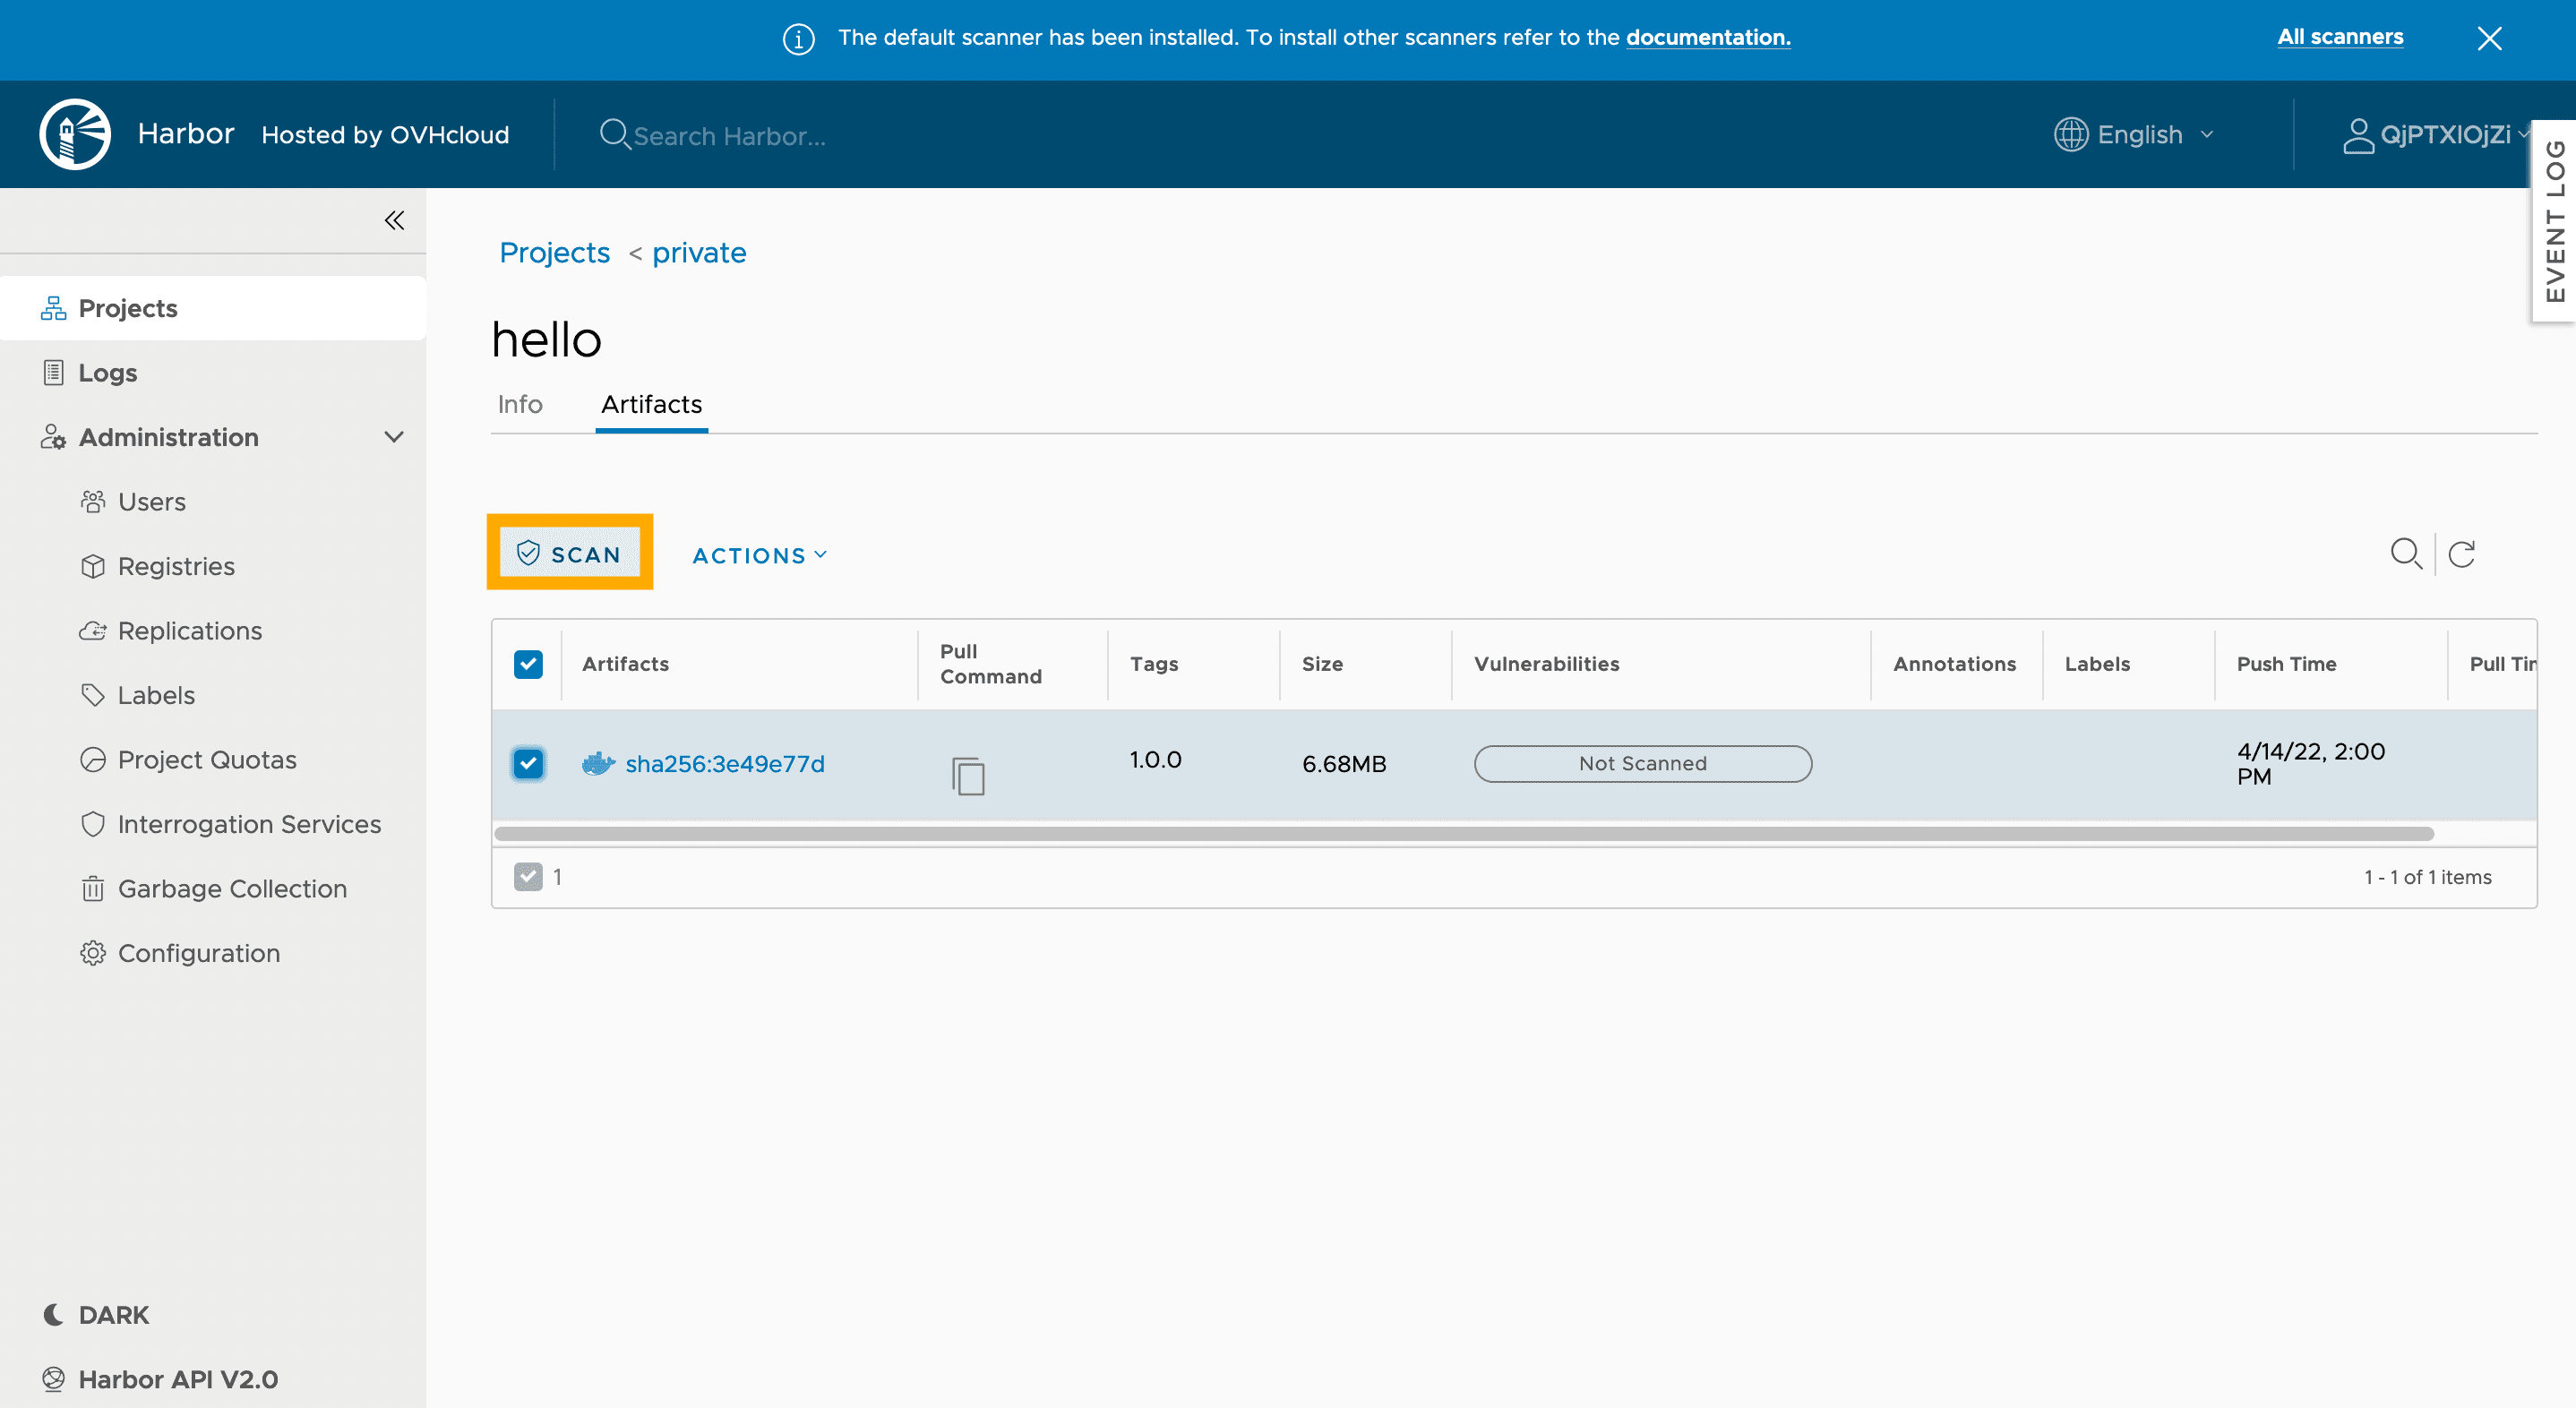
You can manually scan a Docker image. To do that, access your project, select an image, and click on Scan.
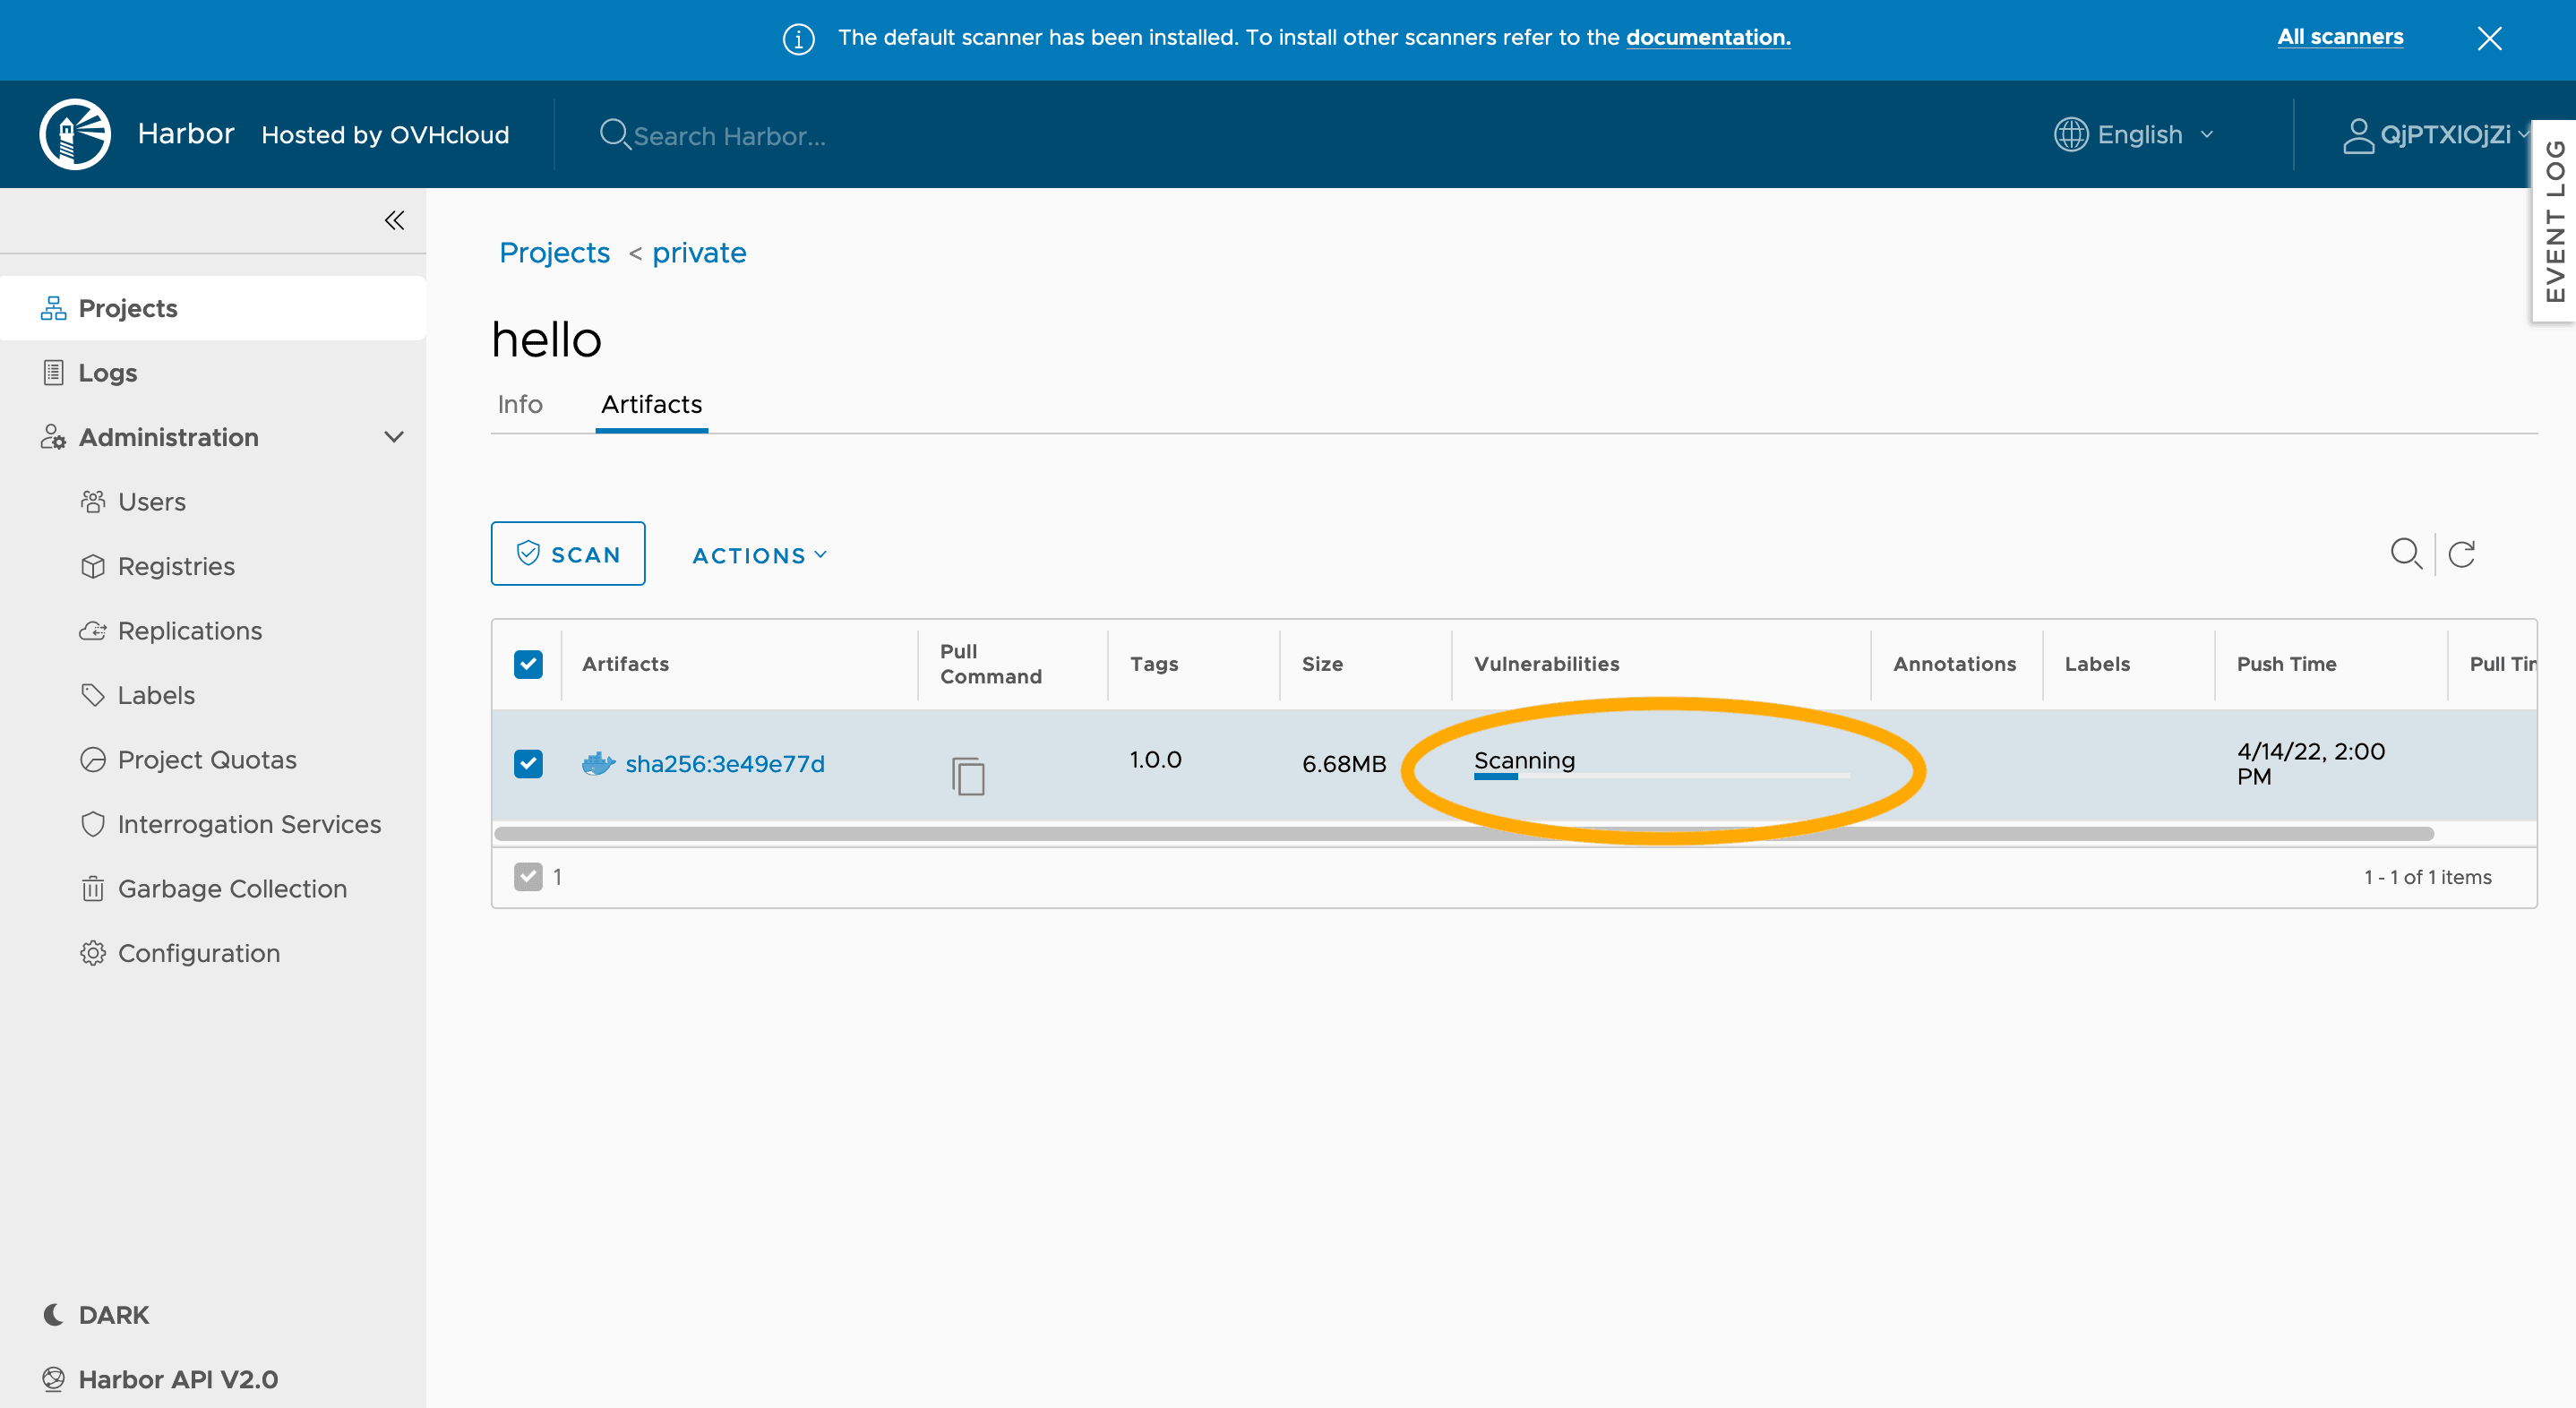
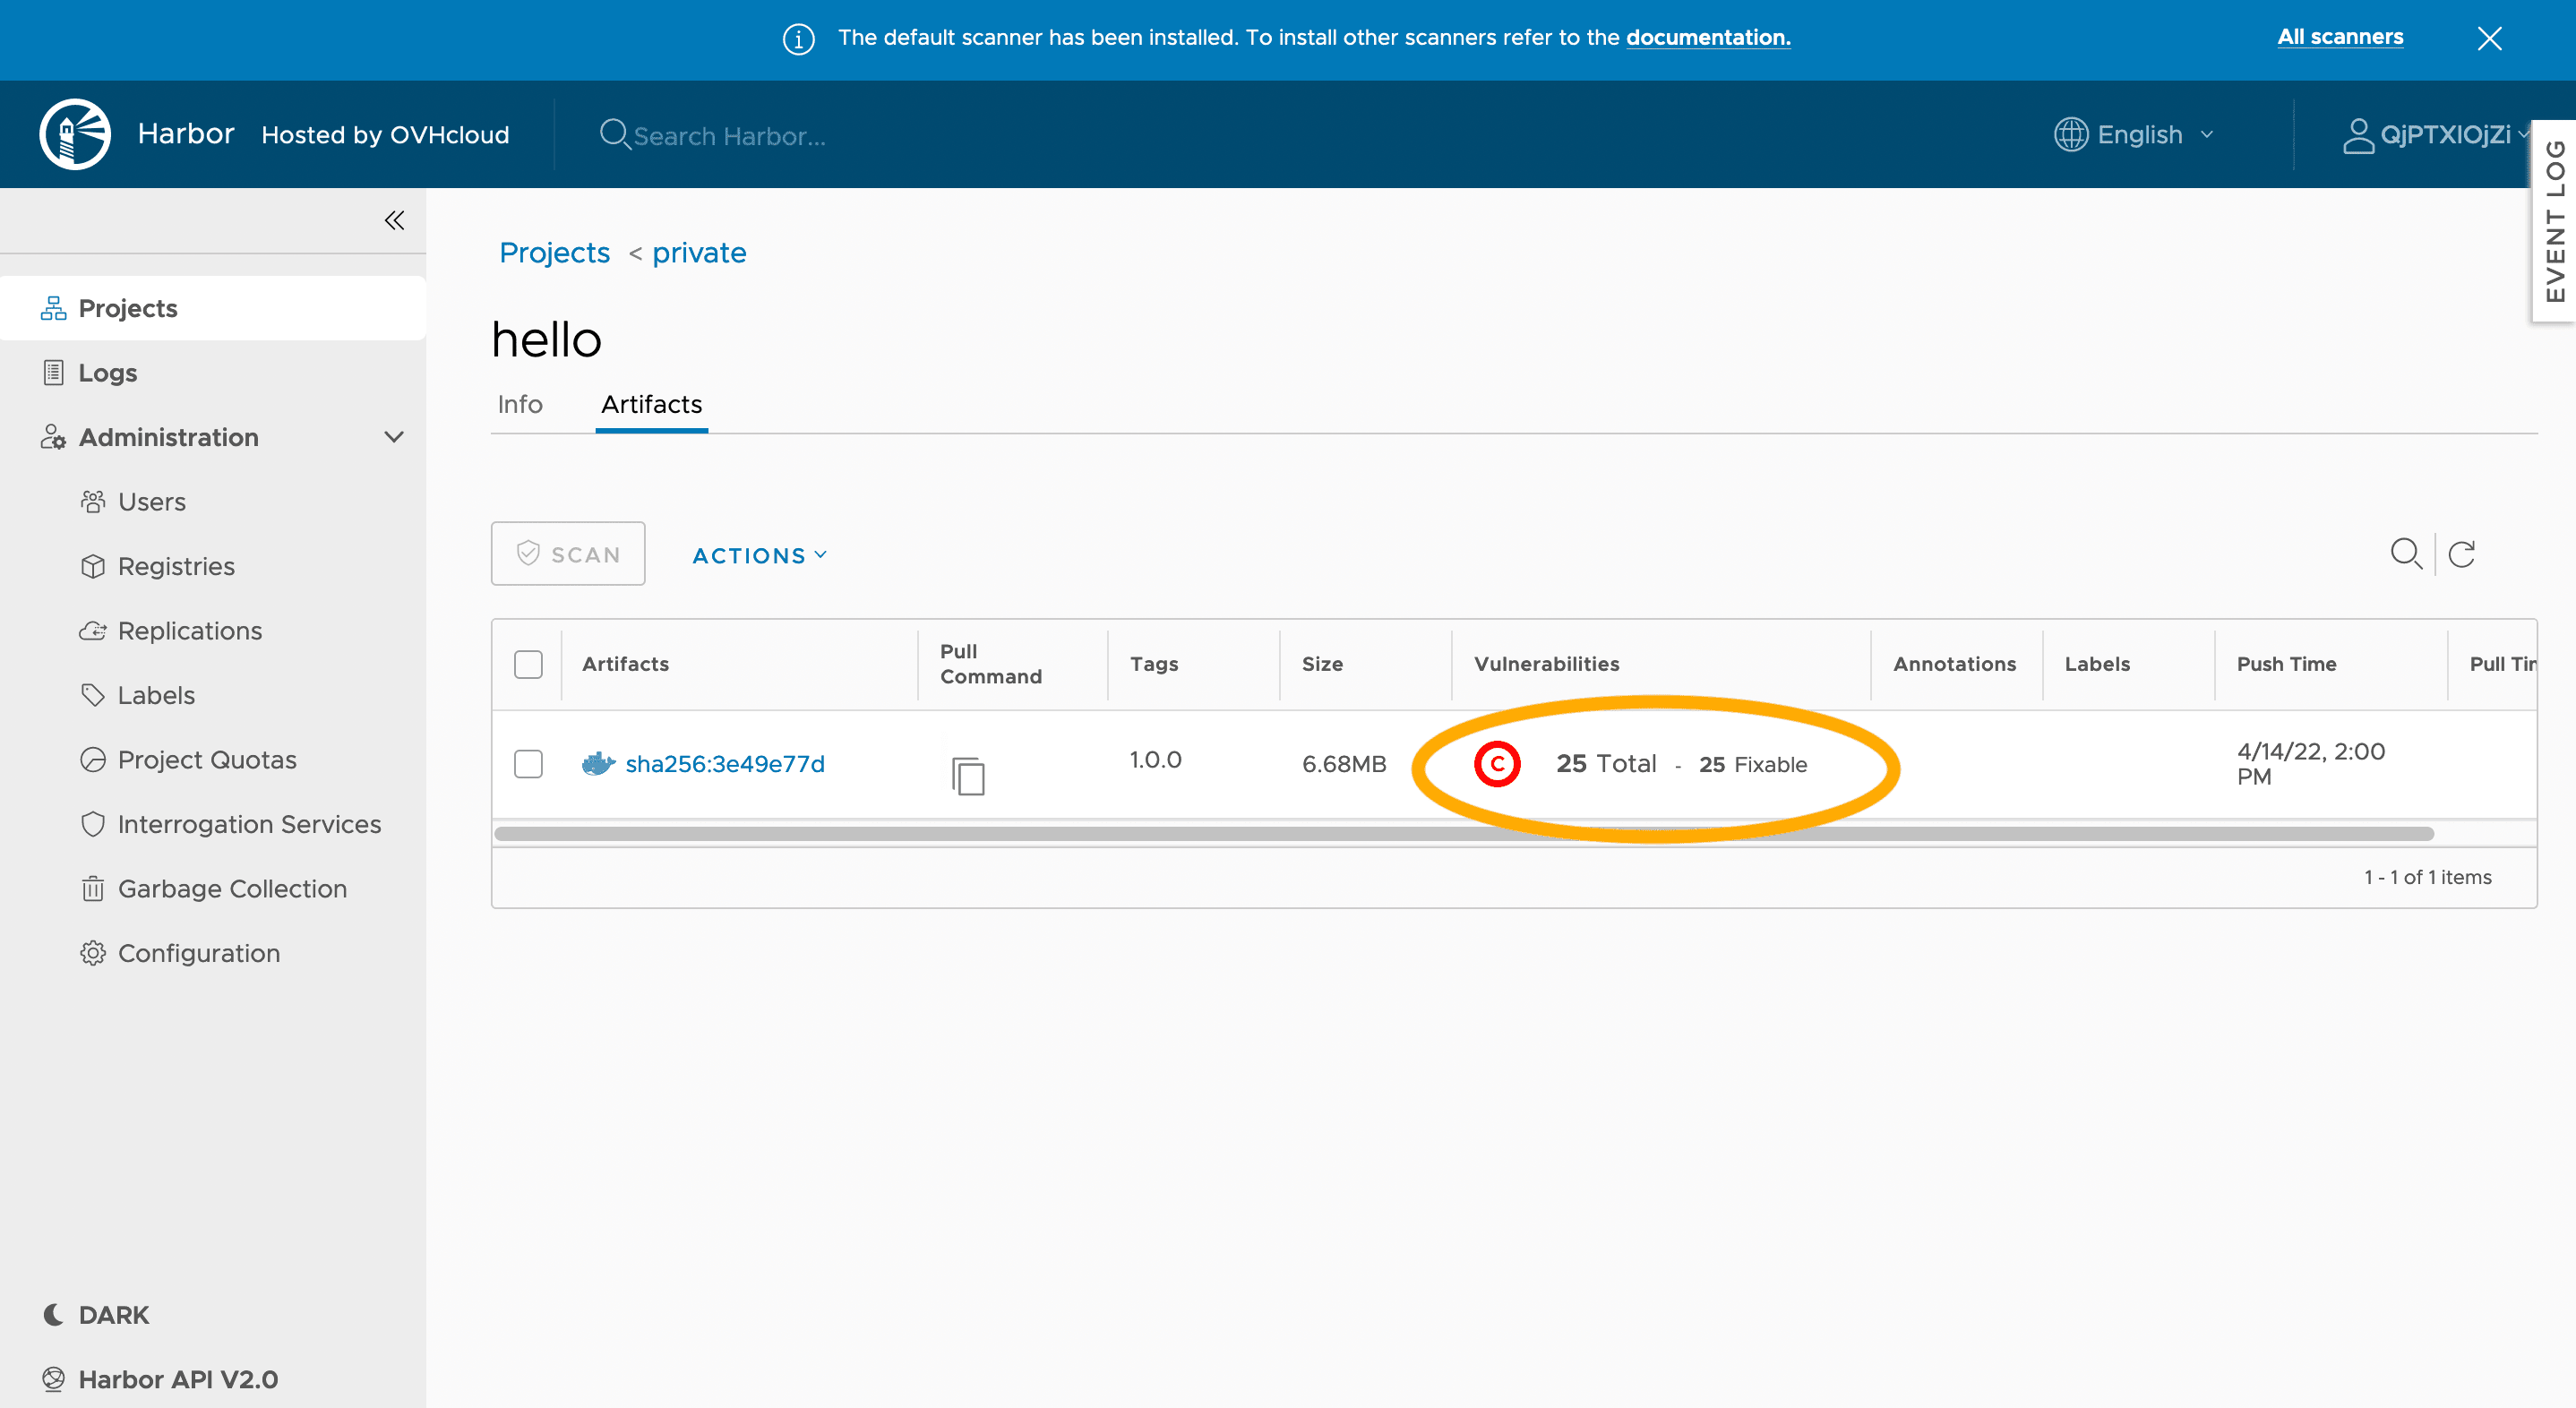
The scanner starts scanning the image.
The number of vulnerabilities is displayed.
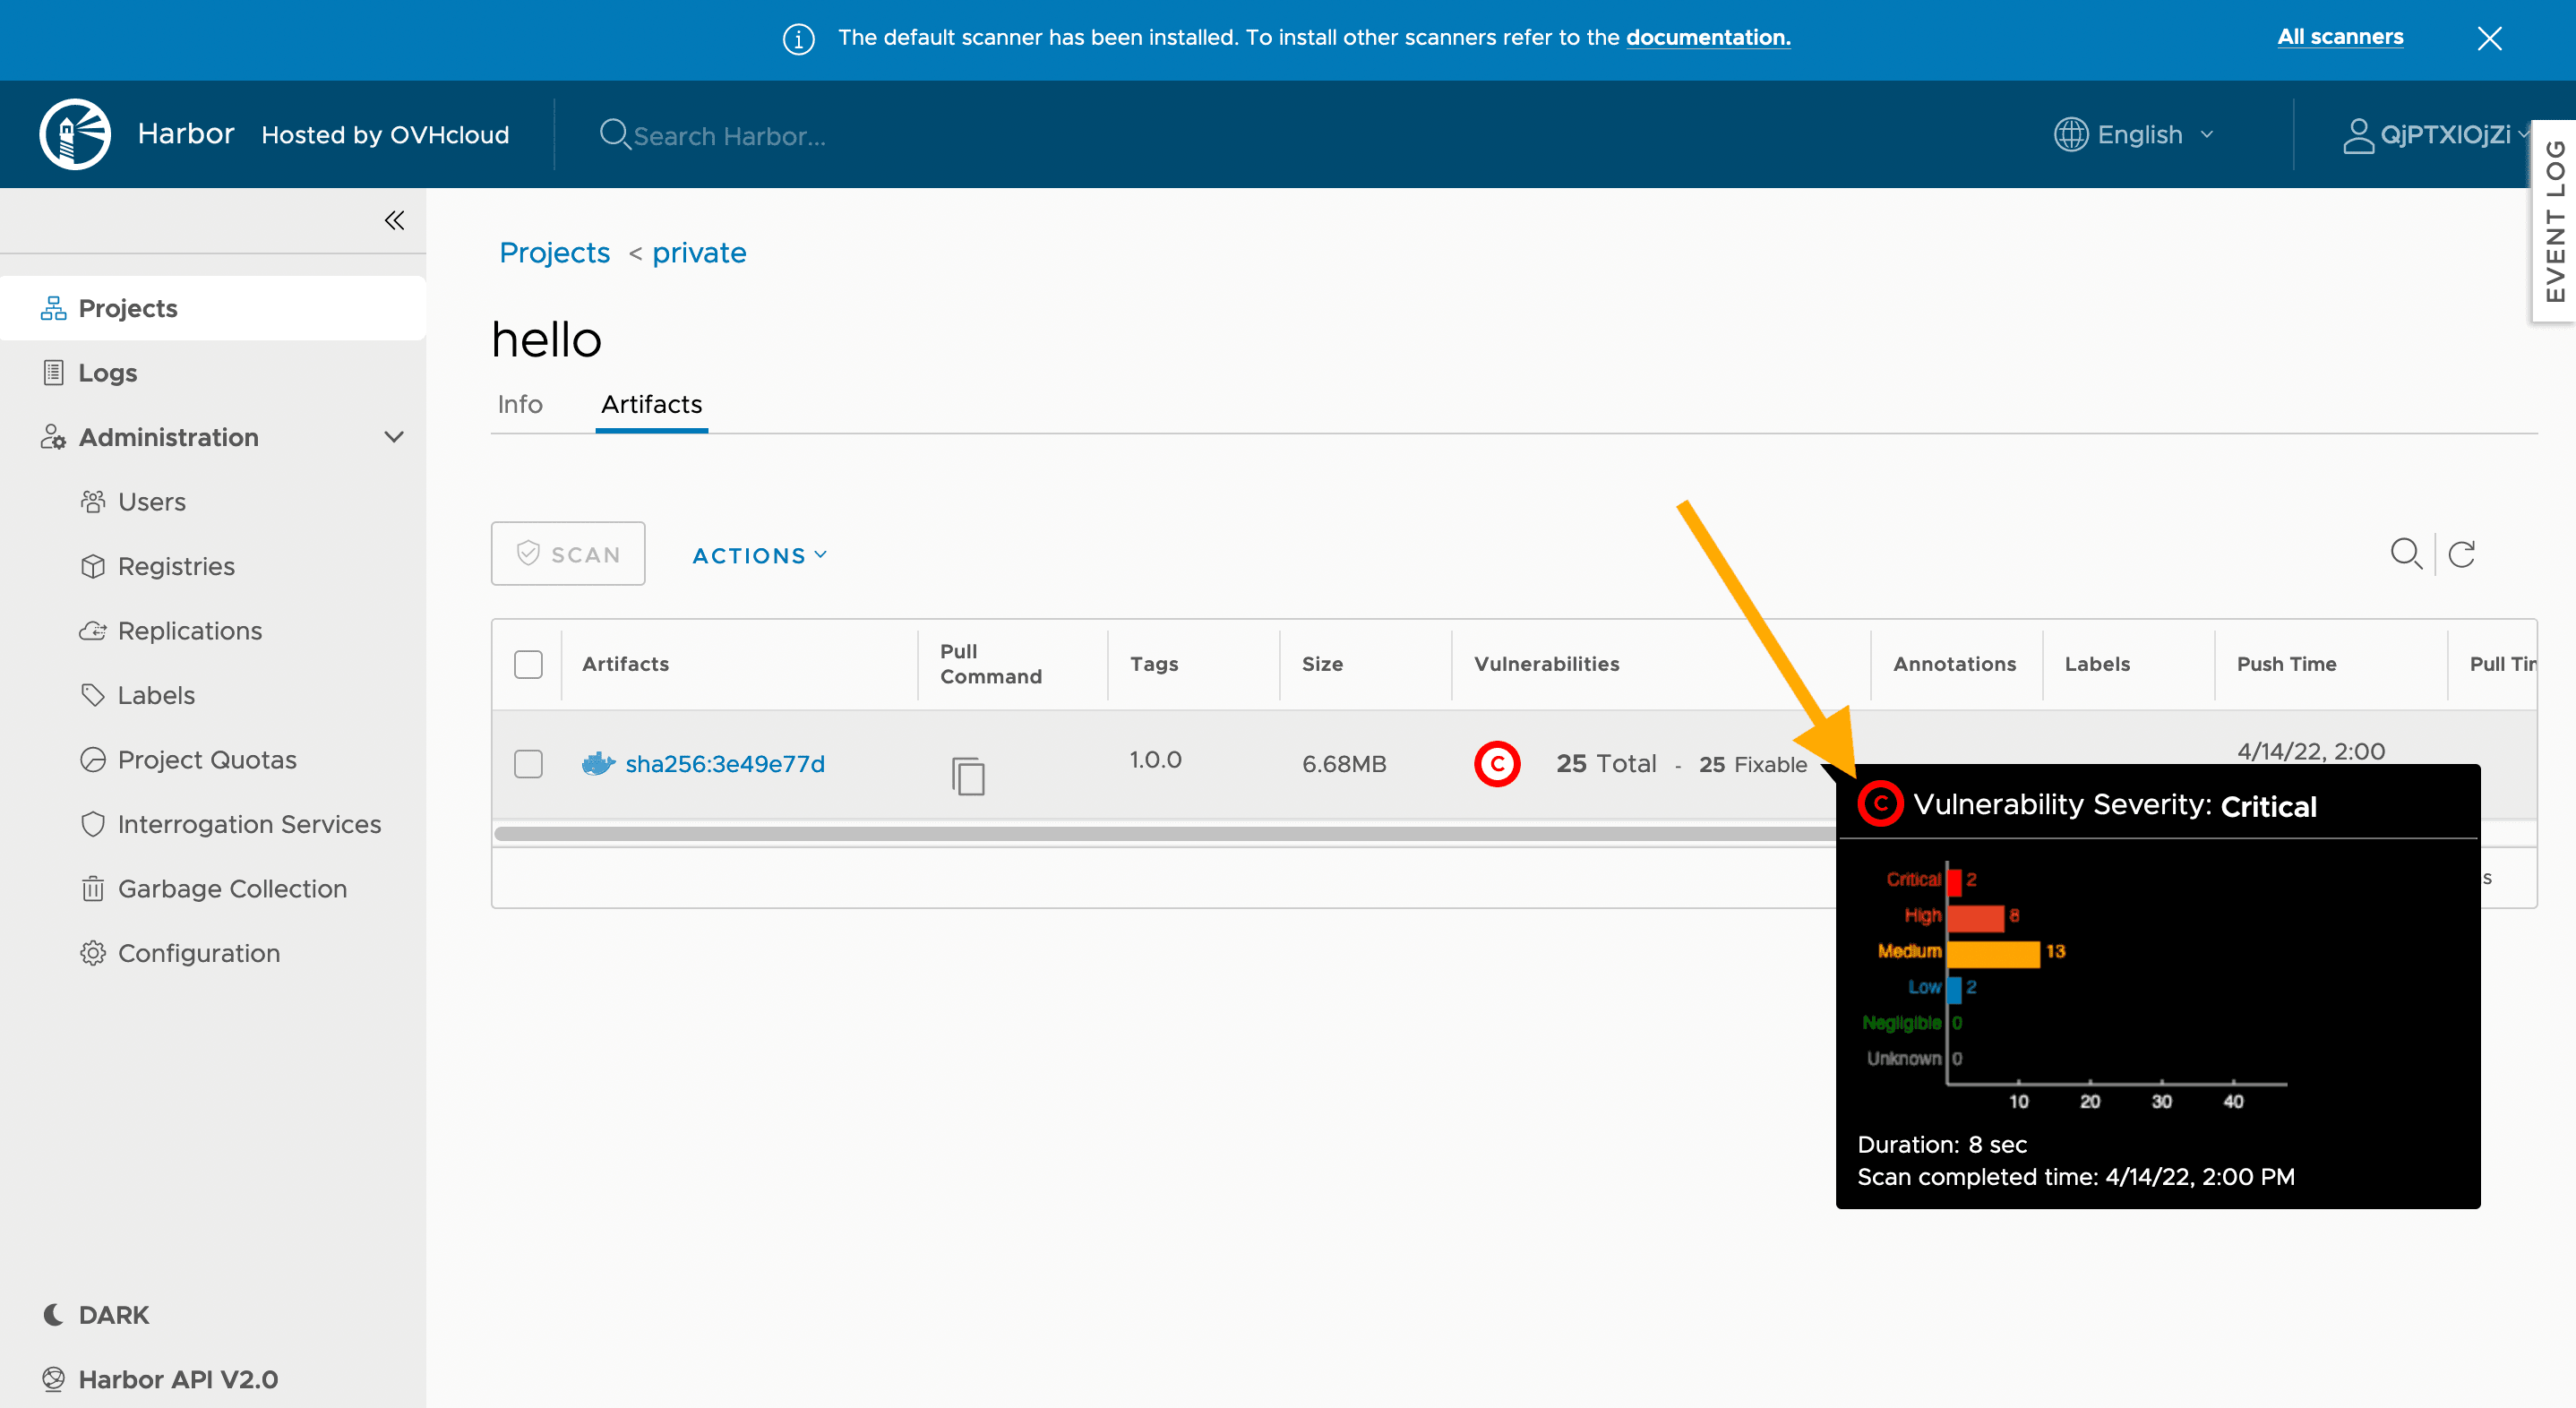
When you hover over the vulnerabilities column, a chart with the vulnerabilities' severity is displayed.
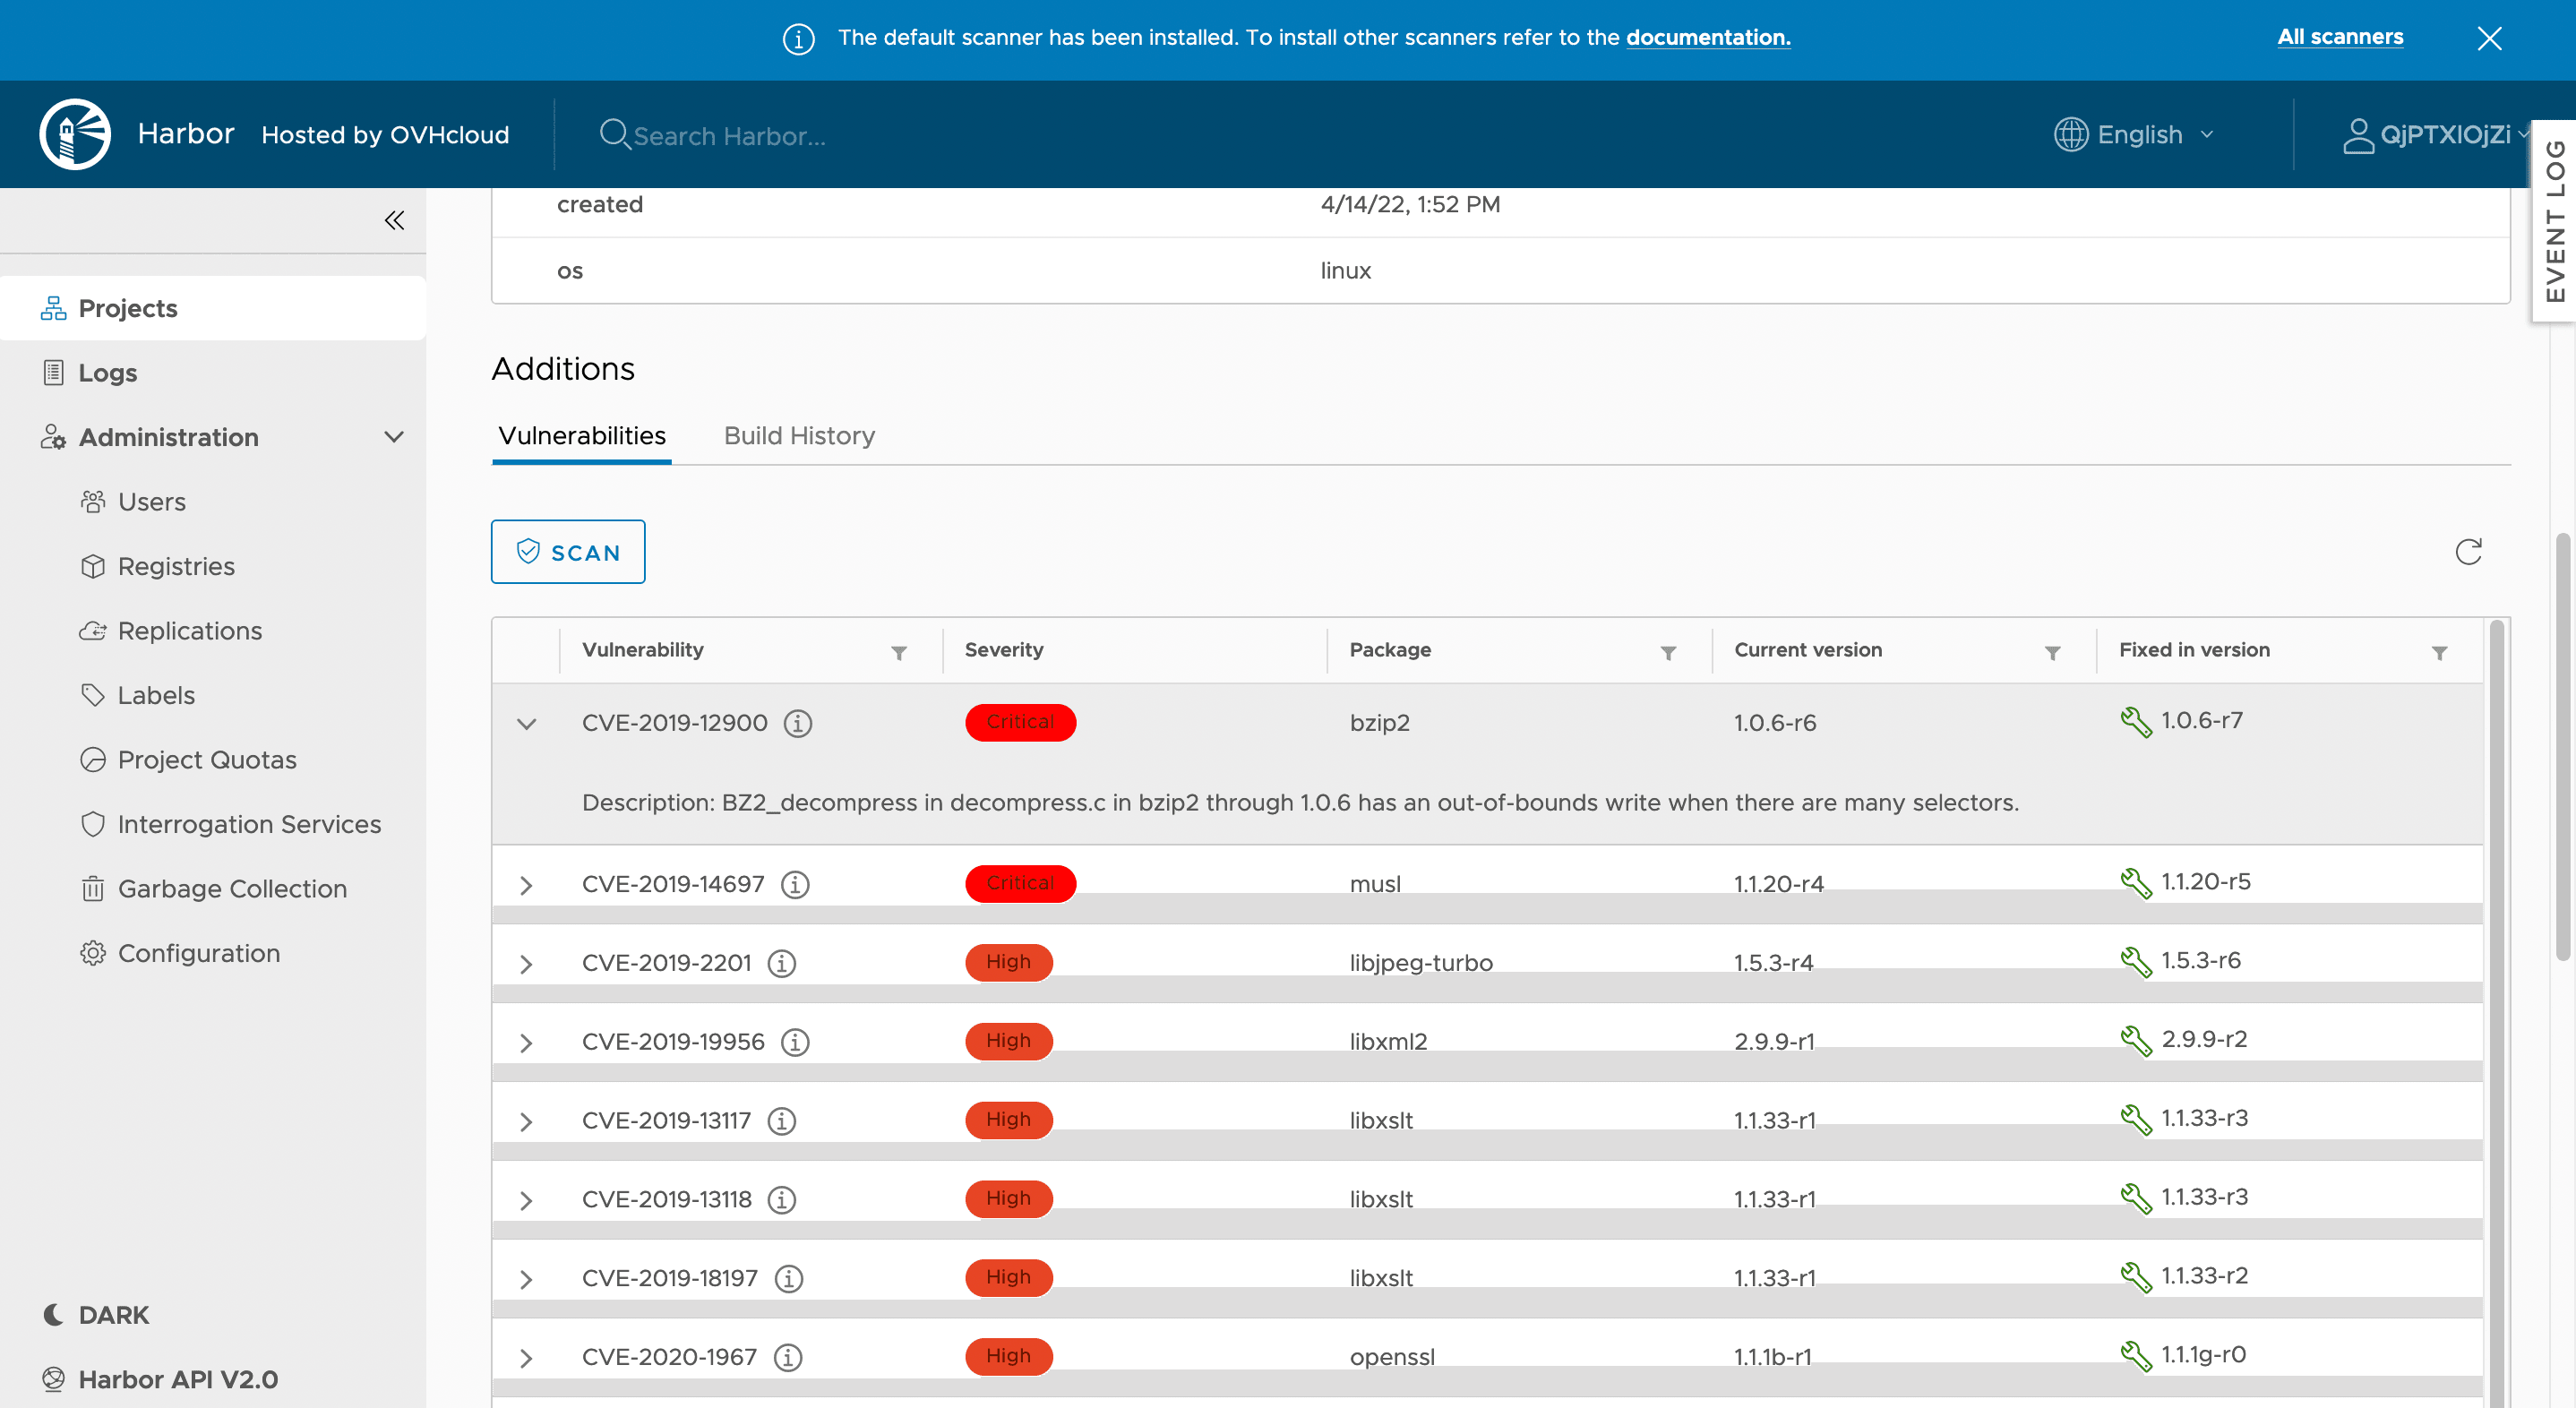
Click on the image ID to display all vulnerabilities, ranked by severity.
Scan all the images
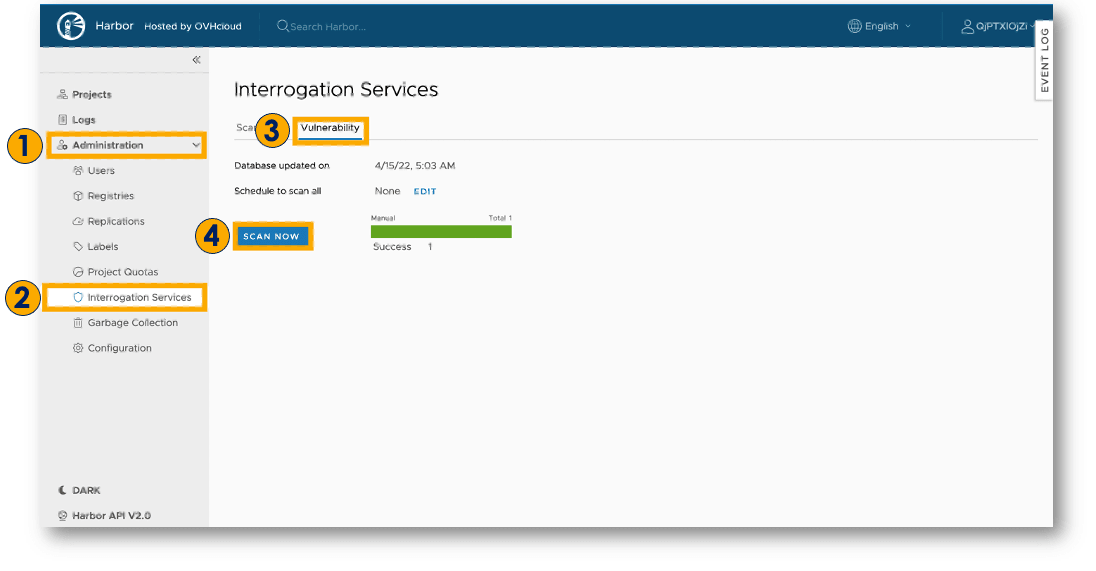
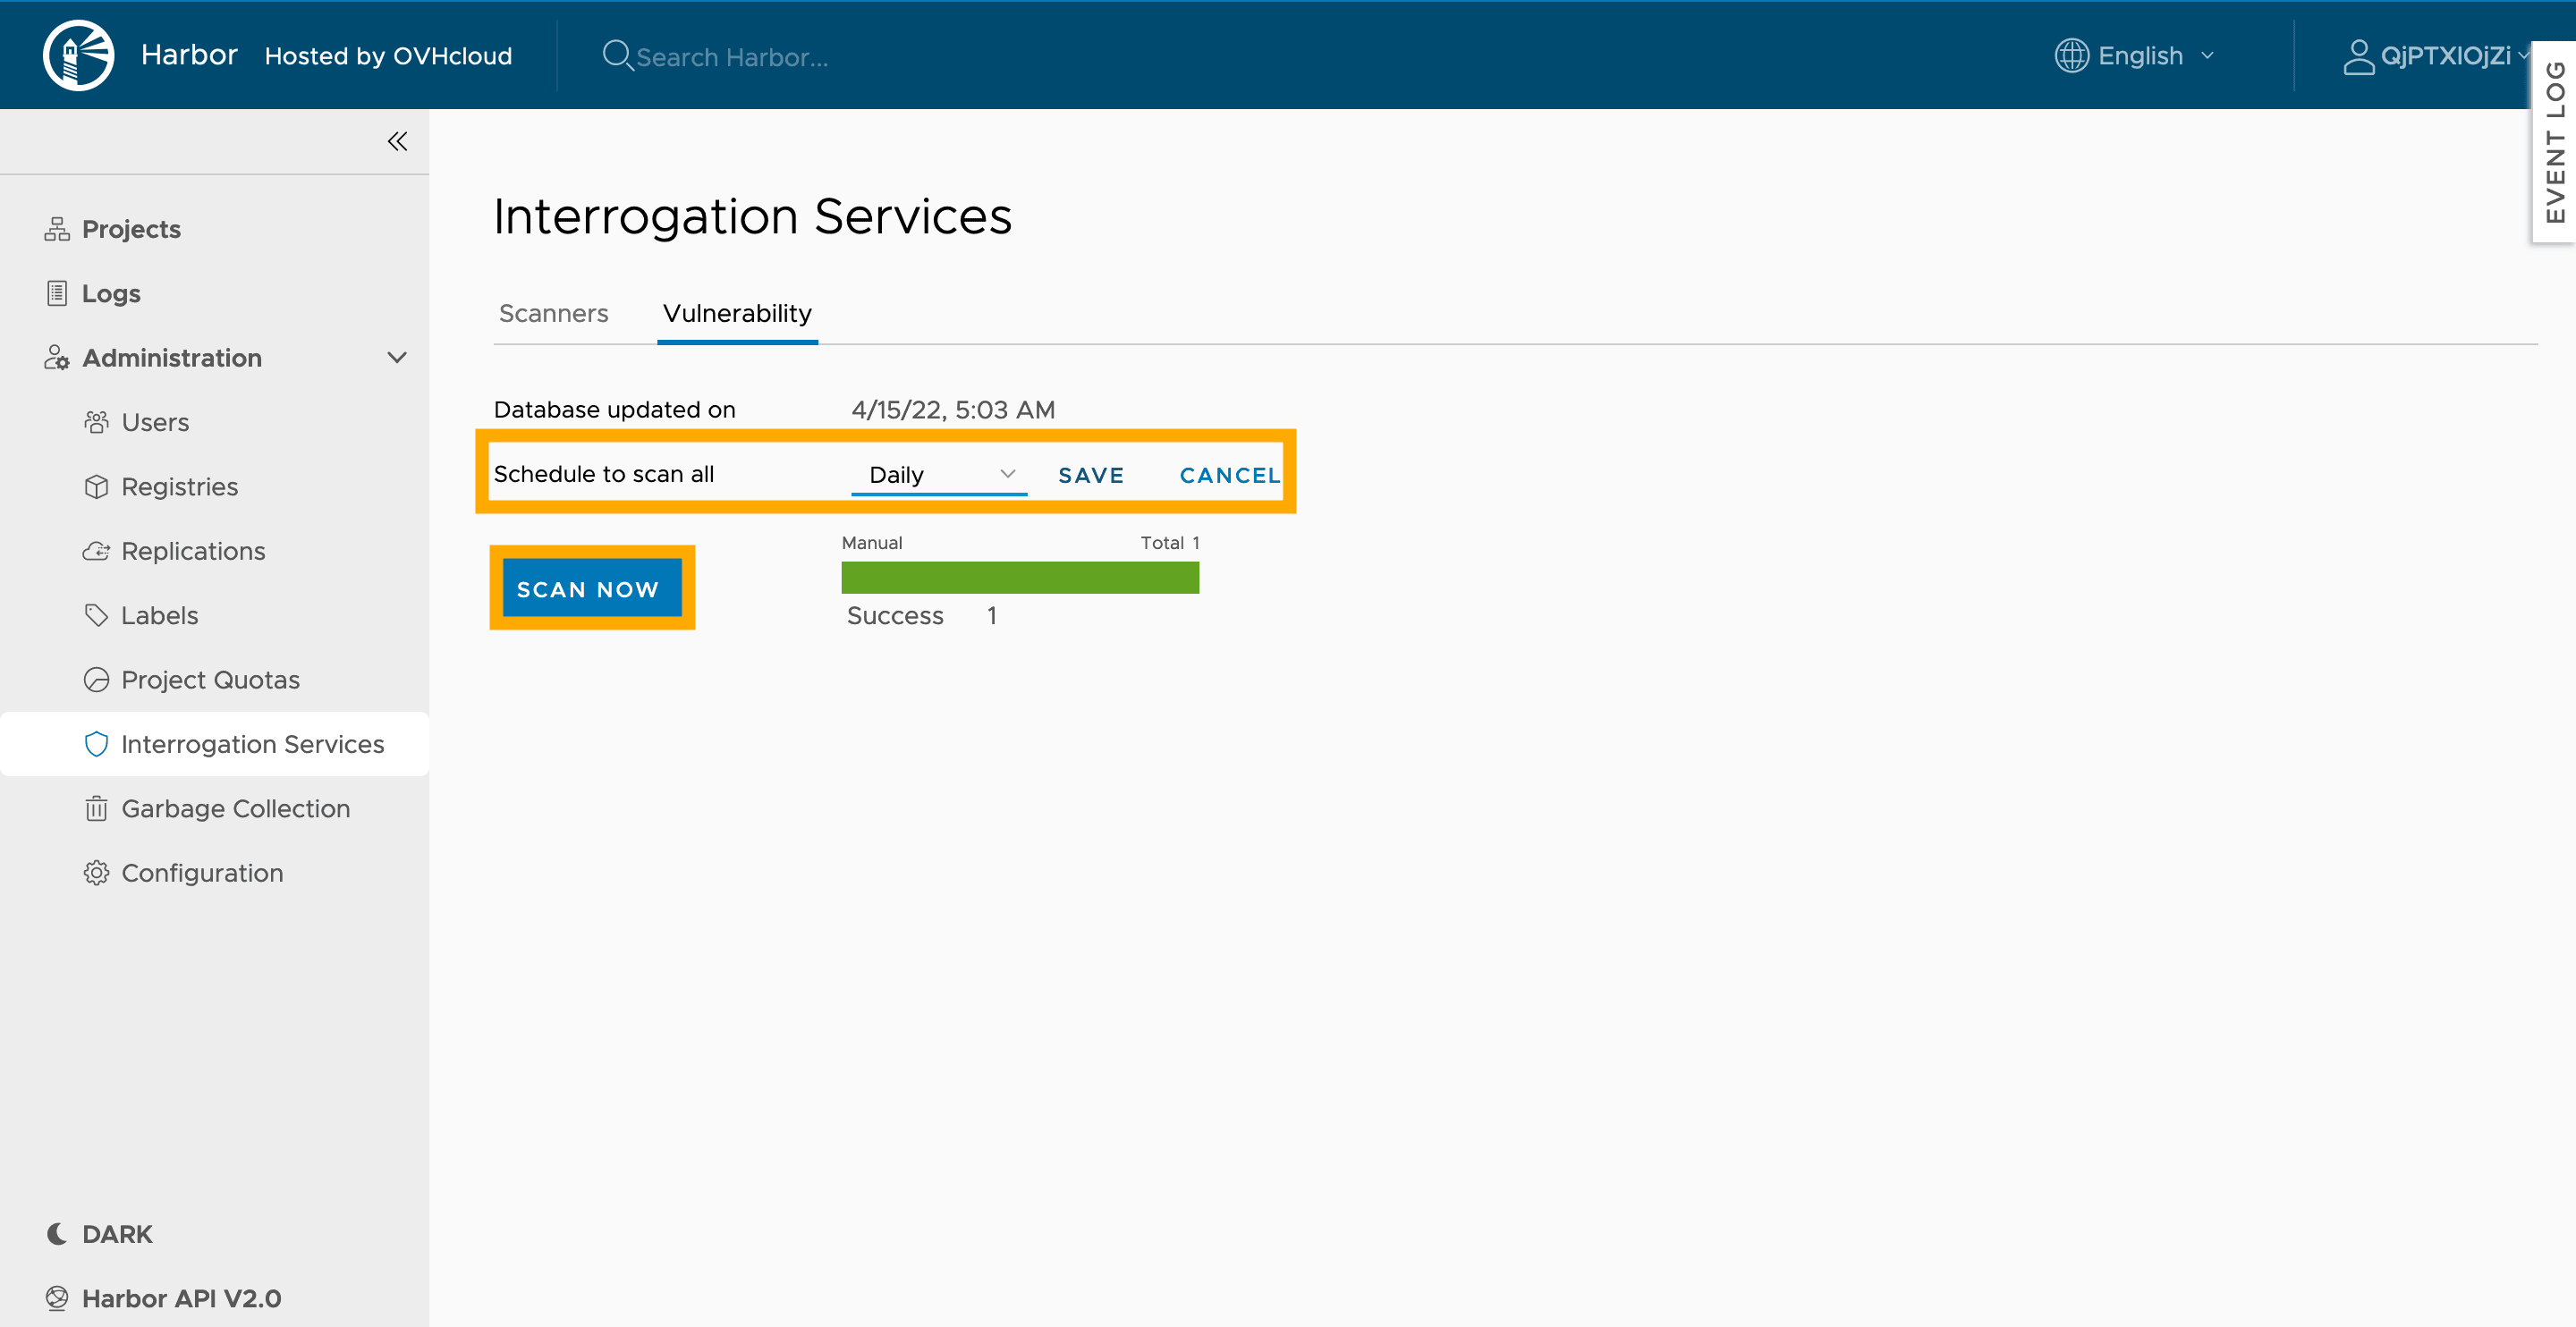
You can also scan all your images manually in your private registry.
To do that:
- Click
Administrationin the side navigation menu. - Select
Interrogation Services. - Go to the
Vulnerabilitytab. - Click
Scan Now.
Scan all images regularly
You can schedule a scan:
- hourly
- daily
- weekly
- when you want (enter as a cron format)
For that, select the scheduling and click on the Save button.
Go further
Browse all the Managed Private Registry (MPR) guides.
Browse the rest of the OVHcloud US documentation for guides on our other products and services.
Learn more about Managed Private Registry on the OVHcloud US website.