
Using OpenSearch Dashboards with Logs Data Platform
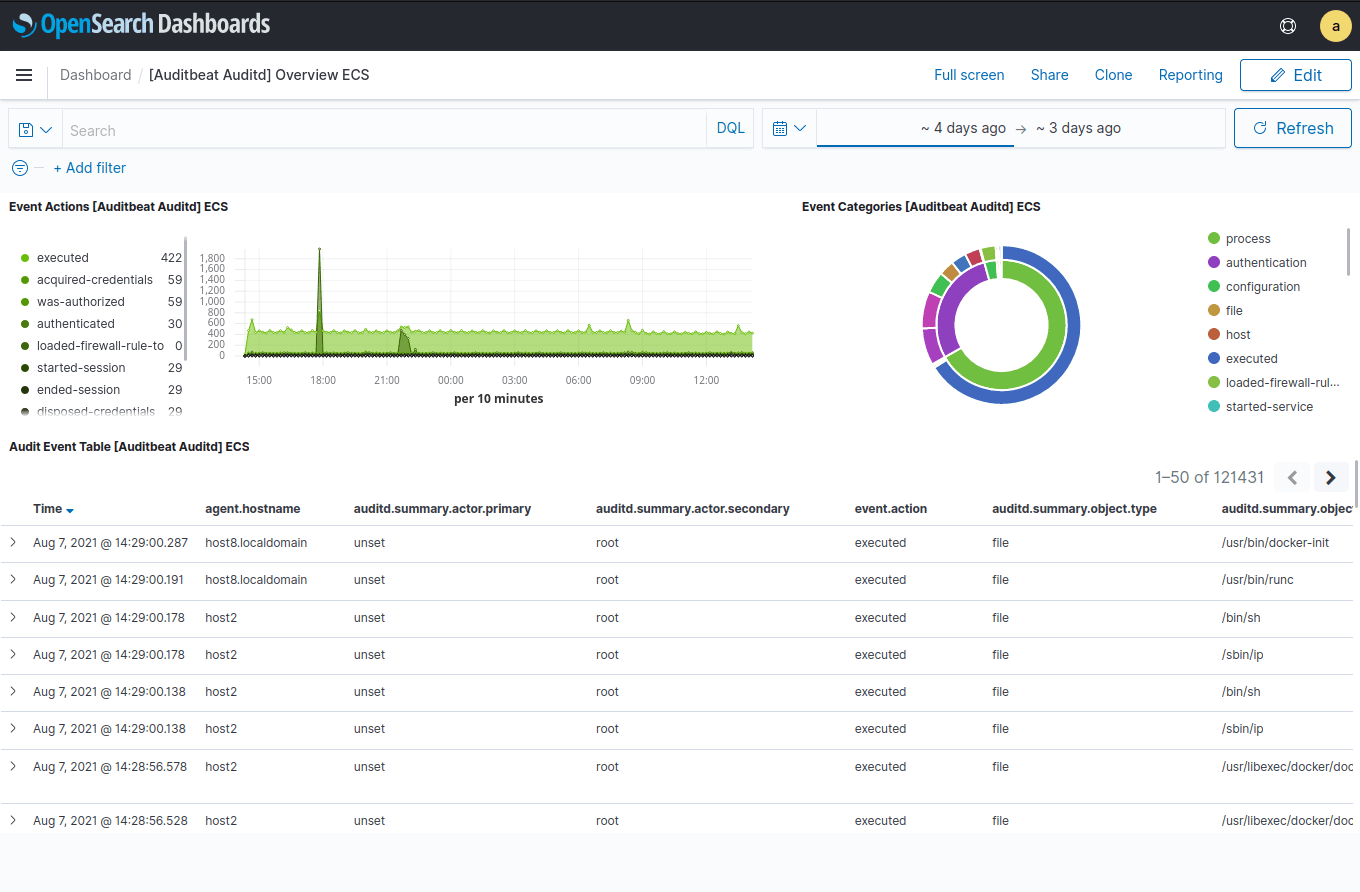
Learn how to unleash the full power of OpenSearch Dashboards and craft some beautiful Dashboards from your logs.
After some training you will be able to do this kind of Dashboard:
Requirements
- the ability to send logs on a stream you own (see our Quick Start for Logs Data Platform guide)
Instructions
Create your Stream Alias
To access your logs from OpenSearch Dashboards, you will need to set up an OpenSearch Alias and link it to your Graylog streams. To do so:
-
Log in to the OVHcloud Control Panel and access your Logs Data Platform service.
-
In the Alias tab, click on the
+ Add an aliasbutton. -
Choose a name and define a description for your alias.
-
Save the entry by clicking the
Savebutton.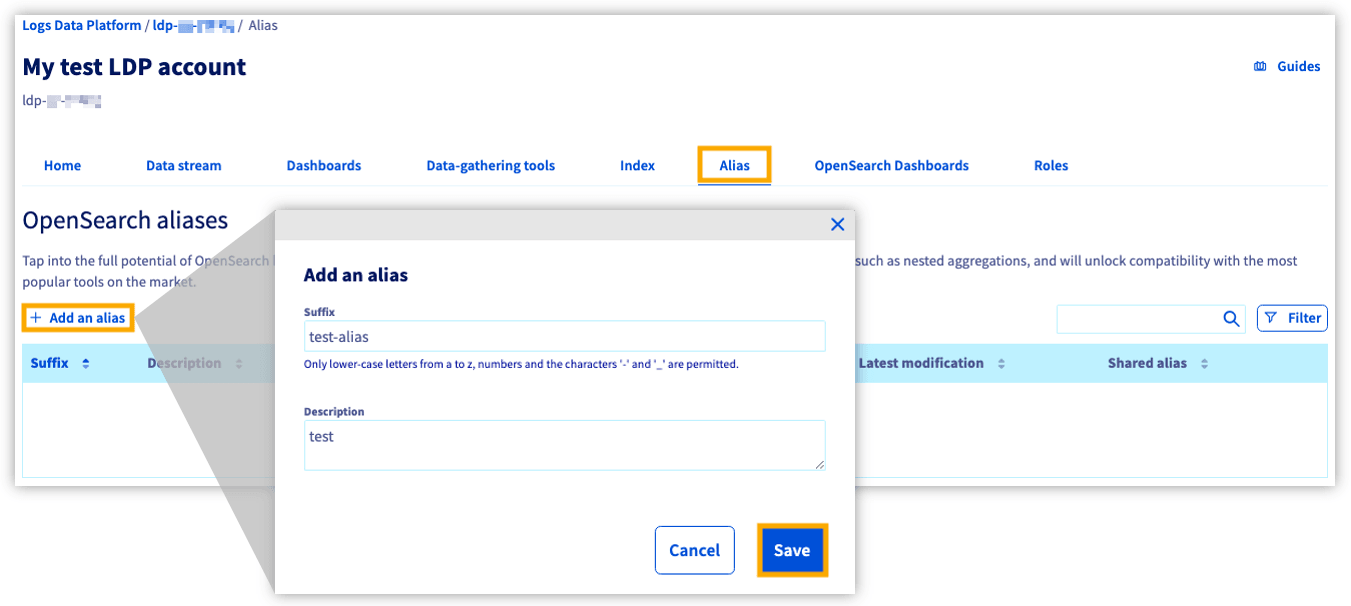
-
Once the alias has been created, use the more options
...button to the right and selectAttach content to the aliasoption.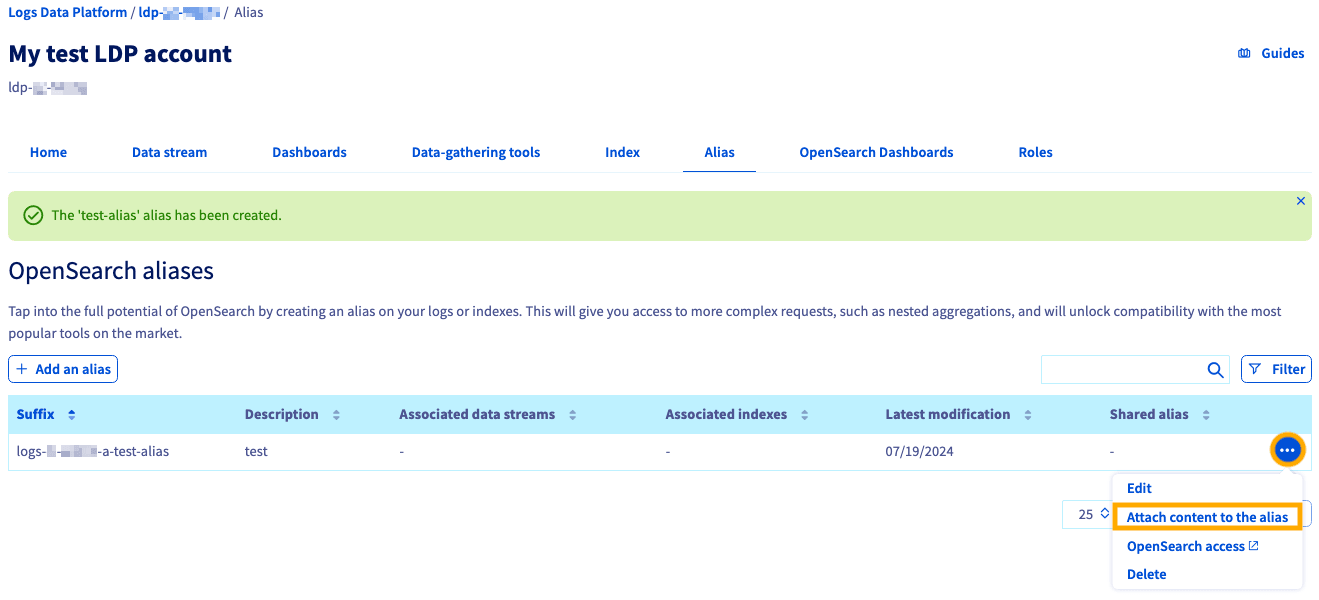
- Define the Graylog streams you want to associate with your alias.
So now Logs Data Platform knows which stream you want to browse. Now let's configure OpenSearch Dashboards and see if it works!
Access your OpenSearch Dashboards instance
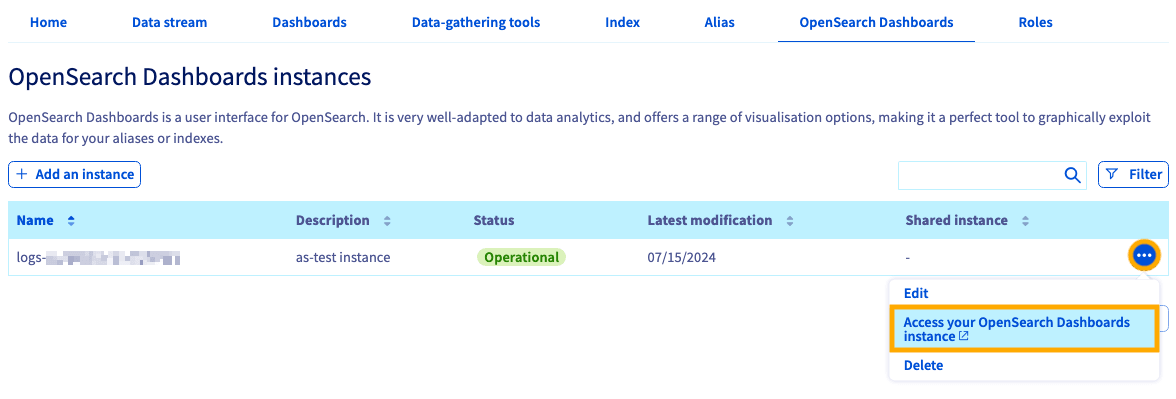
To create your OpenSearch Dashboards instance, click on the OpenSearch Dashboards tab. Click on Add an instance, add a description, and click on Order to launch the creation of your instance. Your instance will be created and delivered in approximately 20 minutes.
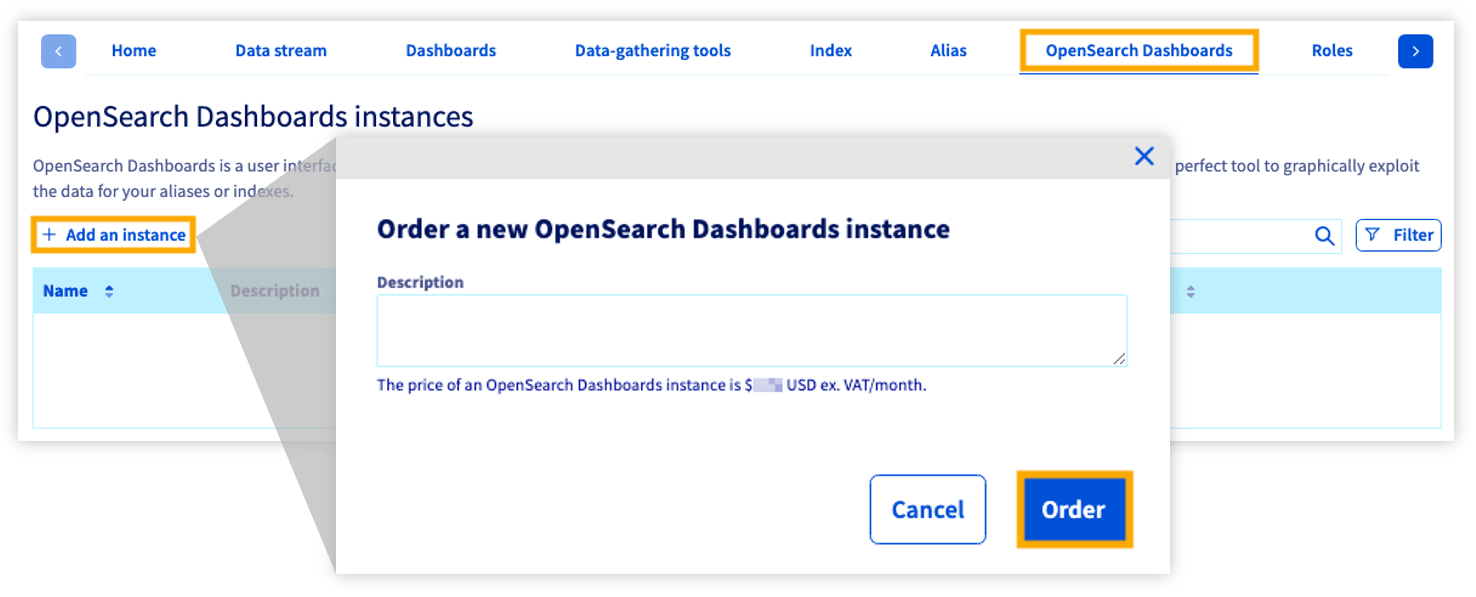
Use the more options ... button to the right and select Access to your OpenSearch Dashboards instance option to be redirected.
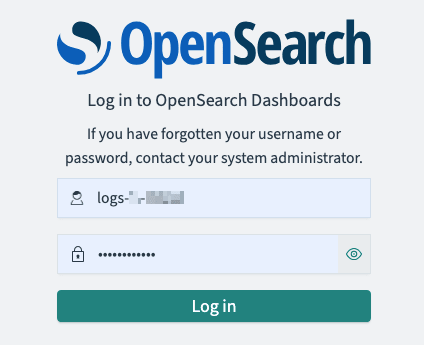
Once there, use your LDP credentials to sign in.
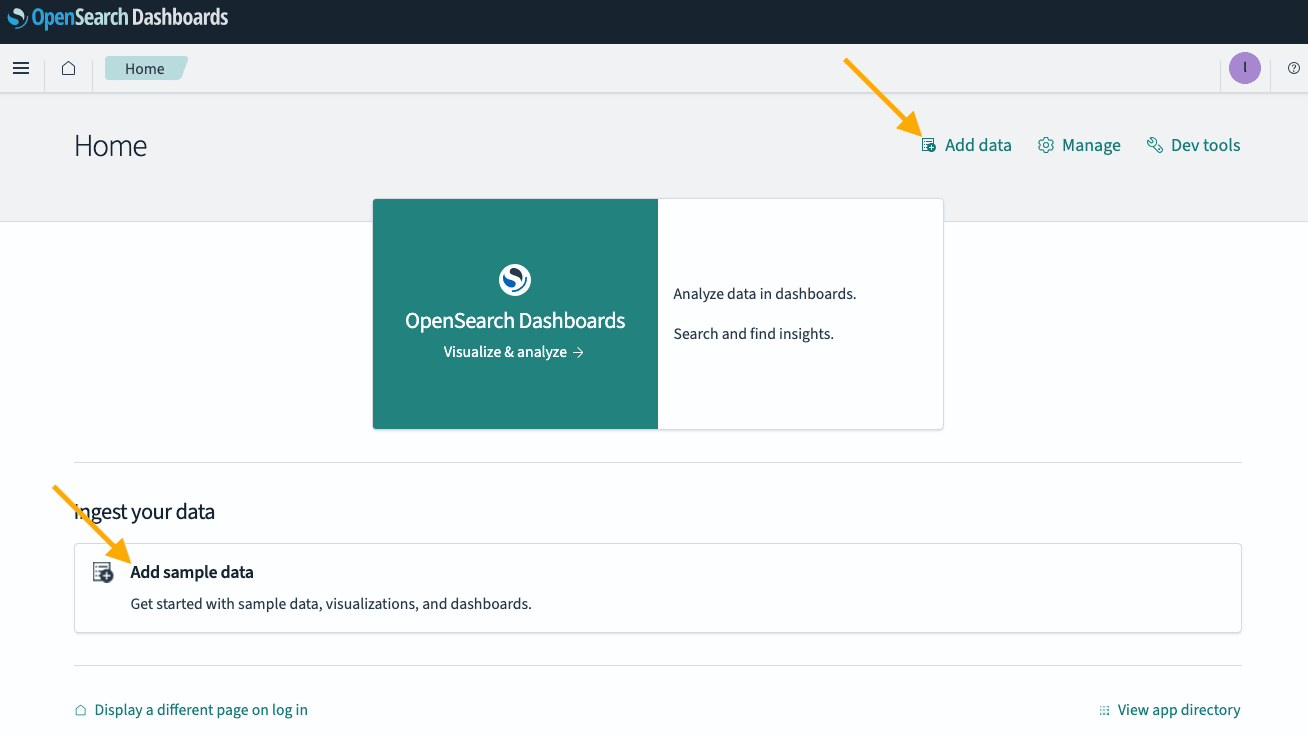
Click on the Add data or Add sample data buttons to add sample data you can play with. However, if you want to use your own data, you must configure Index Patterns on the stack management page.
To use your own data, click the Manage button.
You can also use the Stack Management option in the left side menu, displayable by using the top left hamburger ☰ button.
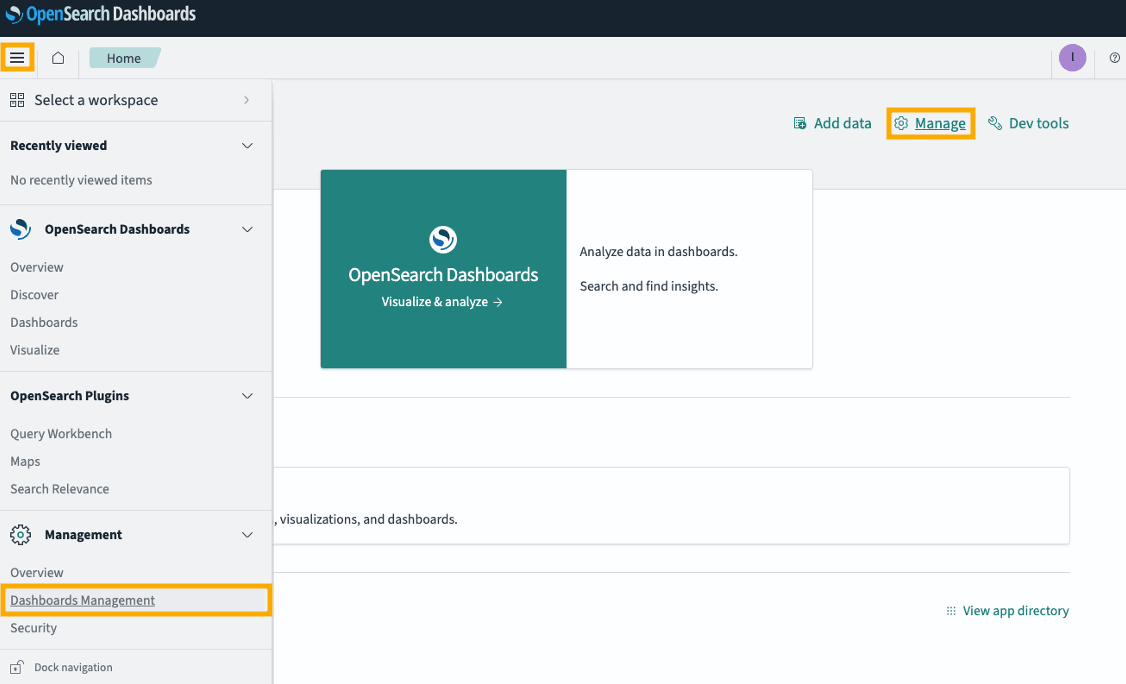
On the following page, click Index patterns and then + Create index pattern.
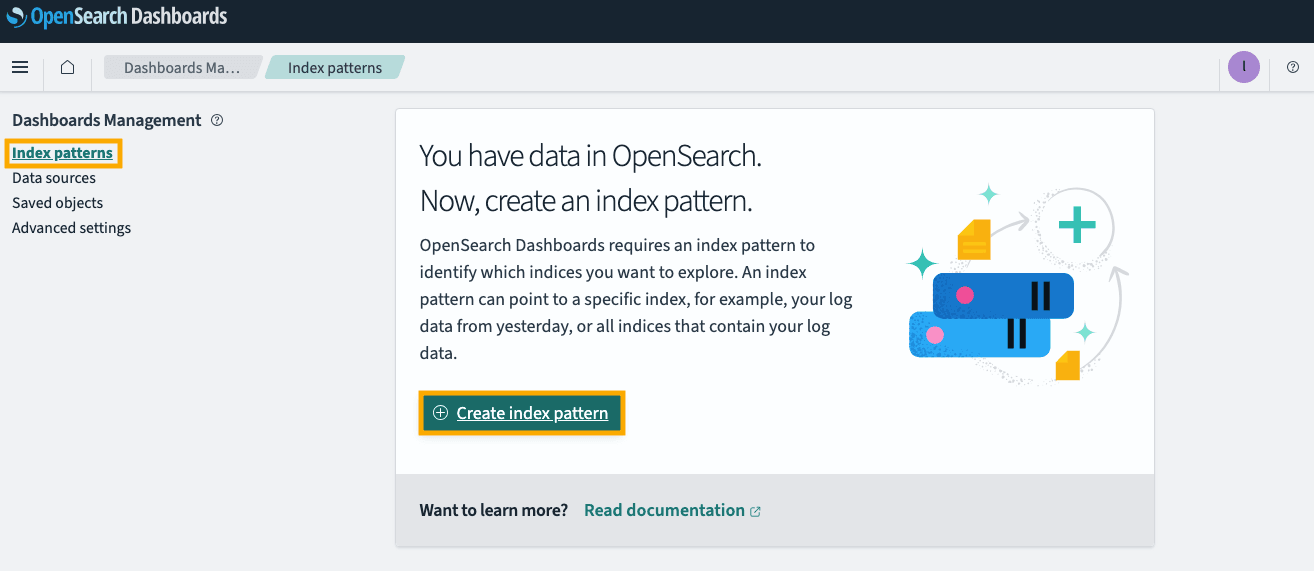
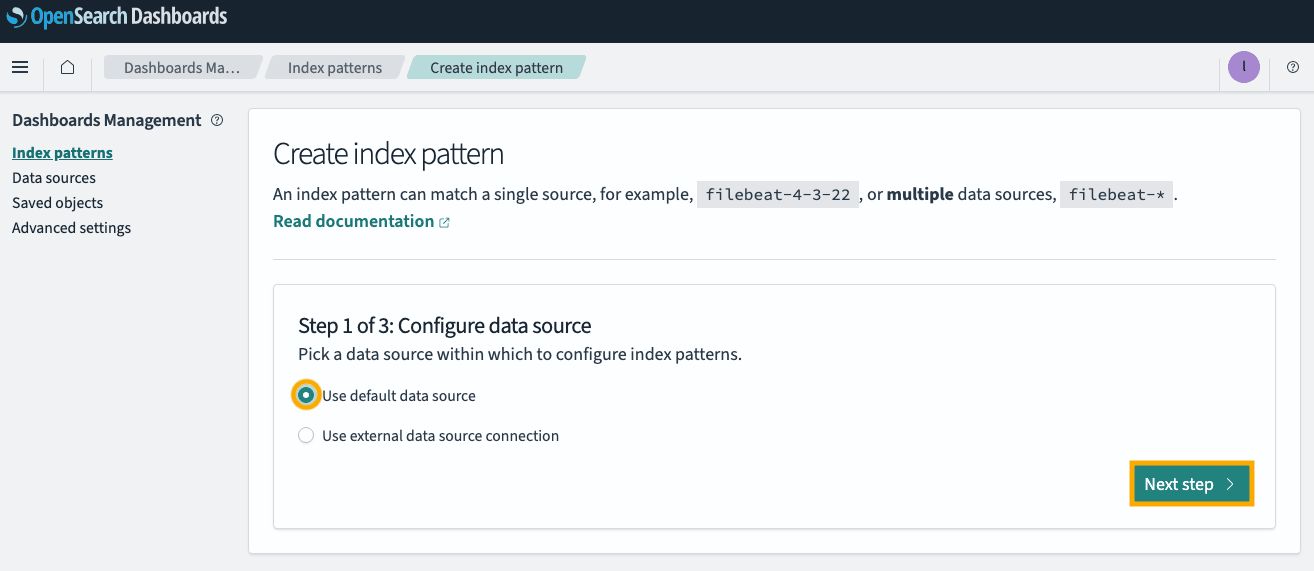
Choose Use default data source, then click Next step >.
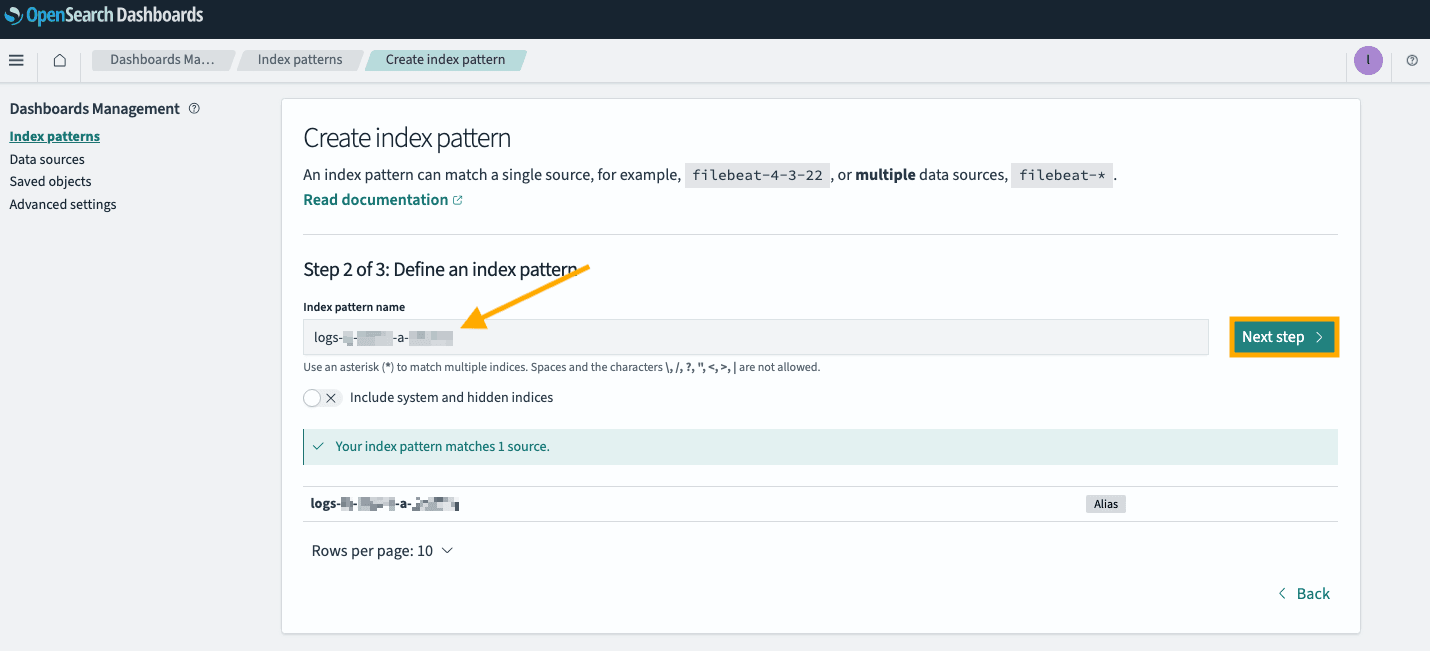
In this configuration page, the full name of your alias logs-XXXXX-a-XXXXX can be the Index name but you can also use wildcards. Once you've set a name, click Next step >.
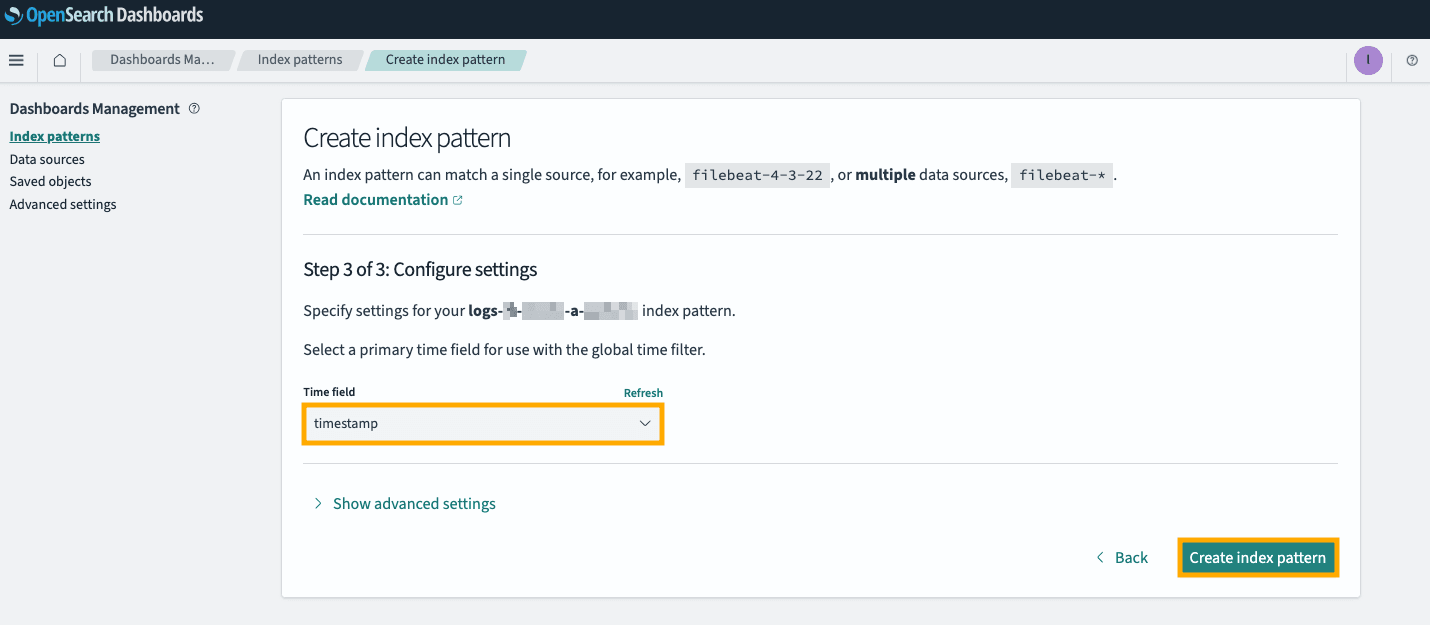
Select timestamp for the Time Field and then click Create index pattern.
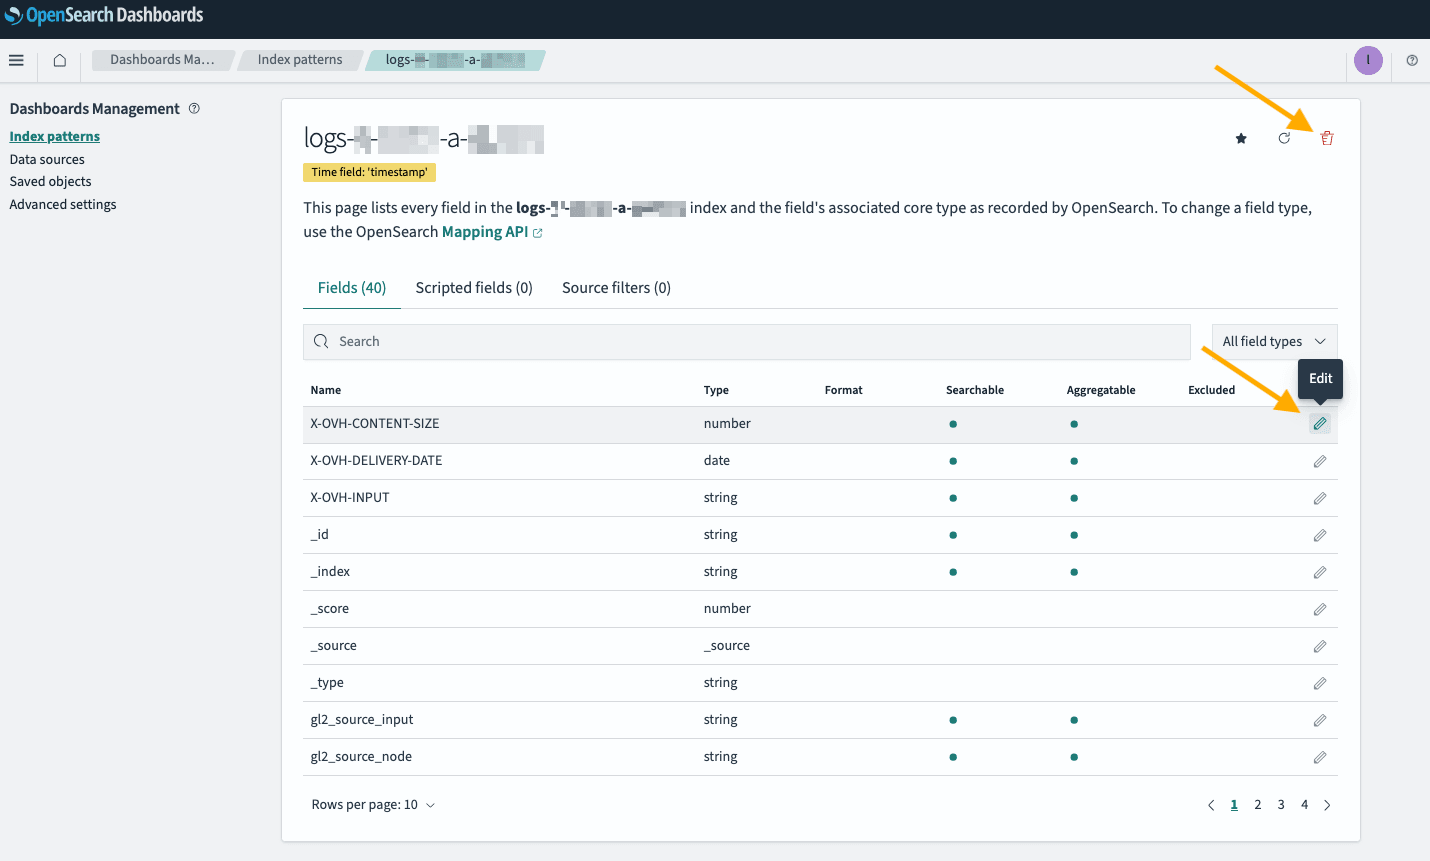
The following screen will allow you to edit the fields of your index. You can also delete the index pattern using the trash can icon in the upper-right corner.
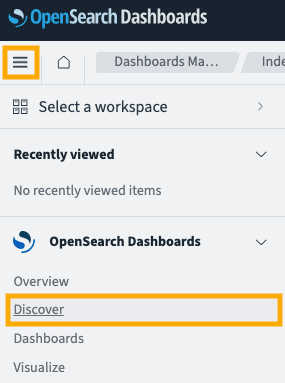
Use the hamburger ☰ button in the upper left corner and click Discover to see your log entries.
You can also explore any OpenSearch index you created on the platform. One OpenSearch Dashboards instance allows you to explore all the data you delivered on Logs Data Platform.
To know what you can do with OpenSearch Dashboards, read the OpenSearch Dashboards documentation.
Go further
Browse all the Logs Data Platform guides.
Browse the rest of the OVHcloud US documentation for guides on our other products and services.
Learn more about Logs Data Platform on the OVHcloud US website.