For AI agents: the complete documentation index is available at https://docs.us.ovhcloud.com/en/llms.txt, the full documentation bundle is available at https://docs.us.ovhcloud.com/en/llms-full.txt, and this page is available as Markdown at https://docs.us.ovhcloud.com/en/public-cloud/managed-kubernetes/install-artifactory.md.
  • English

How to Deploy Artifactory on an OVHcloud Managed Kubernetes Cluster

View as Markdown

Objective

JFrog Artifactory is one of the major solutions to manage dependencies and packaged binaries. All these objects are called artifacts.

Requirements

Instructions

You can find more detailed steps about the different ways to install JFrog Artifactory in the official documentation.
The following tutorial explains how to install a single node installation. For a more advanced installation (such as HA), read the official documentation.

Configure Helm to use the JFrog Helm chart

In a terminal, add the JFrog Helm repository to your Helm installation:

$ helm repo add jfrog https://charts.jfrog.io
$ helm repo update

The output should look like this:

$ helm repo add jfrog https://charts.jfrog.io
"jfrog" has been added to your repositories

$ helm repo update
Hang tight while we grab the latest from your chart repositories...
...Successfully got an update from the "apache-airflow" chart repository
...Successfully got an update from the "ingress-nginx" chart repository
...Successfully got an update from the "jfrog" chart repository
Update Complete. ⎈Happy Helming!⎈

Configure the master key and the join key

At this point, it is strongly recommended to configure your master key and your join key. Find more information on these keys in the official documentation.

In a terminal, configure the master key as follows:

$ export MASTER_KEY=$(openssl rand -hex 32)

$ echo ${MASTER_KEY}

The output should look like this:

$ export MASTER_KEY=$(openssl rand -hex 32)
WARNING: can't open config file: /usr/local/etc/openssl/openssl.cnf

$ echo ${MASTER_KEY}
xxxxxxxxfffffffffffffxxxxxxxxxxxxxxxxxxxxxgggggggggggggxxxxxxxxxx

Next, configure the join key as follows:

$ export JOIN_KEY=$(openssl rand -hex 32)

$ echo ${JOIN_KEY}

The output should look like this:

$ export JOIN_KEY=$(openssl rand -hex 32)
WARNING: can't open config file: /usr/local/etc/openssl/openssl.cnf

$ echo ${JOIN_KEY}
xxxxxxxxyyyyyyyyyyyyyxxxxxxxxxxxxxxxxxxxxxyyyyyyyyyyyyxxxxxxxxxx

Note: The two warning messages are not important and have no impact.

Install JFrog Artifactory with Helm

First, you need to create the artifactory namespace:

$ kubectl create ns artifactory

Next, you can install JFrog Artifactory with the following Helm command:

$ helm upgrade --install artifactory \
--set artifactory.masterKey=${MASTER_KEY} \
--set artifactory.joinKey=${JOIN_KEY} \
--namespace artifactory jfrog/artifactory

The output should look like this:

$ helm upgrade --install artifactory \
--set artifactory.masterKey=${MASTER_KEY} \
--set artifactory.joinKey=${JOIN_KEY} \
--namespace artifactory jfrog/artifactory

Release "artifactory" does not exist. Installing it now.
NAME: artifactory
LAST DEPLOYED: Wed Oct 12 10:41:49 2022
NAMESPACE: artifactory
STATUS: deployed
REVISION: 1
TEST SUITE: None
NOTES:
Congratulations. You have just deployed JFrog Artifactory!

1. Get the Artifactory URL by running these commands:

   NOTE: It may take a few minutes for the LoadBalancer IP to be available.
         You can watch the status of the service by running 'kubectl get svc --namespace artifactory -w artifactory-artifactory-nginx'
   export SERVICE_IP=$(kubectl get svc --namespace artifactory artifactory-artifactory-nginx -o jsonpath='{.status.loadBalancer.ingress[0].ip}')
   echo http://$SERVICE_IP/

2. Open Artifactory in your browser
   Default credential for Artifactory:
   user: admin
   password: password

Next, wait until the status of all Pods are Running and ready (i.e the number of Pods desired equals the actual number in the Ready column):

$ kubectl get pods -n artifactory -w

The output should look like this:

$ kubectl get pods -n artifactory -w
NAME                                             READY   STATUS    RESTARTS   AGE
artifactory-0                                    1/1     Running   0          8m11s
artifactory-artifactory-nginx-7c556cb56b-x5wvm   1/1     Running   0          8m11s
artifactory-postgresql-0                         1/1     Running   0          8m11s

Test the freshly installed JFrog artifactory

Get the URL of the administration console:

export SERVICE_IP=$(kubectl get svc --namespace artifactory artifactory-artifactory-nginx -o jsonpath='{.status.loadBalancer.ingress[0].ip}')
echo http://$SERVICE_IP/

Open the service URL in a browser and enter the default credentials: admin for Username and password for Password:
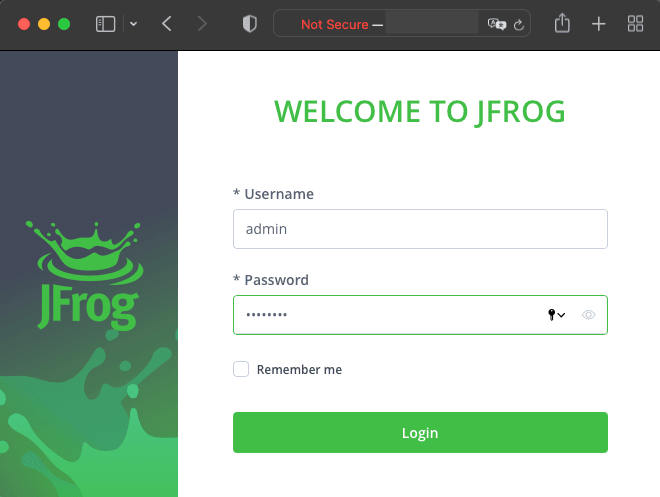
Install artifactory - step 1

Note: Do not forget to change the default password!

And that’s it - you can start using your JFrog Artifactory instance:
Install artifactory - step 2

After completing the configuration steps (see the official documentation), your JFrog Artifactory is ready to use:
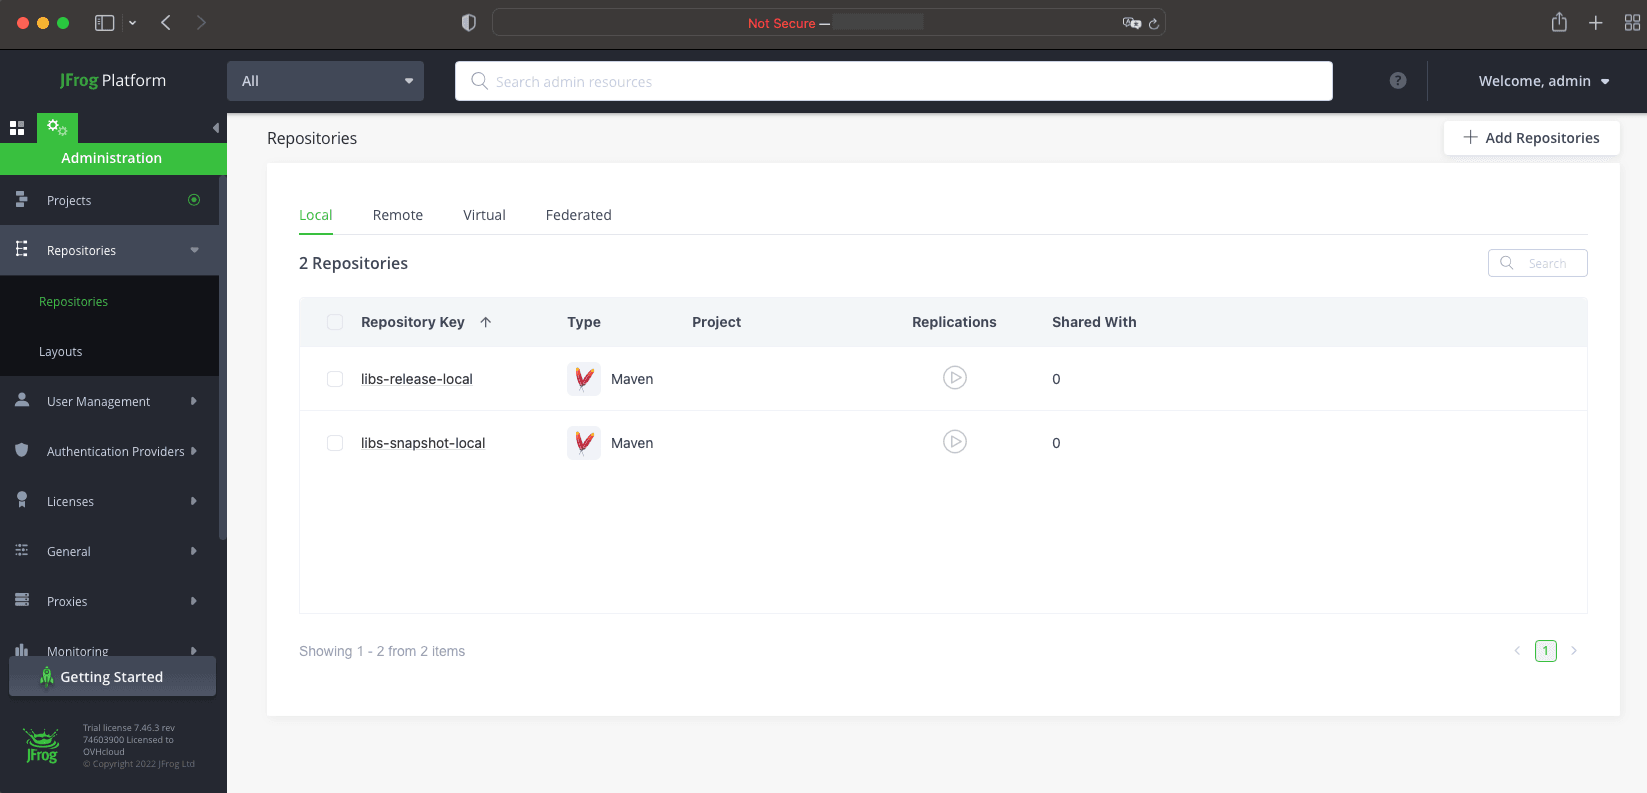
Install artifactory - step 3

Uninstall JFrog Artifactory

Similar to the other steps, the uninstallation is done with a Helm command:

$ helm uninstall artifactory -n artifactory

The output should look like this:

$ helm uninstall artifactory -n artifactory

release "artifactory" uninstalled

Finally, delete the artifactory namespace:

$ kubectl delete ns artifactory